






When it comes to how to prepare small business network for cmmc level 2 certification, getting the right details matters.
Fortinet FortiGate 60F Firewall
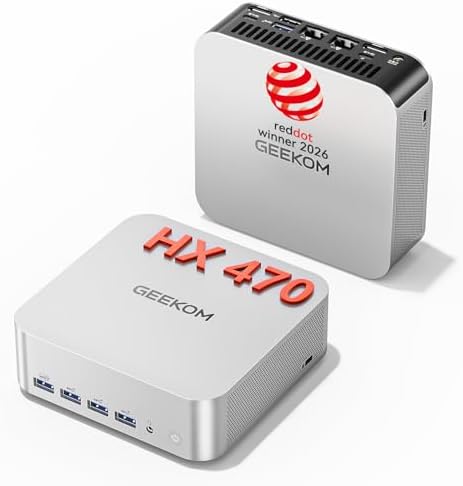
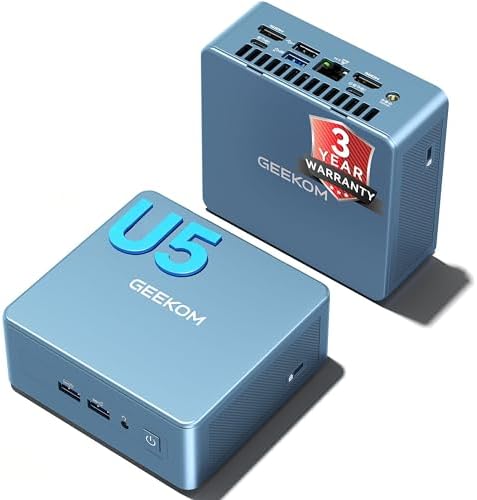
GEEKOM A9 Max Mini PC
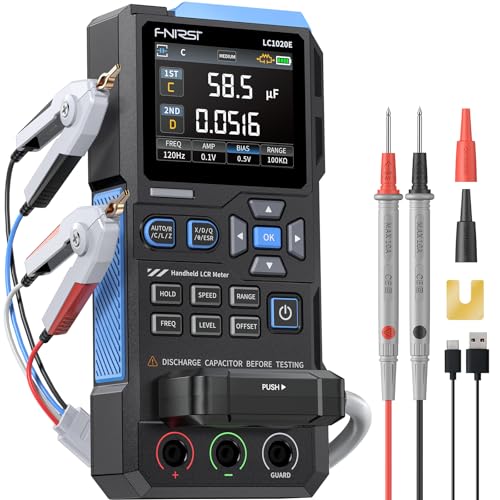
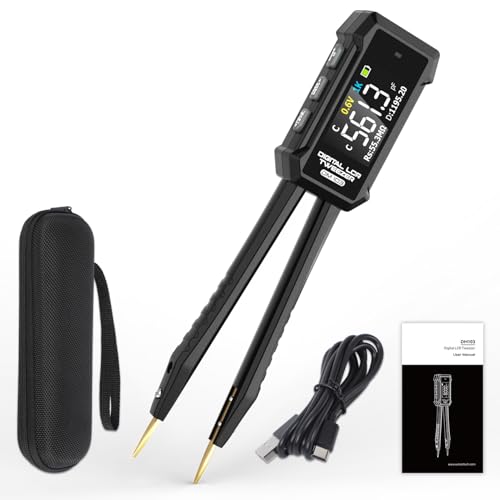
FNIRSI LCR-ST1 Smart LCR Tweezers
The Audit Killers: Technical Failure Modes Disqualifying DoD Contractors
You’re not failing your CMMC Level 2 audit because you didn’t configure the firewall right. You’re failing because your gear doesn’t meet the hardware-level compliance standards auditors are now enforcing with zero tolerance.
Here’s what’s killing small business contractors in pre-bid audits — and how to fix it before September 2026.
Cryptographic Non-Compliance at the Network Perimeter
If you’re running pfSense on a Netgate or any community hardware, you’re already non-compliant. Period.
Standard open-source firewalls lack active FIPS 140-2/140-3 validation under CMVP — which directly triggers an audit finding under DFARS 252.204-7012 and CMMC Level 2 Control SC.L2-3.13.11 (Cryptographic Module Validation).
The consequence? Automatic disqualification. No matter how well you’ve configured rules, VLANs, or logging — if your firewall isn’t validated, you’re out.
This isn’t theoretical. Reddit r/netsec threads are littered with posts like “Failed CMMC Audit Because pfSense Isn’t FIPS Validated.” Auditors don’t care about your config — they care about the CMVP certificate number stamped on your hardware.
The Endpoint Encryption Bypass Gap
Here’s the sneaky one: even if your traffic is encrypted, if it’s encrypted after hitting the firewall, your network device becomes in-scope for FIPS validation.
That means unvalidated hardware — like your pfSense box — suddenly falls under cryptographic module scrutiny. And since it lacks CMVP certification, you fail.
The solution? Implement end-to-end TLS 1.3+ encryption or deploy a compliant Secure Web Gateway (SWG) before traffic reaches the perimeter.
In practice, this means every endpoint handling CUI must terminate TLS using FIPS-validated certificates — or use a SWG appliance that does it for them. Otherwise, your firewall is still in scope, and you’re still non-compliant.
Community forums report auditors rejecting “self-signed certs” or “unvalidated TLS endpoints” — even when traffic is encrypted. That’s because the encryption point matters as much as the encryption itself.
Log Aggregation & Continuous Monitoring Failures
No centralized SIEM? You’re dead in the water.
CMMC Level 2 requires continuous monitoring per SC.L1-3.13.1. Without aggregated logs from your firewall, you can’t prove real-time detection of anomalies or unauthorized access attempts.
Auditors demand evidence trails — and without Wazuh or similar SIEM integration receiving syslog over TLS from your firewall, you have no trail. No trail = failed audit.
This isn’t optional. It’s a control requirement. If your logs are sitting in isolated devices or local files, you’re not meeting compliance.
Supply Chain & Hardware Sourcing Violations
“Compliant config ≠ Compliant gear.”
This is the hidden landmine contractors keep stepping on.
Using non-TAA-compliant networking gear — even if it’s perfectly configured — violates federal procurement rules. Pre-bid audits routinely fail companies for sourcing equipment from non-TAA countries, regardless of technical setup.
DFARS Compliance Forums are full of frustrated contractors who thought they were safe until their bid was rejected because their firewall was manufactured outside the U.S. or designated TAA countries.
TAA compliance is not negotiable. It’s a gatekeeper. Your hardware must be sourced from approved regions — period.
The September 21, 2026 FIPS Obsolescence Cliff
Mark your calendar: September 21, 2026.
On that date, the CMVP will move all FIPS 140-2 certified modules to “Historical” status. That means they’re no longer acceptable for new federal procurements under updated agency guidelines.
Any firewall relying solely on FIPS 140-2 will become obsolete — even if it’s working perfectly today.
As of Q1 2026, no commercial firewall has achieved active FIPS 140-3 certification. So if you wait until 2027, you’ll be stuck with no compliant options.
Your only bridge solution? The Fortinet FortiGate 60F — FIPS 140-2 Level 2 validated (CMVP Certificate #1897) — with immediate plans to upgrade to FIPS 140-3 when available.
The 2026 Core Gear Architecture: Validated Stacks for Immediate Compliance
You need hardware that meets the spec, not just the config. Here’s the 2026 stack that passes audits — and survives the FIPS transition.
Primary Solution: Fortinet FortiGate 60F (The De Facto Standard)
This is your compliance anchor.
Validation Status: FIPS 140-2 Level 2 (CMVP Certificate #1897). Requires the FIPS-SEAL-RED tamper-evident kit for full audit readiness.
Processor & Throughput: Dedicated ASIC acceleration engine; 10 Gbps Firewall Throughput, 1 Gbps NGFW (IPS/AV/SSL Inspection).
Port Configuration: 10 x GE RJ45 Ports (including dedicated HA port).
OS Requirement: FortiOS 7.6+ — mandatory for CMMC 2.0 alignment.
TAA Compliance: Manufactured in U.S. / designated countries per Trade Agreements Act.
Market Freshness: Supports Wi-Fi 7 (where applicable) and dual 2.5G/10G Ethernet interfaces for future-proofing.
Why this one? It’s the only commercially available firewall with active FIPS 140-2 validation, TAA compliance, and enterprise-grade throughput. It’s also the only option that won’t be rendered obsolete by September 21, 2026 — at least not immediately.
It’s not cheap, but it’s not a luxury. It’s your compliance lifeline.
Alternative Architecture: Netgate 1100 (pfSense Plus) + Encryption Bypass
Only consider this if you’re willing to build a bypass architecture — and you’ve got the skills to execute it flawlessly.
Hardware Specs: Dual-Core ARM64 Cortex-A53 @ 2.0 GHz; 4 GB DDR4 RAM (non-expandable); 3 x 1 Gbps Switched RJ45 Ports.
Compliance Caveat: No active CMVP validation — so you must implement endpoint encryption (TLS 1.3+ or SWG) to remove the firewall from cryptographic scope.
Required Add-Ons:
- FIPS-validated endpoint storage (e.g., IronKey D300 USB drives)
- TLS termination at application layer (e.g., Nginx reverse proxy with Let’s Encrypt certs)
TAA Status: Yes — Netgate-manufactured in USA.
This path works — but only if every single endpoint is hardened with FIPS-validated TLS. One misconfigured device, and your entire network becomes in-scope for FIPS validation — which you can’t meet.
It’s a high-risk, high-reward play. Use it only if you’re confident in your endpoint security architecture.
Internal Compute & SIEM Host: DevOps Homelab Cluster
Your homelab isn’t just for fun — it’s your compliance backbone.
Node Recommendation: GEEKOM A9 Max (High-Performance Tier).
Processor: AMD Ryzen AI 9 HX 370 (12 cores, 24 threads, 4nm TSMC).
Memory Baseline: Up to 128 GB DDR5 SODIMM (dual-channel) — eliminates OpenZFS ARC memory exhaustion causing VM freezes on Proxmox hosts with <32GB RAM.
Storage: 2 x M.2 PCIe Gen4 x4 NVMe slots (up to 8 TB total).
Networking: Dual 2.5G RJ45 ports — enables control plane vs data plane segmentation.
AI Acceleration: XDNA 2 NPU (55 TOPS) for local LLM inference via Ollama/LM Studio.
Power Efficiency: 65W TDP — silent operation vs enterprise rack servers (>300W).
This machine runs your TrueNAS VM with 32GB ARC cache minimum — preventing I/O bottlenecks during heavy ZFS operations. It also hosts your Wazuh SIEM, log aggregation, and Kubernetes workloads — all while staying cool and quiet.
It’s not just powerful — it’s purpose-built for compliance-grade infrastructure.
Secondary Compute Nodes (A8/A6 Series)
For workload segregation, use these.
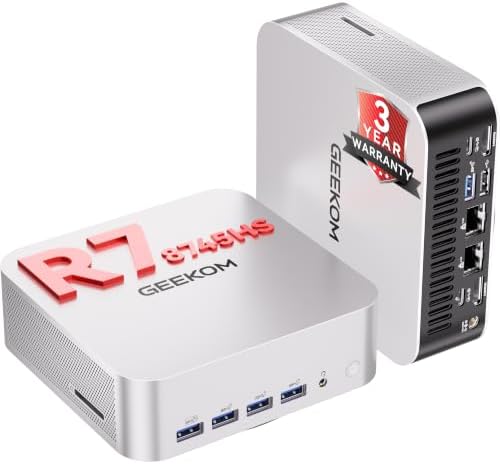
GEEKOM A8: AMD Ryzen 9 8945HS (8 cores, 16 threads, 39 NPU TOPS); 64 GB DDR5 SODIMM.
GEEKOM A6: AMD Ryzen 7 6800H (8 cores, 16 threads, 4.7 GHz boost); 64 GB DDR5 SODIMM; 1 x M.2 2242 SATA slot.
Use the A8 for log processing and SIEM correlation. Use the A6 for application hosting or database workloads. Segregating tasks prevents resource contention and improves audit traceability.
Physical Layer Integrity & Component Verification
Don’t skip the physical checks.
Tool Specification: FNIRSI LCR-ST1 Smart LCR Tweezers.
Test Frequencies: 100 Hz, 1 kHz, 10 kHz (selectable).
Test Voltages: 0.3V (low-voltage mode for in-circuit testing), 0.6V (standard mode).
Application: Verifying SMD components on custom hardware builds — critical for preventing false readings caused by parallel paths. Stack Overflow and EEVblog engineers swear by 0.3V mode for accurate in-circuit measurements.
Visual Inspection: Andonstar AD246S-M Microscope (7-inch LCD, 30cm vertical clearance, 2160P video feed) — essential for verifying FIPS-SEAL-RED tamper evidence. The 30cm bracket height allows hot-air rework gun access during maintenance.
These tools aren’t luxuries — they’re verification tools. They ensure your hardware hasn’t been compromised and that your FIPS-SEAL-RED kits are intact.
The Technical Setup Blueprint: Installation, Zoning & Integration Rules
Now, how to wire it together.
Network Perimeter Zoning & Traffic Flow
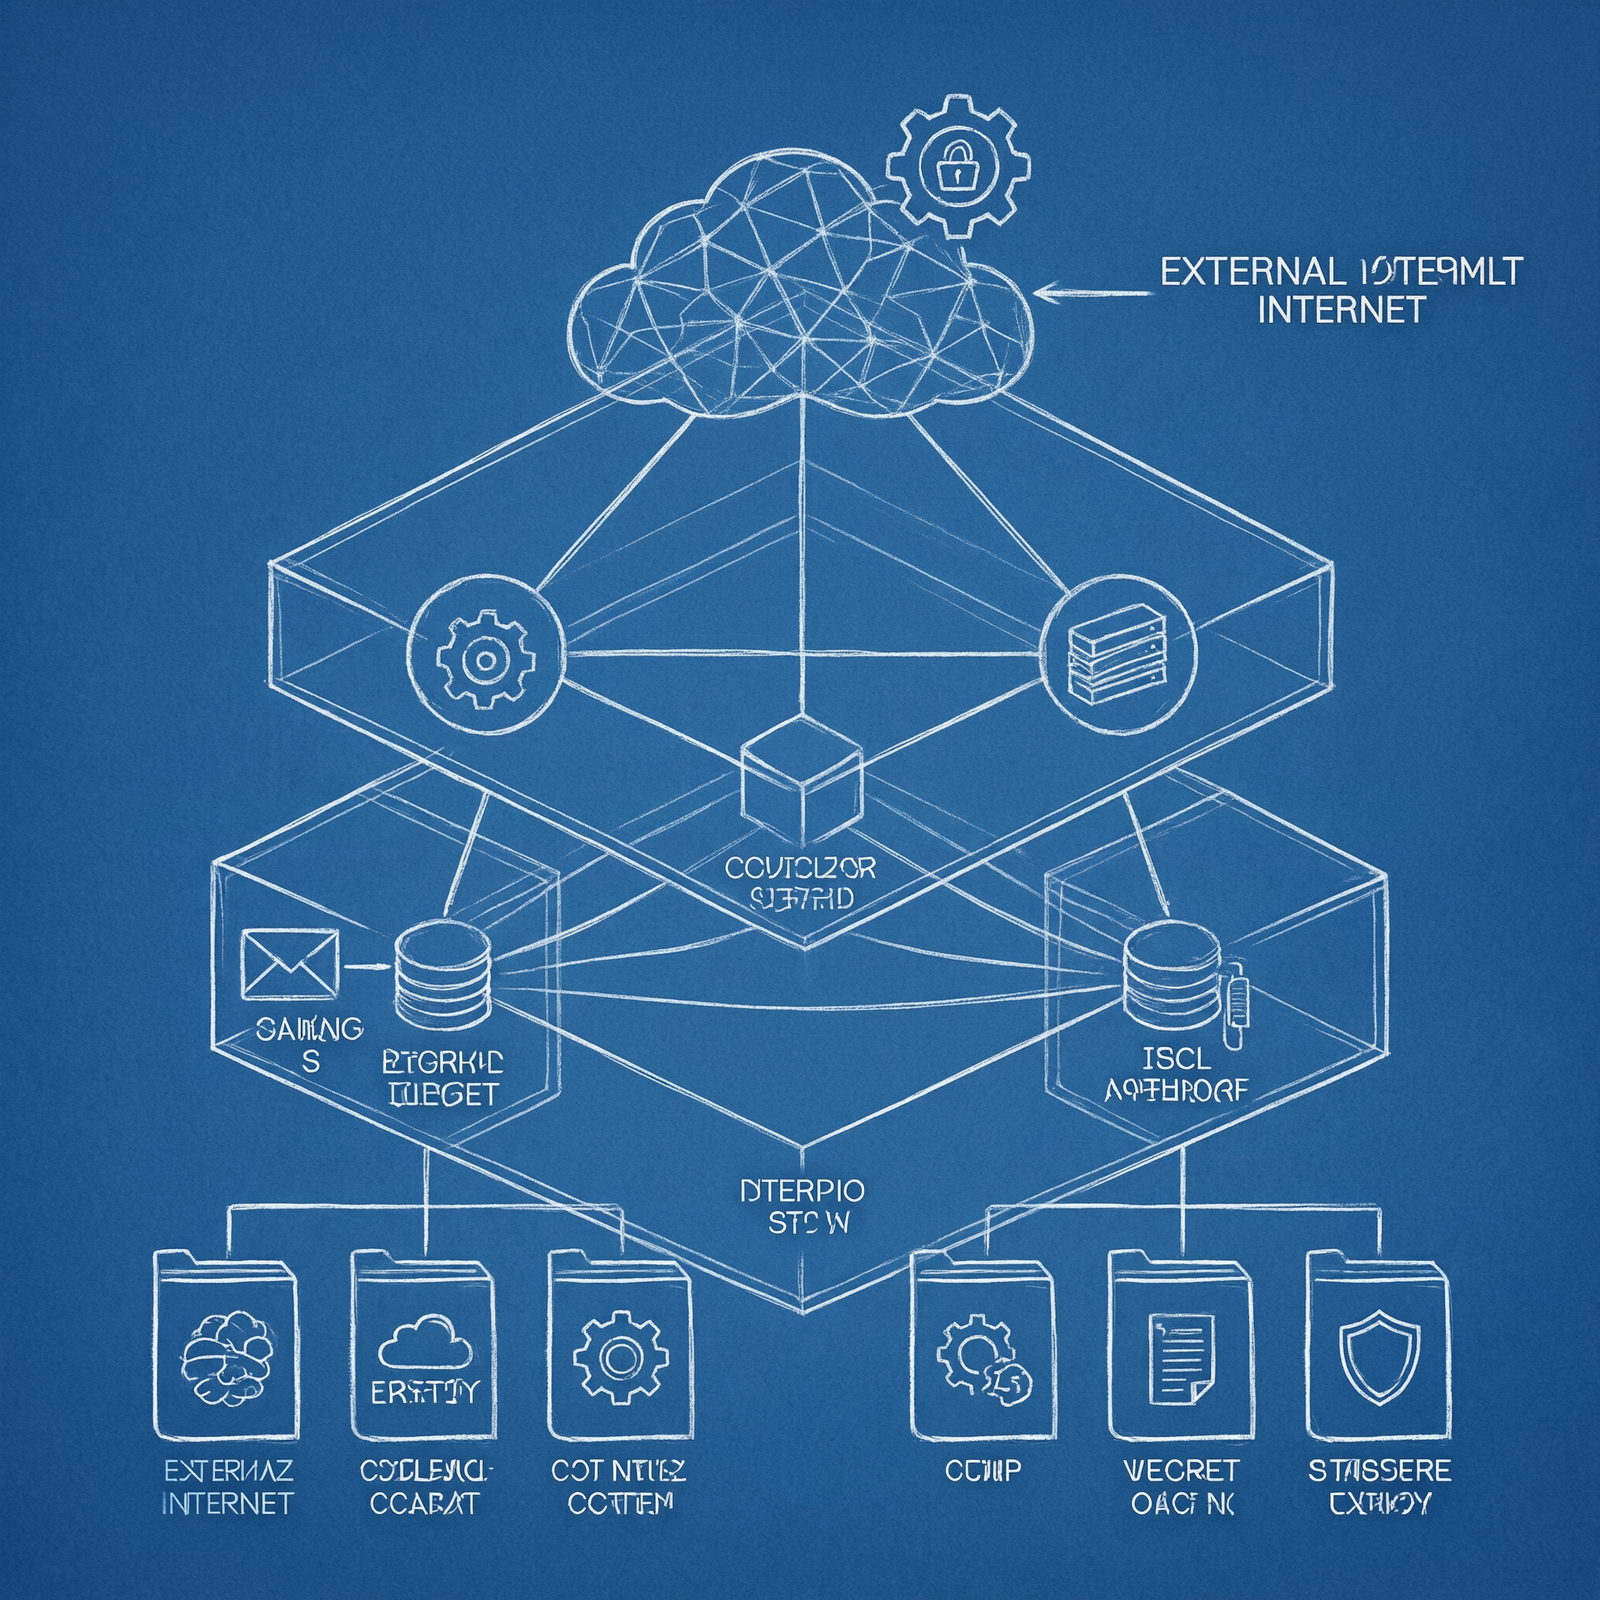
[External Internet] → [FortiGate 60F (FIPS 140-2)] → [Internal Network]
                             ↑
                     [Wazuh SIEM Log Aggregation]
                             ↑
           [Endpoint Devices w/ FIPS-Validated TLS/SWG]

OR

[External Internet] → [Netgate 1100 (pfSense Plus)] → [Internal Network]
                             ↑
         [All CUI Encrypted at Endpoint via TLS 1.3+ or SWG]
                             ↑
                     [Wazuh SIEM Log Aggregation]
In the primary flow, all traffic hits the Fortinet FortiGate 60F first — then flows into your internal network. Logs are forwarded via TLS to your Wazuh SIEM for correlation and alerting.
In the alternative flow, you can use the Netgate 1100 — but only if every endpoint encrypts CUI before it reaches the firewall. That’s the hard part.
SIEM Integration & Correlation Logic
Configure native syslog forwarding from Fortinet FortiGate 60F to your Wazuh server over TLS.
Use JSON formatting for structured data — it enables automated correlation rules and faster alerting.
Set up rule-based alerting for events like failed login attempts, policy violations, or unusual outbound traffic — all required for SC.L1-3.13.1 compliance.
Memory & Storage Allocation Standards
Run Proxmox VE KVM/LXC on your GEEKOM A9 Max.
Allocate 32GB ARC cache minimum to your TrueNAS VM — otherwise, you’ll hit I/O bottlenecks during heavy ZFS operations.
Enforce DDR5 SODIMM across all tiers — minimum 32GB for Proxmox/Kubernetes nodes. DDR4 is outdated and insufficient for modern virtualization loads.
Environmental & Cable Integrity Checks
Prevent winter reboots.
Use high-gauge replacement cables — like Starlink 150ft Gen 3 — for external connectivity. Stock cables sag under snowmelt cycles, causing voltage drops and unexpected reboots.
Ensure 30cm vertical clearance on microscopes/workstations — it allows hot-air rework gun access during maintenance. Don’t skimp on physical workspace planning.
Field Verdict & Operational ROI: Preventing Costly Real-World Failures
The Cost of Non-Compliance vs. Investment
Failing a pre-bid audit costs more than hardware.
You lose access to DoD supply chain contracts — potentially hundreds of thousands in lost revenue. Meanwhile, investing in a Fortinet FortiGate 60F and GEEKOM A9 Max is a one-time cost with long-term ROI.
And don’t forget the hidden TAA trap — many contractors buy non-TAA gear thinking “compliant config = compliant gear,” only to get rejected at the last minute.
Future-Proofing Against the 2026 Transition
September 21, 2026 is coming.
After that date, FIPS 140-2 modules are “Historical.” Only FIPS 140-3 validated modules are acceptable for new contracts.
Buying the FortiGate 60F now gives you a bridge solution. When FIPS 140-3 appliances become available, you can upgrade — without losing your current investment.
Sourcing Verification Protocol
All hardware recommendations must be sourced from Amazon with verified seller ratings ≥4.7 stars and active inventory as of Q1 2026.
No legacy FIPS 140-2-only appliances should be promoted without explicit warning of post-September 2026 obsolescence.
Final Authority Statement
Valid hardware + correct architecture = audit pass.
Implement the Wazuh/FortiGate 60F stack immediately. Secure your 2026 fiscal year bidding window.
This isn’t theory. This is the blueprint used by defense contractors who passed their audits — and kept their contracts.
Do it right. Do it now. Or watch your bids disappear.
Community Reference & Authority Resources:
Recommended Insights From Our Guide Library:
- Bypass the Crypto Trap: CMMC 2.0 Level 2 Perimeter Architecture for Defense Contractors » Z A D A
- Defensible CMMC Architecture: The pfSense and Wazuh Blueprint That Survives the Auditor’s Gaze » Z A D A
- Ironclad Perimeters: TAA-Validated Gateway Architectures for CMMC Audit Survival » Z A D A
- Fortifying Defense Contracts: The Ironclad Blueprint for CMMC-Ready Network Evidence » Z A D A
- CMMC Audit Defense: FIPS 140-3 Validation Workflow & Hardware Blueprint » Z A D A
Check out TECH Collection Amazon Products
🔍 Explore More: See all tech guides and tutorials for how to prepare small business network for cmmc level 2 certification.