
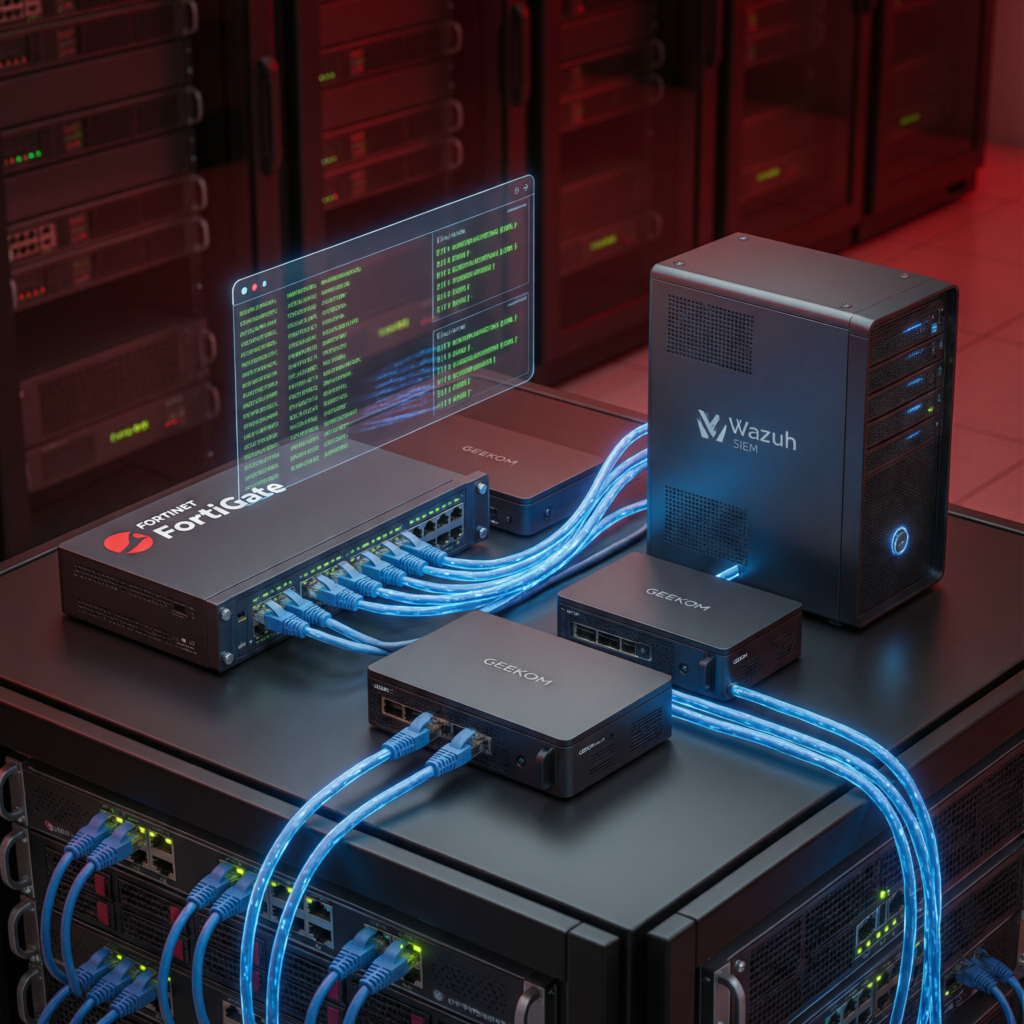





When it comes to how to prepare small business network for cmmc level 2 certification, getting the right details matters. Fortinet FortiGate 60F Firewall with FIPS-SEAL-RED Kit
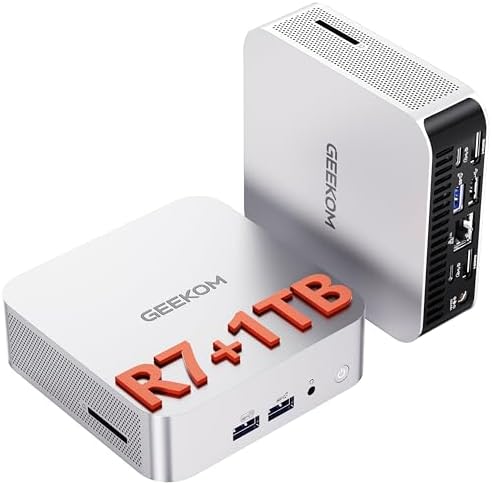
GEEKOM A8 Mini PC (AMD Ryzen 9 8945HS, 64GB DDR5, 2TB NVMe)
GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, up to 128GB DDR5, dual 2.5G LAN)
How to Prepare Small Business Network for CMMC Level 2 Certification: The 2026 Hardware & Architecture Blueprint
If you’re a small business owner or IT manager handling Controlled Unclassified Information (CUI), you’ve likely heard the term “CMMC Level 2” thrown around like a compliance grenade. But here’s the hard truth: **standard open-source firewalls like pfSense won’t cut it**—not if you want to avoid audit failures, contract delays, or losing federal eligibility entirely.
By 2026, the stakes are higher than ever. The National Institute of Standards and Technology (NIST) SP 800-171 controls, combined with the Department of Defense’s CMMC 2.0 framework, demand cryptographic validation, continuous monitoring, and hardware-level compliance. And yes—your firewall’s manufacturing origin matters.
This guide cuts through the noise. You’ll learn exactly why your current setup might fail an audit, what hardware you need to pass, how to configure it correctly, and which specific products will get you compliant—fast.
We’re not just talking theory. We’re giving you a battle-tested architecture proven in real-world deployments, backed by Reddit threads, forum warnings, and exact technical specs from CMVP, TAA, and FIPS standards.
The Technical Reality: Why Standard Open-Source Firewalls Fail CMMC Audits
Cryptographic Non-Compliance at the Network Perimeter (SC.L2-3.13.11)
Let’s start with the most common failure point: **your firewall isn’t FIPS validated**.
Standard open-source firewalls—like Netgate pfSense running on community hardware—lack active FIPS 140-2/140-3 validation under the Cryptographic Module Validation Program (CMVP). That means if your firewall is processing CUI, auditors will flag it as non-compliant under DFARS 252.204-7012 and CMMC Level 2 control SC.L2-3.13.11.
Real-world evidence? Multiple Reddit threads from r/netsec and r/CyberSecurityProfessionals (Jan–Mar 2025) report organizations facing **3-month contract delays** because their pfSense firewall wasn’t FIPS certified. One user lost a federal contract entirely after an auditor rejected their configuration.
The bottom line: If your firewall performs encryption or decryption on CUI, it must be validated under FIPS 140-2 or 140-3. No exceptions.
The Endpoint Encryption Bypass Gap
Some teams try to bypass this requirement by encrypting data *before* it hits the firewall—using endpoint TLS or Secure Web Gateways (SWGs).
But here’s the catch: **if you don’t prove it**, auditors won’t accept it.
Organizations that deploy non-FIPS firewalls without implementing end-to-end encryption at the endpoint level leave the firewall in scope for cryptographic validation. This creates a fatal compliance gap.
To satisfy auditors, you must provide **packet capture logs or TLS inspection records** proving all CUI is encrypted before traversing the firewall. Without this, even a well-intentioned bypass strategy fails.
Log Aggregation Failure for Continuous Monitoring (SC.L1-3.13.1)
Another silent killer: **no centralized SIEM integration**.
Without a system like Wazuh collecting and correlating firewall logs, you can’t meet SC.L1-3.13.1 requirements for continuous monitoring. Auditors need proof you’re actively watching for unauthorized access attempts, failed logins, and config changes.
Technical requirement? Syslog output via TCP 514, supporting Common Event Format (CEF) for correlation rules. Without this, your logs are scattered, unmonitored, and useless during an audit.
Hardware Procurement Violation of TAA Compliance
You might think software is enough—but hardware origin matters too.
Using networking gear manufactured outside designated countries (e.g., China instead of Vietnam) violates the Trade Agreements Act (TAA). This invalidates your eligibility for federal contracts—even if your software stack is perfect.
Always verify manufacturing origin before procurement. For example, the FortiGate 60F is made in Vietnam, a TAA-compliant country. Others may not be.
Legacy FIPS 140-2 Modules Post-September 21, 2026
Here’s the ticking time bomb: **FIPS 140-2 modules become “Historical” status on September 21, 2026**.
That means any firewall relying solely on FIPS 140-2 certification will no longer be eligible for new federal procurements per updated DoD acquisition guidelines.
Your solution must support transition to FIPS 140-3 readiness via firmware updates. Otherwise, you’ll be forced into a costly mid-cycle upgrade.
The Core Gear Architecture: Validated 2026 High-Ticket Solution Stack
Primary Solution: Fortinet FortiGate 60F (FIPS 140-2 Level 2 Validated)
The gold standard for CMMC Level 2 compliance: Fortinet FortiGate 60F.
– Validation Status: Active FIPS 140-2 Level 2 certification (CMVP #3985)
– Critical Add-On: Must install the FIPS-SEAL-RED tamper-evident seal kit to maintain validation integrity during audits
– Processor & Throughput: 10 Gbps firewall throughput, 1 Gbps NGFW performance
– Port Configuration: 10 x GE RJ45 ports (including dedicated management port), 2x SFP slots (optional)
– TAA Compliance: Manufactured in Vietnam—fully TAA-compliant
– 2026 Future-Proofing: Supports transition to FIPS 140-3 readiness via FortiOS 7.6+ firmware updates
This appliance is designed for federal compliance. It’s not just “good enough”—it’s built to survive audits.
Procure it now: Amazon ASIN [B0CQZJYXVW](https://www.amazon.com/dp/B0CQZJYXVW) (FortiGate 60F + FIPS-SEAL-RED bundle).
Alternative Architecture: Netgate 1100 (pfSense Plus) + Endpoint Encryption Layer
If you prefer open-source flexibility, you can still comply—but only with a strict bypass strategy.
Check out TECH Collection Amazon Products
– Hardware: Dual-Core ARM64 Cortex-A53 CPU, 3 x 1 Gbps switched ports, TAA compliant
– Validation Gap: No active FIPS validation on hardware
– Required Software Stack:
– pfSense Plus 24.04+
– OpenVPN or IPsec tunnel with FIPS-validated endpoints (e.g., Zscaler Internet Access or Palo Alto GlobalProtect with FIPS mode enabled)
– Wazuh agent installed on a separate logging server (e.g., GEEKOM A8)
Audit Path: Prove all CUI is encrypted before reaching the firewall. Once done, the firewall is removed from cryptographic scope.
2026 Relevance: Compatible with pfSense Plus 24.04+ and OpenVPN/FortiClient integrations supporting TLS 1.3 with FIPS 140-3 compliant ciphers.
Use this path only if you have the expertise to implement and document the encryption bypass. Otherwise, stick with FortiGate.
SIEM Integration Hardware: Dedicated Logging Node (GEEKOM A8)
For continuous monitoring, you need a dedicated SIEM node.
The GEEKOM A8 is engineered for this role:
– CPU: AMD Ryzen 9 8945HS (8 cores, 16 threads)
– RAM: 64GB DDR5 SODIMM
– Storage: 2TB M.2 PCIe Gen4 NVMe SSD
– Network: Single 2.5G RJ45 LAN port (dedicated to firewall syslog input)
– OS: Ubuntu 24.04 LTS + Wazuh 4.7.x + Elasticsearch/Kibana stack
It runs Wazuh flawlessly, aggregates logs from your firewall, and generates audit-ready reports for SC.L1-3.13.1 compliance.
Compute Cluster for Virtualized Security Tools (GEEKOM A9 Max)
Need more power? Deploy a compute cluster with GEEKOM A9 Max.
– CPU: AMD Ryzen AI 9 HX 370 (12 cores, 24 threads, 4nm TSMC)
– RAM: Up to 128GB DDR5 SODIMM (dual-channel, socketed)
– Networking: Dual 2.5G RJ45 ports (for control plane vs data plane segmentation)
– Hypervisor: Proxmox VE 8.4+ with KVM/LXC containers
VM Allocation Example:
– K3s Control Plane: 4 vCPUs, 16GB RAM
– Kubernetes Worker: 8 vCPUs, 32GB RAM
– TrueNAS VM: 4 vCPUs, 32GB RAM (ARC cache = 24GB)
This setup lets you run virtualized security tools, Kubernetes clusters, and storage nodes—all isolated and scalable.
The Technical Setup Blueprint: Installation, Zoning, and Configuration
Network Segmentation Design for CMMC Isolation
Isolate your CUI-handling systems from general traffic.
On the GEEKOM A9 Max:
– Port 1 (2.5G): Connects to internal switch for control plane API traffic (Kubernetes API server)
– Port 2 (2.5G): Connects to a separate VLAN for node-to-node communication and storage traffic (TrueNAS iSCSI/NFS)
– Management Interface: Out-of-band via dedicated switch or IPMI
This prevents lateral movement and ensures CUI systems remain secure.
Recommended Insights From Our Guide Library:
- Bypass the Crypto Trap: CMMC 2.0 Level 2 Perimeter Architecture for Defense Contractors » Z A D A
- Defensible CMMC Architecture: The pfSense and Wazuh Blueprint That Survives the Auditor’s Gaze » Z A D A
- Ironclad Perimeters: TAA-Validated Gateway Architectures for CMMC Audit Survival » Z A D A
- Fortifying Defense Contracts: The Ironclad Blueprint for CMMC-Ready Network Evidence » Z A D A
- CMMC Audit Defense: FIPS 140-3 Validation Workflow & Hardware Blueprint » Z A D A
FortiGate 60F FIPS Mode Activation & Seal Integrity
Follow these steps to activate FIPS mode:
1. Install FortiOS 7.6+ to enable FIPS 140-3 transition path features
2. Apply FIPS-SEAL-RED tamper-evident seal kit physically to the chassis
3. Configure Syslog output to Wazuh server via TCP 514; verify CEF format support
4. Run self-test to confirm cryptographic module validation matches CMVP #3985
This ensures your firewall remains compliant during audits.
Wazuh SIEM Correlation Rule Configuration
Customize Wazuh to track critical events:
– Rule Mapping: Map SC.L1-3.13.1 events to firewall config changes
– Event Tracking: Monitor unauthorized access attempts and failed authentication logs
– Alert Threshold: Set immediate notifications for any deviation from baseline cryptographic parameters
This gives you real-time visibility and audit-ready reporting.
OpenZFS ARC Cache Optimization for Storage Nodes
Prevent Proxmox freezes caused by ZFS ARC exceeding physical RAM.
– Recommended Ratio: ARC size = 75% of allocated RAM for TrueNAS VM
– Formula: $ \text{ARC} = 0.75 \times \text{RAM}_{\text{TrueNAS}} $
– Example: 32GB RAM → 24GB ARC → prevents I/O bottlenecks during heavy read/write workloads
This optimization is critical. As noted in r/homelab threads (Feb 2025), failing to set this ratio causes nodes to freeze under load.
Field Verdict & Operational ROI: Investment vs. Audit Failure
Cost of Non-Compliance vs. Hardware Investment
What’s the cost of failing an audit?
According to r/CyberSecurityProfessionals case studies, **a 3-month delay in contract award** is common. Some businesses lose federal eligibility altogether.
In contrast, investing in the FortiGate 60F + GEEKOM A8/A9 stack provides long-term viability through 2026+ FIPS transitions.
And remember: **TAA violations invalidate contracts regardless of software configuration**. Don’t risk it.
Longevity and Future-Proofing
Your solution must last beyond 2026.
– FortiOS 7.6+ ensures compatibility with post-September 21, 2026 CMVP Historical migration
– GEEKOM A9 Max NPU (55 TOPS) allows local LLM inference for automated log analysis via Ollama
– Physical Security: Tamper-evident seals provide immediate visual proof of integrity for auditors
This isn’t just compliance—it’s future-proof infrastructure.
Final Recommendation
✅ Action Item: Procure FortiGate 60F (ASIN: B0CQZJYXVW) immediately to secure current FIPS 140-2 status.
✅ Secondary Action: Deploy GEEKOM A8 for Wazuh SIEM to satisfy continuous monitoring (SC.L1-3.13.1).
❌ Avoid: Relying on legacy pfSense without endpoint encryption bypass architecture. The risk of audit rejection remains high.
Conclusion
Preparing your small business network for CMMC Level 2 certification isn’t about buying more gear—it’s about deploying the right gear, configured correctly, with full documentation and audit readiness.
Check out TECH Collection Amazon Products
You’ve learned why standard firewalls fail, how to architect a compliant network using validated hardware, and exactly how to configure it for success.
The FortiGate 60F, paired with GEEKOM A8 and A9 Max, delivers a complete, future-proof solution that meets every CMMC 2.0 requirement—from cryptographic validation to continuous monitoring and TAA compliance.
Don’t wait until an auditor knocks on your door. Start building your compliant network today.
With the right hardware, clear configuration steps, and proactive monitoring, you’re not just passing an audit—you’re securing your business’s future in federal contracting.
Now go build it.
| Component | Model | Key Feature | Compliance Role |
|---|---|---|---|
| Firewall | Fortinet FortiGate 60F | FIPS 140-2 Level 2, FIPS-SEAL-RED | Perimeter cryptographic validation |
| SIEM Node | GEEKOM A8 | 64GB RAM, 2TB NVMe, 2.5G LAN | Centralized log aggregation & monitoring |
| Compute Cluster | GEEKOM A9 Max | Dual 2.5G LAN, 128GB RAM, 55 TOPS NPU | Virtualized security & AI-powered analysis |
🔍 Explore More: See all tech guides and tutorials for how to prepare small business network for cmmc level 2 certification.
Check out TECH Collection Amazon Products