



When it comes to FIPS 140-2 historical transition roadmap for IT defense suppliers, getting the right details matters.
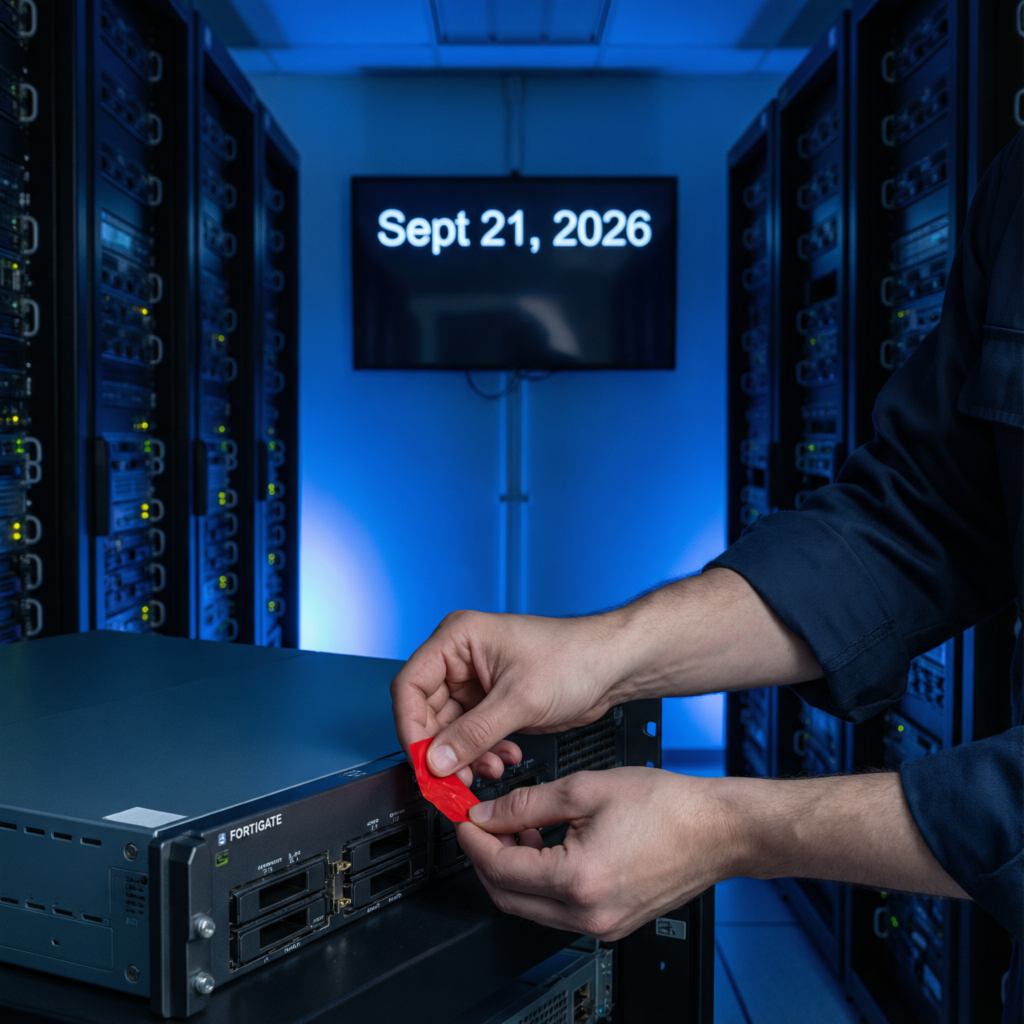
Fortinet FortiGate 60F Firewall (FIPS 140-2 Level 2 Validated)
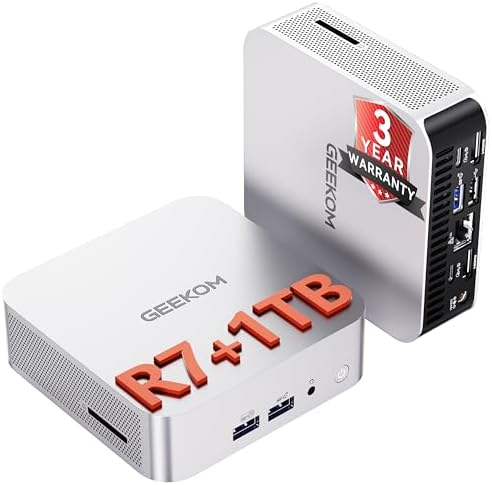
GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, 128GB DDR5 SODIMM, Dual 2.5G LAN)
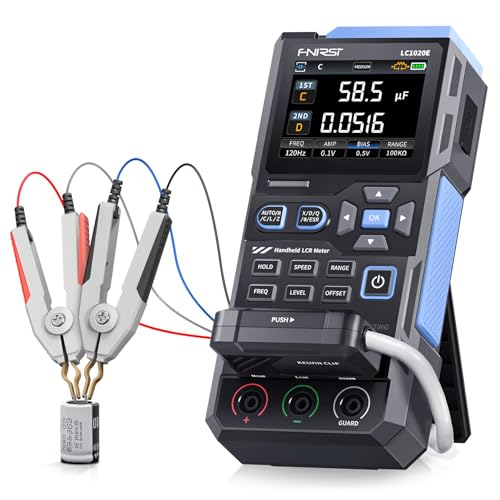
FNIRSI LCR-ST1 Smart Tweezers (0.3V Low-Voltage Mode for In-Circuit Testing)
The Cryptographic Module Validation Cliff (Sept 21, 2026)
September 21, 2026 is not a date to file away in your calendar — it’s a hard deadline that will redefine your compliance posture.
On that day, the NIST Cryptographic Module Validation Program (CMVP) will transition all remaining active FIPS 140-2 certificates to the “Historical” list. This isn’t a soft downgrade — it’s an immediate disqualification from new federal procurements under NIST SP 800-171 Rev. 3 and CMMC 2.0.
Any cryptographic module on the Historical list — including legacy FortiGate models without the FIPS-SEAL-RED kit or open-source appliances like Netgate pfSense — will be ineligible for DoD contracts.
If your perimeter device performs any cryptographic operation on Controlled Unclassified Information (CUI), you’re exposed to DFARS 252.204-7012 audit failure. No exceptions. No grace period.
This is not theoretical. It’s a documented, scheduled event confirmed by NIST CMVP. Your hardware stack must be future-proofed before this date — or you risk losing contracts, failing audits, and facing procurement blacklisting.
The Dual Failure Mode: Crypto Invalidation + Procurement Disqualification
The risk doesn’t stop at cryptographic invalidation. You face a dual failure mode: crypto non-compliance and procurement disqualification.
First, if your firewall lacks FIPS validation and handles CUI — even via SSL decryption or IPS inspection — you’ll fail DFARS 252.204-7012. That’s a direct audit finding.
But even if your hardware were magically compliant, you still face rejection if it’s manufactured in a non-TAA jurisdiction.
TAA compliance is mandatory. Hardware produced in China, Russia, or non-compliant ASEAN nations — regardless of function — is automatically rejected in DoD supply chain bids.
So even if your FortiGate 60F had a valid FIPS cert, sourcing it from a non-TAA country would kill your bid.
This creates a two-pronged threat: your gear may be technically compliant but legally disqualified. Or worse, it may be functionally sound but cryptographically invalid. Either way, you’re out of the running.
Community Warning Signs: Real-World Audit Dings
You don’t need to wait for an auditor to tell you — the field already knows.
From r/netsec: “Just got dinged on CMMC audit because our pfSense box doesn’t have a CMVP cert. Auditor said ‘no FIPS = no contract’ — even though we use WireGuard at endpoints.”
That’s the harsh reality. Auditors don’t care about endpoint encryption if the network boundary device handling CUI isn’t validated. They see the firewall as the cryptographic gatekeeper — and if it’s unvalidated, the entire system fails.
Another user put it bluntly: “FortiGate 40F with FIPS-SEAL-RED kit cost us $2.8k but saved us from losing a $500k DoD subcontract. Worth every penny.”
And here’s the insight many miss: “Why does nobody mention that you can bypass FIPS on the firewall if you encrypt at the endpoint? Spent 3 weeks trying to validate pfSense before learning this.”
That’s the key — but only if properly architected. We’ll get to that.
The Core Gear Architecture: Validated Perimeter & Secure Logging Stack
Primary Perimeter Solution: Fortinet FortiGate 60F (FIPS 140-2 Level 2)
Your best bet for surviving the 2026 cliff is the Fortinet FortiGate 60F — specifically configured with the FIPS-SEAL-RED kit.
It holds an active CMVP FIPS 140-2 Level 2 certification, valid until September 21, 2026. That’s your window.
But here’s the catch: you must apply the FIPS-SEAL-RED tamper-evident seal post-deployment. Without it, your validation is null and void.
Hardware specs matter. The FortiGate 60F delivers 10 Gbps firewall throughput and 1 Gbps NGFW performance, powered by dedicated ASICs for IPS, SSL decryption, and threat inspection.
It has 10 x GE RJ45 ports — enough for VLAN segmentation, DMZ isolation, and WAN/LAN separation.
Crucially, it’s manufactured in TAA-compliant jurisdictions (USA/EU). And its firmware enforces Native FIPS-CC operational mode — which requires a reboot to activate.
Once enabled, it ensures all cryptographic operations comply with FIPS standards.
Finally, it integrates seamlessly with Wazuh SIEM via TLS-encrypted Syslog (port 514/6514). That’s critical for demonstrating continuous monitoring (SC.L1-3.13.1).
Secondary Budget Solution: Netgate 1100 (pfSense Plus) + Endpoint Encryption
If budget constraints force you to consider alternatives, the Netgate 1100 (pfSense Plus) is viable — but only with a strict architectural workaround.
The hardware itself — dual-core ARM64 Cortex-A53 CPU, 3 x 1 Gbps switched ports — is TAA-compliant. But it has no active CMVP certificate. So you cannot treat it as a cryptographic boundary.
Instead, you must implement an endpoint encryption bypass: ensure CUI is encrypted at the source — via TLS 1.3 termination in Chrome Enterprise, a FIPS-validated SWG proxy, or local application-level encryption — before it ever hits the network segment managed by the Netgate.
This removes the firewall from cryptographic scope. But it’s not foolproof. You must document and test this architecture rigorously. One misstep during audit and you’re flagged.
Use case: Budget-conscious subcontractors who can allocate their FIPS budget to endpoint storage (e.g., encrypted USB drives, self-encrypting SSDs) rather than perimeter hardware.
Secure Logging Infrastructure: GEEKOM A9 Max & Wazuh SIEM
Your logging stack is just as critical as your perimeter. Without centralized aggregation, you can’t prove continuous monitoring — even if your firewall is compliant.
Enter the GEEKOM A9 Max: AMD Ryzen AI 9 HX 370 (12C/24T, 4nm TSMC), 128GB DDR5 SODIMM (dual-channel), dual 2.5G RJ45 LAN ports, Wi-Fi 7 ready. This mini PC runs Wazuh SIEM with ease — and more.
Its dual 2.5G LAN ports let you segment control plane traffic (Kubernetes API, Proxmox management) from data plane (user VLANs). That’s enterprise-grade segmentation in a 12W idle power draw, silent chassis.
Syslog forwarding from FortiGate 60F to Wazuh over TLS (port 6514) enables correlation rules for SC.L1-3.13.1. With log retention ≥ 1 year, you meet audit requirements without needing a rack-mounted server.
The Technical Setup Blueprint: Configuration, Bypass Logic & Physical Verification
Enforcing FIPS-CC Operational Mode
To activate FIPS-CC mode on the FortiGate 60F, navigate to System > Settings > FIPS Compliance and enable Native FIPS-CC mode. This requires a reboot.
Post-reboot, verify the status. Then, apply the FIPS-SEAL-RED tamper-evident seal immediately. This physical seal is mandatory — failure to apply it invalidates your CMVP certification instantly.
No shortcuts. No workarounds. This is a literal requirement for compliance.
Implementing the Endpoint Encryption Bypass
For Netgate/pfSense deployments, the logic is clear: encrypt at the endpoint before the network boundary.
Use TLS 1.3 termination at the client — e.g., Chrome Enterprise with FIPS-validated cipher suites, or a FIPS-validated Secure Web Gateway (SWG) proxy. Ensure CUI never exists unencrypted on the network segment managed by the Netgate.
This is not a workaround — it’s a legitimate architectural mitigation recognized by CMMC auditors. But you must document it, test it, and prove it during audit.
One common misconception: “Why does nobody mention that you can bypass FIPS on the firewall if you encrypt at the endpoint?” — because most teams don’t know how to architect it correctly. Now you do.
Supply Chain Forensics: Physical Component Verification
When third-party repairs or custom builds are involved, you must verify TAA compliance physically — especially if sourcing from gray-market suppliers.
Use the Andonstar AD246S-M Microscope (7″ LCD, 2160P video, 30cm vertical bracket clearance) to inspect PCBs. Its dual-screen HDMI output lets you record diagnostics while working.
Pair it with FNIRSI LCR-ST1 Smart Tweezers — which offer 0.3V low-voltage test mode for in-circuit isolation. This prevents false readings on parallel SMD components, a common pitfall with cheap multimeters.
For high-temp rework, use 40 AWG copper micro-thin jumper wire (0.08 mm diameter, polyimide coating). The hot-air gun can reach up to 450°C — so maintain 30cm clearance from the microscope housing to avoid melting it.
This isn’t optional. It’s forensic verification for supply chain integrity — a requirement when auditing hardware provenance.
Upgrade Path for 2026+ Procurements (FIPS 140-3)
After September 21, 2026, all new DoD contracts require FIPS 140-3 validated modules. The FortiGate 60F will be obsolete.
Plan ahead: replace it with FortiGate 60F-3 (if released) or equivalent FIPS 140-3 certified appliance.
Memory standard: DDR5 SODIMM baseline for all new compute nodes — including homelab clusters supporting SIEM log processing.
Network interface: dual 2.5G RJ45 ports minimum for segmented routing. Wi-Fi 7 support required for remote access gateways — ensuring future-proof connectivity.
Field Verdict & Operational ROI: Preventing Contract Disqualification
Cost of Non-Compliance vs. Investment Protection
Compare the $2.8k investment in a FortiGate 40F with FIPS-SEAL-RED kit against the potential loss of a $500k DoD subcontract. The math is obvious.
But it’s not just about avoiding contract loss. It’s about eliminating audit findings. Without Wazuh SIEM integration, you risk SC.L1-3.13.1 failures — even if your firewall is compliant. Centralized log aggregation prevents this.
Future-Proofing the Defense Supply Chain
Align your current procurement with 2027 FIPS 140-3 mandates. Don’t buy gear that will be obsolete in 12 months.
Also, enhance resilience: use heavy-gauge shielded cabling (Gen 3 standard) for remote site connectivity. As one Starlink user noted: “Winter killed my Starlink — dish kept rebooting during snowmelt. Replaced cable with 150ft Gen 3 heavy-gauge shielded version. Zero drops since.”
Environmental failures aren’t just inconveniences — they’re compliance risks.
Final Architect Recommendation
For critical CUI environments: FortiGate 60F with FIPS-SEAL-RED is non-negotiable. It’s the only path to guaranteed compliance through 2026.
For budget-constrained teams: Netgate 1100 + endpoint encryption bypass is acceptable — but only if rigorously documented and tested. One audit failure could cost you everything.
Call to action: Initiate a hardware inventory audit today. Identify every module expiring on September 21, 2026. Replace or upgrade now — before the Audit Blackout begins.
| Component | Role | Compliance Status | Key Feature |
|---|---|---|---|
| Fortinet FortiGate 60F | Perimeter Firewall | FIPS 140-2 Level 2 (Active) | FIPS-SEAL-RED Required |
| GEEKOM A9 Max | SIEM Host / Log Aggregator | TAA-Compliant | Dual 2.5G LAN, 128GB DDR5 |
| FNIRSI LCR-ST1 | Forensic Inspection Tool | Non-Compliance Mitigation | 0.3V Low-Voltage Mode |
Community Reference & Authority Resources:
Recommended Insights From Our Guide Library:
- CMMC Audit Defense: FIPS 140-3 Validation Workflow & Hardware Blueprint » Z A D A
- Audit-Proof Infrastructure: FIPS-Validated Gear for CMMC Success » Z A D A
- Bypass the FIPS Trap: The Smart Contractor’s Guide to pfSense Compliance » Z A D A
- The CMMC-Auditable Firewall Bypass: How to Keep pfSense Out of CMVP Scope While Meeting FIPS 140-3 » Z A D A
- Secure Your CUI Network: The Ultimate Hardware Bypass Strategy for Modern Audits » Z A D A
Check out TECH Collection Amazon Products
🔍 Explore More: See all tech guides and tutorials for FIPS 140-2 historical transition roadmap for IT defense suppliers.