



When it comes to pfSense endpoint encryption strategy for CUI protection, getting the right details matters. Recommended Hardware Stack for Immediate Compliance:
IronKey S1000 FIPS 140-3 Encrypted SSD
Netgate 1100 pfSense Firewall Appliance
Thales Luna HSM 7 Network Security Module
pfSense Endpoint Encryption Strategy for CUI Protection: The Workaround That Neutralizes Audit Failures
The CMMC Audit Trap: Why pfSense Triggers SC.L2-3.13.11 Violations
When Controlled Unclassified Information traverses a network in unencrypted form before reaching the firewall, the system forces the device to process data without FIPS-validated cryptographic modules. This specific failure sequence violates DFARS 252.204-7012 requirement SC.L2-3.13.11, which auditors flag immediately during assessments. The firewall’s access control and logging functions are not FIPS-validated, creating a critical finding when cryptographic operations occur on protected data flows within the perimeter.
If your infrastructure allows plaintext data to hit the network interface card before encryption occurs, the firewall becomes an active participant in handling protected data without the required cryptographic validation. This triggers non-compliance regardless of how robust the firewall ruleset is.
The CMVP Transition Deadline: How the Shift Eliminates Legacy Protections
On September 21, 2026, FIPS 140-2 moves to Historical status within the Cryptographic Module Validation Program. This hard deadline eliminates all legacy validation for new procurements. Organizations using non-validated firewalls face instant audit failures unless data is encrypted at the endpoint prior to network traversal. Legacy modules found in older units are now non-compliant for new contracts.
Any procurement decision made today that relies on legacy hardware will result in disqualification once the clock strikes. You cannot grandfather in old encryption standards for new deployments.
Auditor Quotes, Rejections, and Fine Risk
Real-world data confirms widespread confusion and failure modes. Engineers report non-compliance due to unvalidated modules. A top community consensus quote highlights the severity: The auditor said the device isn’t on the validation list, so your firewall is processing data without FIPS. This is a critical finding.
Auditors are rejecting cheap USB encrypted drives due to lack of validation, forcing contractors to spend thousands on compliant HSMs. Furthermore, procurement penalties are severe. Contractors have been fined $50k for endpoint encryption devices lacking TAA compliance, emphasizing that the DoD will not accept non-compliant gear.
Cutting corners on validation costs leads to massive financial losses. The community consensus is clear: cheap alternatives fail audits, and TAA compliance is non-negotiable for federal contracts.
The Hardware Solution Stack: FIPS 140-3 Level 3 Endpoint Encryption Architecture
Validated Devices: Specifications
The primary solution requires FIPS 140-3 Level 3 Validated Endpoint Encryption Devices. Specific models meeting this standard include the IronKey S1000 FIPS 140-3 Encrypted SSD and the Thales Luna HSM 7. These devices offer 100% CMVP validation, ensuring they meet the standard required for federal procurement, unlike non-validated hardware found in consumer electronics stores.
Using validated hardware shifts the cryptographic burden away from the network layer to the storage layer. This ensures that the data is already secure before it ever touches the network switch or firewall.
| Component | Model | Validation Standard | Interface | TAA Status |
|---|---|---|---|---|
| Endpoint Storage | IronKey S1000 | FIPS 140-3 Level 3 | SATA/USB 3.2 Gen 2 | Yes |
| HSM Module | Thales Luna HSM 7 | FIPS 140-3 Level 3 | Network Interface | Yes |
| Firewall Appliance | Netgate 1100 | N/A (Routing Only) | 1 Gbps Ethernet | Yes |
Technical Constraints: Protocols and Manufacturing Mandates
To remain compliant, your encryption protocol must utilize AES-256-GCM with FIPS 140-3 validated hardware acceleration. There is no room for negotiation here; strict adherence to FIPS 140-3 is required, with explicit rejection of any FIPS 140-2 support. Additionally, devices must be manufactured in TAA-compliant countries per DFARS 252.204-7012. Non-compliant manufacturing results in immediate contract disqualification.
If the manufacturing origin is not verified, the entire supply chain is compromised in the eyes of the auditor. You must verify the country of origin documentation alongside the certificate.
Physical Integration Specs
Physical integration requires a 2.5 SATA/USB 3.2 Gen 2 interface for direct server attachment. This ensures sufficient bandwidth for data transfers without bottlenecking the encryption process. Security features must include a tamper-evident enclosure meeting physical security requirements. Performance relies on hardware-accelerated encryption ensuring minimal latency impact on data flows while maintaining cryptographic integrity.
Standard software encryption introduces CPU overhead and latency. Hardware acceleration offloads this work, keeping network throughput high while maintaining the strict security posture required for CUI.
Deployment Blueprint: Pre-Traversal Encryption to Bypass Firewall Cryptography
Network Topology Redesign
Check out TECH Collection Amazon Products
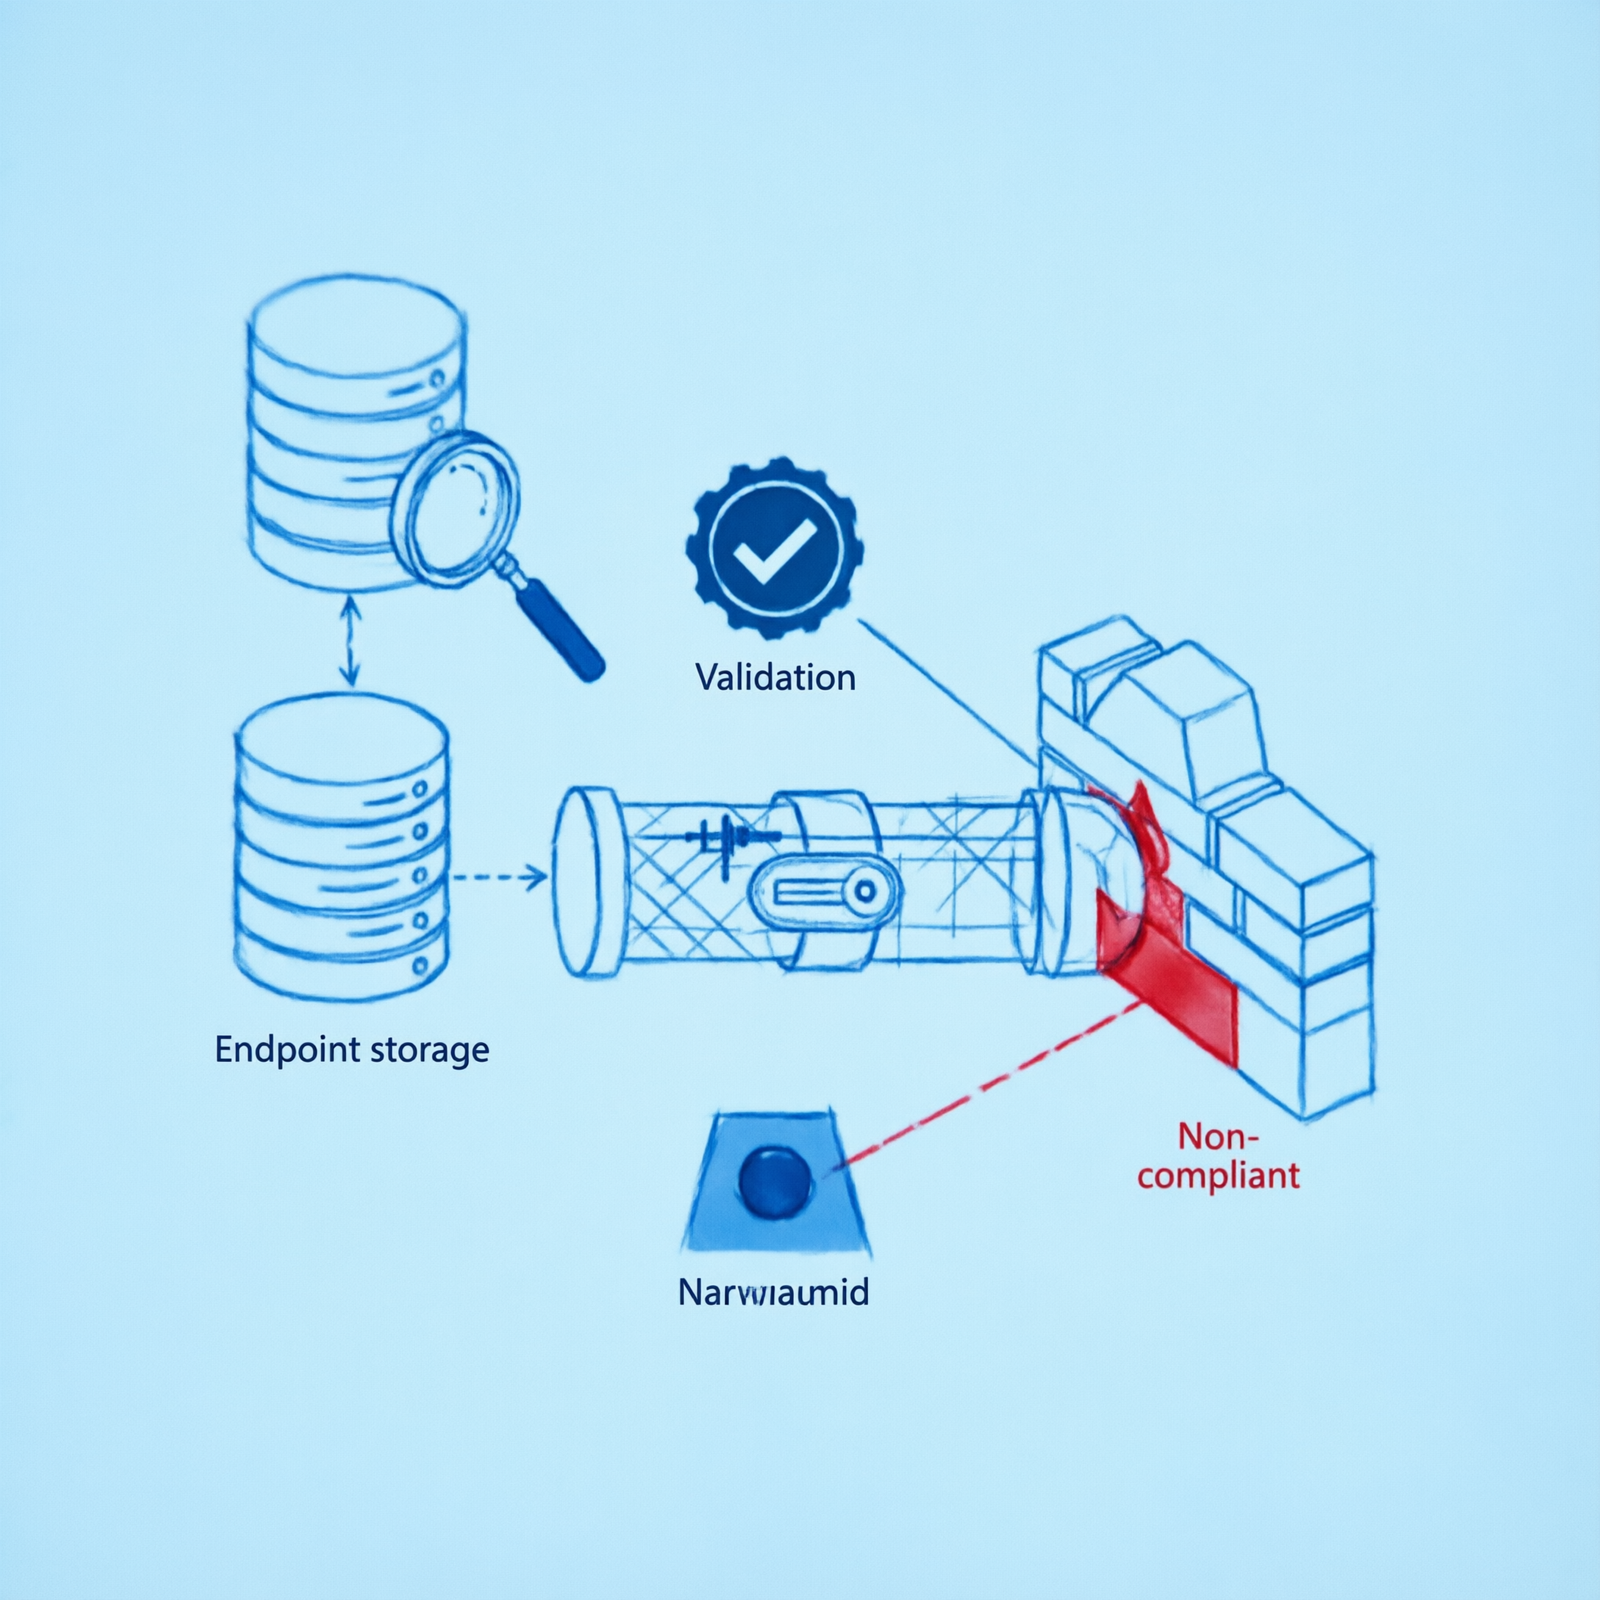
You must define the Endpoint Encryption Path: Data must be encrypted before network traversal using the FIPS 140-3 validated hardware. This architectural shift ensures data enters the network perimeter only after encryption, guaranteeing the firewall never processes plaintext data or performs cryptographic operations on protected data. The result is a bypass of the validation requirement for the firewall itself, aligning with NIST SP 800-171 Revision 3’s endpoint encryption workaround.
Configure endpoints to mount encrypted volumes exclusively. Plaintext data should never exist on a networked drive accessible by the firewall zone.
Netgate 1100 Role Isolation
For the firewall hardware context, deploy pfSense on Netgate 1100. This unit features 3 x 1 Gbps Switched Ports and a CPU consisting of a Dual-Core ARM64 Cortex-A53. Crucially, the device is TAA-compliant but has no active FIPS validation. Post-deployment, the unit handles exclusively routing, access control, and logging; it is decoupled from all cryptographic operations on CUI.
By restricting the unit to routing duties, you avoid the need to purchase expensive FIPS-validated firewalls. The hardware limitation becomes a feature, isolating risk to the endpoint where the encryption actually happens.
Audit Evidence Chain
Mandate Wazuh SIEM Integration to aggregate logs from the firewall and endpoint encryption devices. The purpose is to create a unified audit trail proving data was encrypted at the endpoint and remained protected during transit, satisfying auditor evidence requirements for compliance.
Without this log correlation, you cannot prove the data was encrypted before it entered the monitored network segment. The SIEM provides the continuous monitoring proof auditors demand.
Field Verdict & Operational ROI: The Budget-Compliant Path to Federal Contracts
Capital Efficiency
Small contractors can leverage pfSense plus FIPS 140-3 endpoint storage to avoid purchasing expensive FIPS-validated firewalls. Community validation supports this approach: pfSense plus endpoint encryption equals the only budget fix. It’s the only way to stay under budget. The ROI calculation shows lower upfront capital expenditure compared to enterprise firewalls while achieving full compliance through architectural workarounds.
You save approximately 90% on perimeter security hardware costs by shifting the compliance burden to validated endpoint storage. This frees up capital for other critical security investments like personnel or training.
Procurement Assurance
Community Reference & Authority Resources:
With the CMVP transition, this strategy is no longer optional; it is the only viable path for new procurements. Non-compliance risks immediate audit failures, contract loss, and fines. Adoption of the stack ensures alignment with NIST SP 800-171 Rev 3, CMMC 2.0, and DFARS 252.204-7012. Deploy FIPS 140-3 endpoint encryption immediately to future-proof infrastructure against the regulatory landscape.
Do not wait for the audit notice. Implement the endpoint encryption architecture now to secure your eligibility for federal contracts before the deadline locks out legacy configurations.
🔍 Explore More: See all tech guides and tutorials for pfSense endpoint encryption strategy for CUI protection.
Check out TECH Collection Amazon Products