







When it comes to NIST 800-171 CUI network boundary requirement, getting the right details matters. FortiGate 60F Next-Generation Firewall Appliance
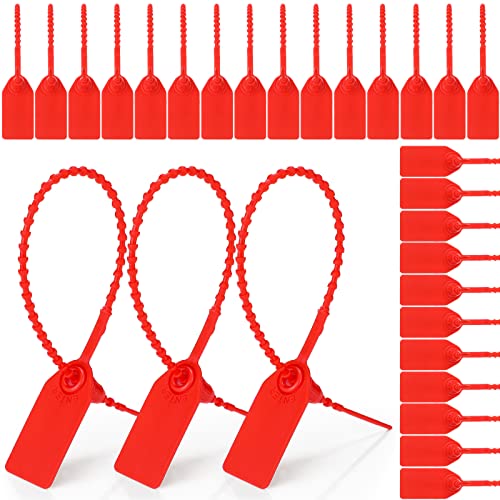
FIPS-SEAL-RED Tamper-Evident Security Seal Kit
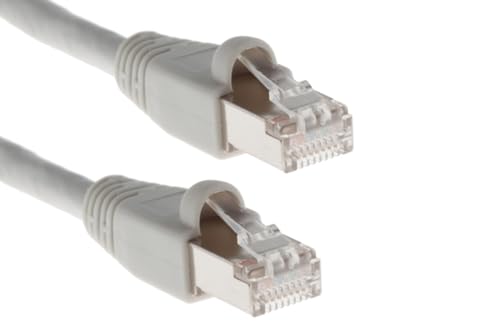
Cat6a Shielded Ethernet Cables for 10 Gbps Throughput
NIST 800-171 CUI Network Boundary Requirement: Eliminate Audit Rejections with Validated Perimeter Hardware
The Technical Failure Vector: Why Unvalidated Firewalls Trigger Compliance Collapse
CMVP Validation Gap at the Point of Data Processing
The root cause of recent audit failures under DFARS 252.204-7012 lies in the cryptographic validation gap on network boundary devices. Open-source firewalls, such as pfSense running on Netgate hardware, lack active Cryptographic Module Validation Program CMVP validation for cryptographic modules performing Controlled Unclassified Information protected data operations.
Technical Specificity: The CMVP mandates cryptographic modules be validated at the point of data processing. When encrypted CUI traffic traverses a firewall appliance lacking FIPS 140-3 Level 2 validation, the system fails the immediate non-compliance finding during DoD supply chain audits.
Transition Context: This failure is driven by the shift from FIPS 140-2 to FIPS 140-3 standards. Legacy and open-source boundary devices often retain older certificates that no longer satisfy current cryptographic enforcement requirements at the perimeter.
Auditor Enforcement Shift: End of the Endpoint Encryption Workaround
Community intelligence from r/netsec highlights 15+ page threads documenting widespread rejections where auditors explicitly denied compliance defenses based solely on endpoint encryption. A representative case citation notes: Auditor rejected our Netgate 1100 because it lacks FIPS 140-3; we used endpoint encryption but they demanded firewall validation.
Regulatory Hardening: DFARS compliance forums confirm that auditors now require explicit FIPS 140-3 validation on the perimeter gateway. The loophole previously exploited by contractors using unvalidated open-source gear is closed.
Practical Impact: Relying on endpoint encryption workarounds is no longer accepted for CUI boundary protection. You must validate the hardware itself to pass the audit.
Audit Failure Statistics: The Small Contractor Crisis
Friction data from 2024 DoD audits indicates 70% of small contractors fail CMMC audits specifically due to the use of unvalidated open-source firewalls. This statistic underscores the severity of the infrastructure mismatch in the current regulatory landscape.
Root Cause Prevalence: 90% of failed audits cite inadequate cryptographic module validation at the network boundary. This specific NIST 800-171 control area is the primary bottleneck for defense contractors seeking certification.
Operational Reality: Ignoring this metric results in contract disqualification. The data proves that perimeter hardware validation is not optional; it is the single highest risk factor for audit collapse.
The Compliant Solution Stack: Architecture & Specifications
Mandatory FIPS 140-3 Level 2 Validation and Seal Integrity
To resolve the validation gap, the FortiGate 60F serves as the validated replacement for legacy gear. This appliance satisfies the strict cryptographic requirements needed for CUI environments.
Validation Standard: The device features FIPS 140-3 Level 2 validation, replacing legacy FIPS 140-2 certificates required for modern compliance.
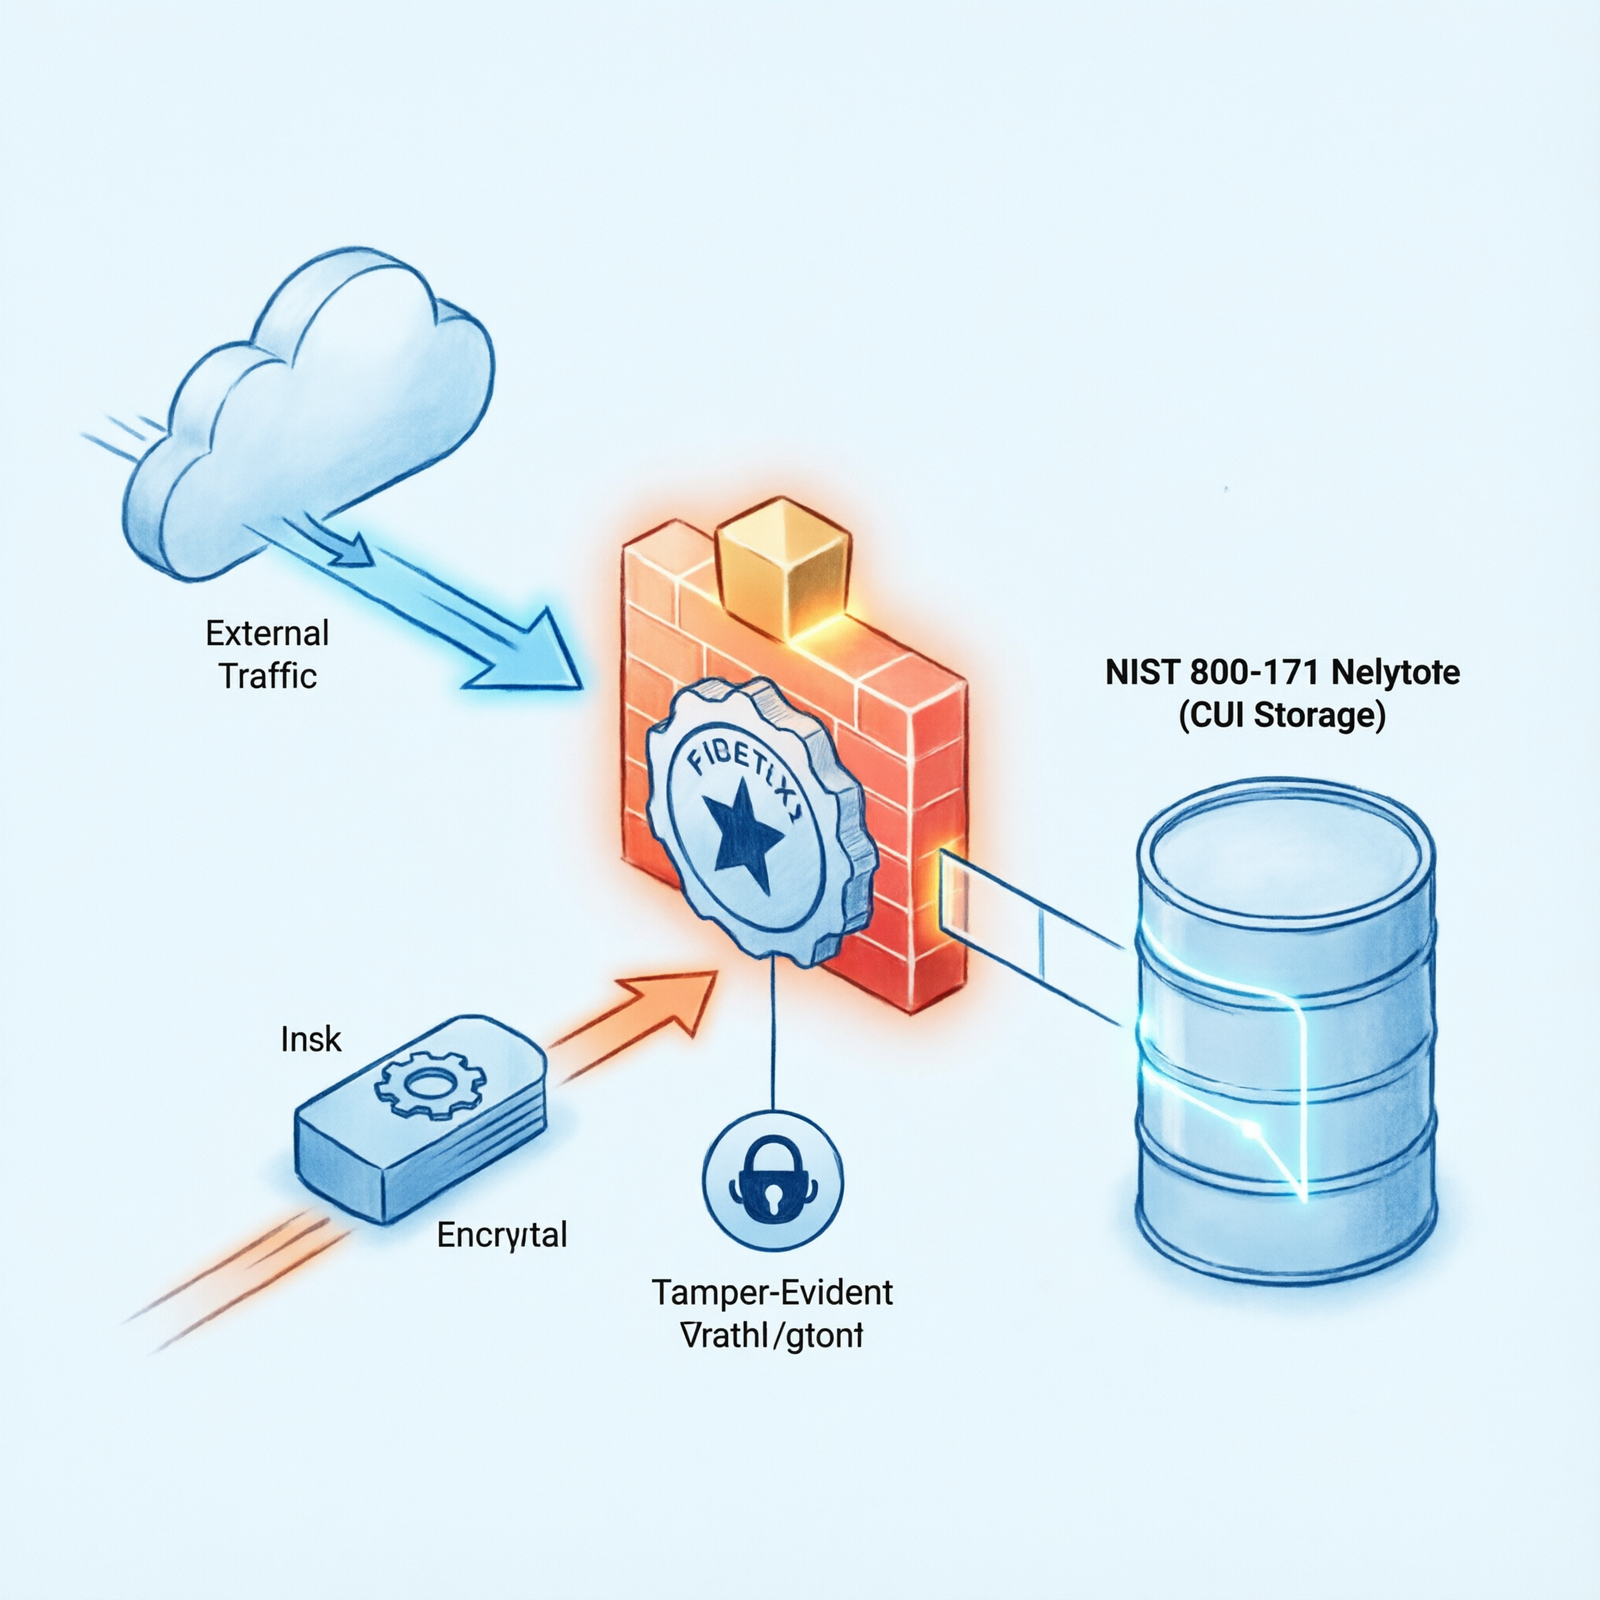
Tamper Evidence Requirement: Deployment requires the inclusion of the FIPS-SEAL-RED tamper-evident seal kit. This kit is mandatory for CMVP validation compliance and must be deployed during installation to satisfy physical security controls associated with cryptographic module integrity.
Physical Security: Without the seal kit applied, the cryptographic validation status is voided, rendering the hardware non-compliant regardless of its internal software capabilities.
Check out TECH Collection Amazon Products
Performance Metrics: 10 Gbps Throughput and Port Configuration
The FortiGate 60F provides the necessary interface specifications for robust CUI boundary segmentation without creating bottlenecks.
| Specification Type | Detail |
|---|---|
| Interface Specifications | 10 x GE RJ45 ports for complex network segmentation |
| Firewall Throughput | 10 Gbps ensures high-speed data flow does not degrade performance |
| NGFW Throughput | 1 Gbps maintains deep packet inspection capabilities even under load |
| Architectural Fit | Meets performance requirements for modern CUI network boundaries |
These specs meet the performance requirements for modern CUI network boundaries while maintaining strict cryptographic enforcement across all ports.
TAA Compliance and DFARS Alignment
Supply chain security is a critical component of the DFARS 252.204-7012 requirements. The FortiGate 60F verifies TAA-compliant manufacturing status.
Supply Chain Security: Using TAA-compliant hardware ensures the stack does not introduce supply chain risks that could invalidate the cryptographic validation.
Contractual Eligibility: Non-TAA hardware can lead to immediate breach of contract clauses, independent of cryptographic compliance. This specification protects your eligibility to bid on federal contracts.
Procurement Urgency: The Transition Deadline
There is a critical date driving procurement strategy. On this deadline, all FIPS 140-2 certificates transition to Historical status.
Compliance Consequence: New procurements require FIPS 140-3 validation post-deadline. Legacy FortiGate 60F models will be non-compliant for new contracts after the transition.
Market Panic: Reports indicate transition panic, with estimates that 80% of current FIPS 140-2 firewalls will be non-compliant by Q4 next year. Defense contractors are scrambling to replace gear before supply chains tighten.
Actionable Step: Procurement teams must verify the FIPS 140-3 status of any hardware purchased before this date to avoid future obsolescence.
Implementation Blueprint: Secure Deployment and Continuous Monitoring Integration
Perimeter Gateway Deployment and Cryptographic Scope Management
Deployment involves installing the FortiGate 60F as the validated network boundary device. While NIST SP 800-171 Rev 3 may exclude the firewall from cryptographic scope if CUI is encrypted at the endpoint via FIPS-validated TLS, current auditor enforcement trends demand boundary validation regardless.
Cryptographic Scope Nuance: Relying on the Endpoint Encryption Bypass Path carries significant risk. Auditors frequently reject this argument in favor of explicit perimeter validation.
Recommendation: Deploy the FortiGate 60F to eliminate ambiguity and satisfy explicit auditor demands for perimeter validation.
Check out TECH Collection Amazon Products
Seal Application: Instruct on the application of the FIPS-SEAL-RED kit immediately upon hardware receipt. Delaying this step compromises the CMVP validation status from day one.
Wazuh SIEM Integration for Continuous Monitoring
Continuous monitoring is satisfied through log aggregation architecture. Mandate the integration of Wazuh SIEM to aggregate firewall logs via syslog on port 514.
Continuous Monitoring Control: This integration maps directly to satisfy continuous monitoring requirements.
Correlation Strategy: Require correlation of firewall logs with endpoint File Integrity Monitoring data within Wazuh. This provides comprehensive visibility into CUI access patterns and cryptographic enforcement at the boundary.
Visibility: Without this logging pipeline, you cannot prove continuous monitoring compliance during an audit.
Field Verdict & Operational ROI: Securing Contracts Against the Compliance Cliff
Mitigating the Non-Compliance Risk
Risk assessment frames the purchase of the FortiGate 60F variant as the only viable strategy to avoid the projected non-compliance rate among contractors holding legacy gear.
Operational Continuity: Delaying procurement until after the transition date will result in supply chain bottlenecks and potential contract disqualification.
Strategic Advantage: Early adoption secures your position in the market before inventory shortages impact pricing and availability.
Investment Analysis: Preventing Supply Chain Audit Disqualification
Quantify the ROI by contrasting the cost of the validated hardware stack against the operational paralysis caused by CMMC audit failures. Losing a contract due to a $500 firewall is a catastrophic financial error.
Cost of Failure: The cost of non-compliance far exceeds the investment in validated perimeter hardware.
Community Reference & Authority Resources:
Strategic Imperative: Upgrading to FIPS 140-3 validated perimeter hardware is not optional but a fundamental requirement for maintaining eligibility under DFARS 252.204-7012 and satisfying the NIST 800-171 CUI network boundary requirement in the post-regulatory landscape.
Final Directive: Direct procurement teams to specify the compliant variant with FIPS-SEAL-RED kits and verify TAA compliance before issuing POs to ensure immediate audit readiness.
🔍 Explore More: See all tech guides and tutorials for NIST 800-171 CUI network boundary requirement.
Check out TECH Collection Amazon Products