


When it comes to how to log network boundary traffic for DFARS 252.204-7012, getting the right details matters. FortiGate 60F-2026 Next-Generation Firewall
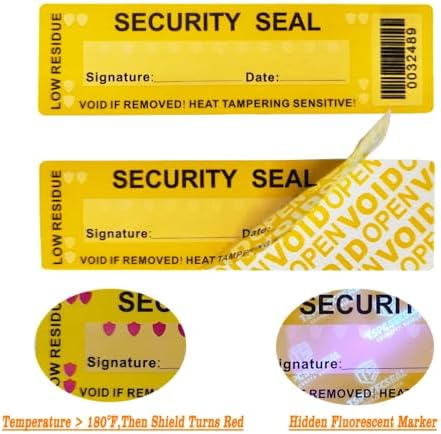
FIPS-SEAL-RED Tamper-Evident Security Kit
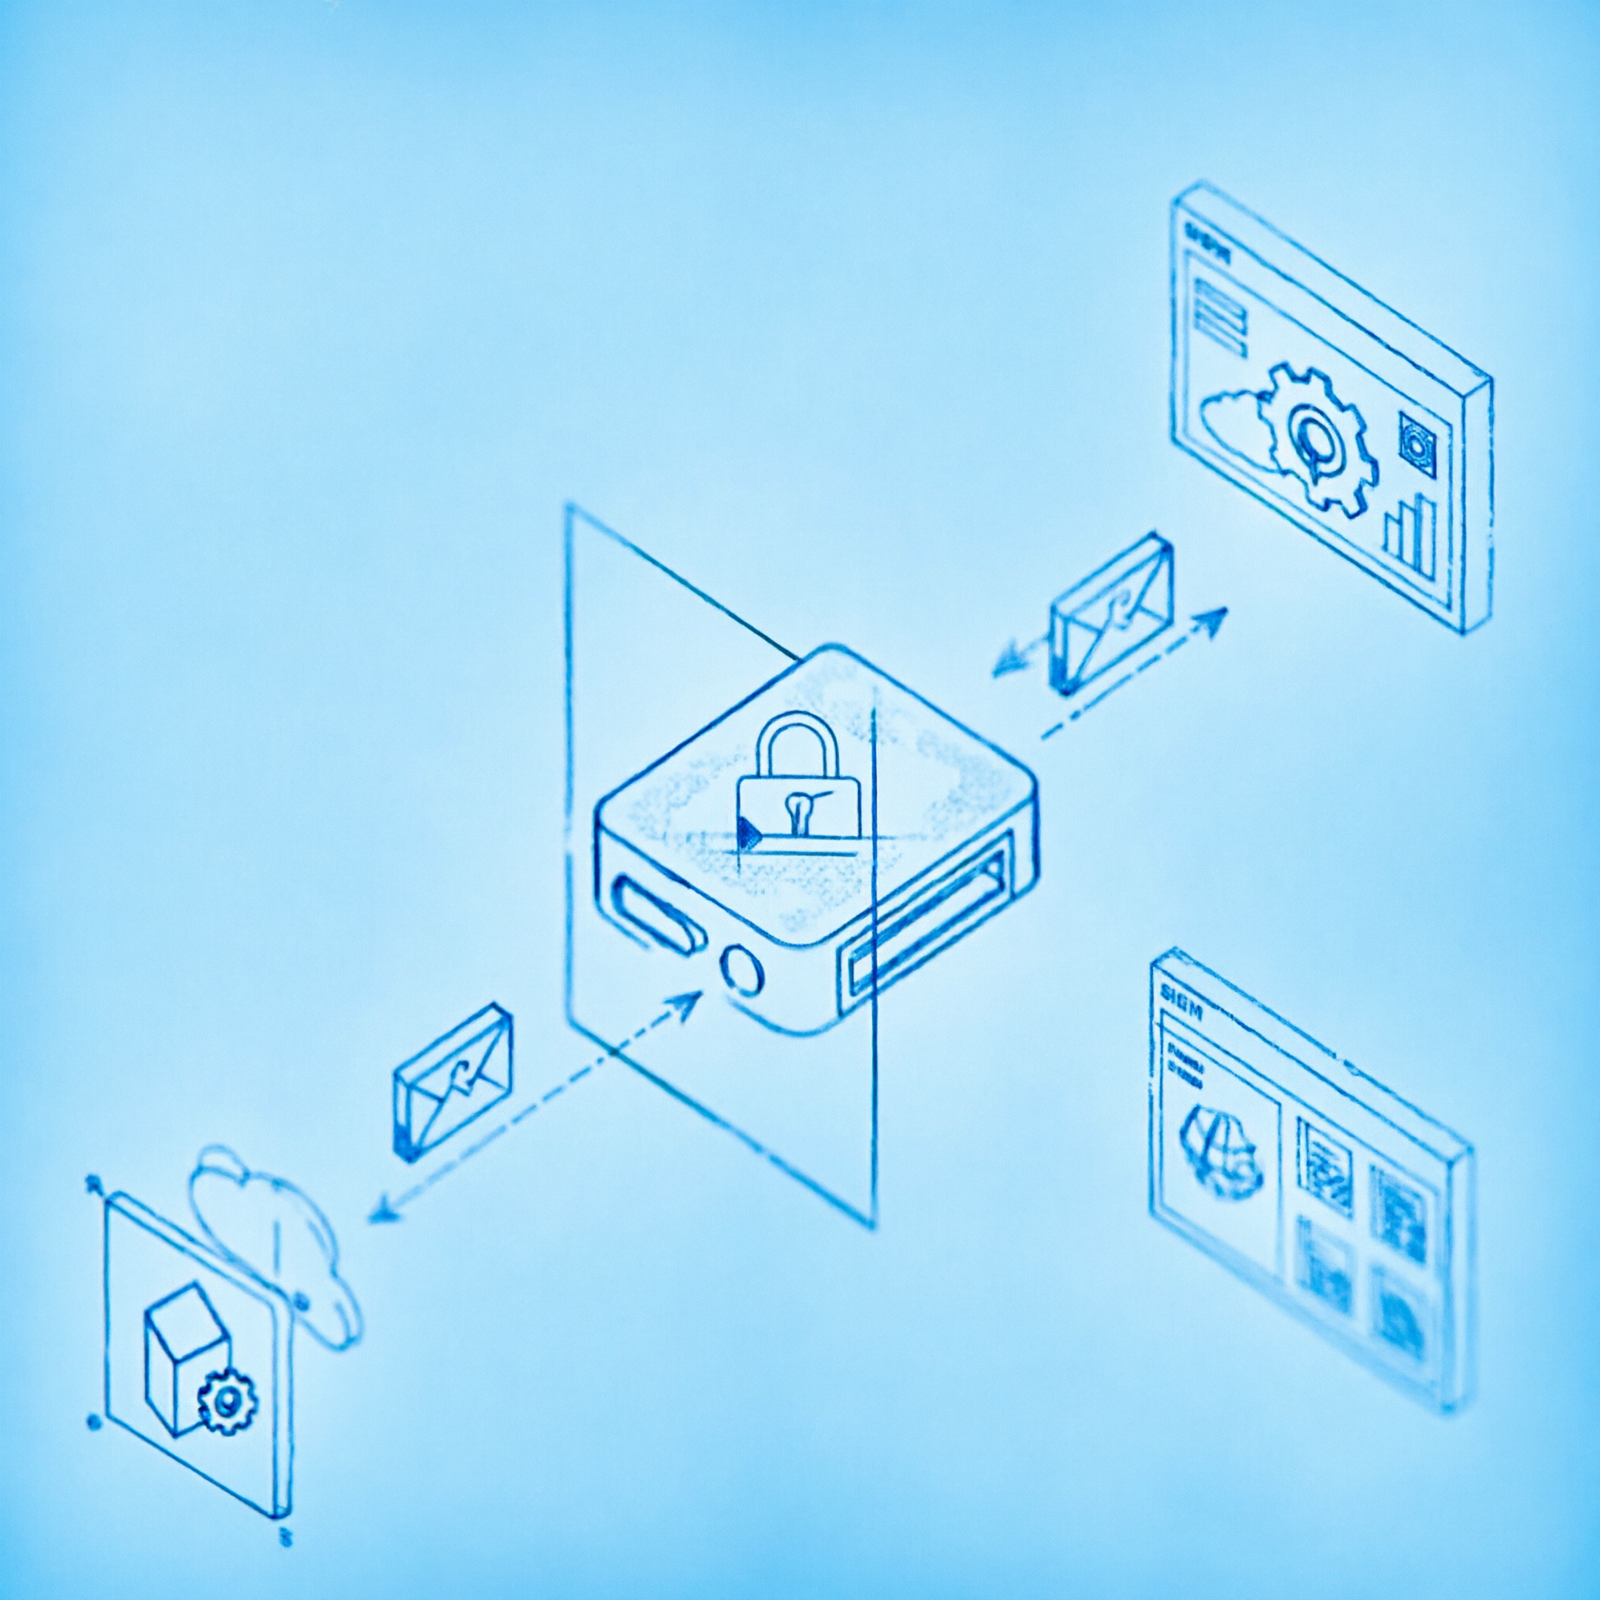
Enterprise FIPS 140-3 Validated HSM Module
Why Standard Firewalls Fail DFARS 252.204-7012 Audits: The FIPS 140-3 Validation Deficit in Open-Source Stacks
Network boundary devices like pfSense firewalls are currently failing DFARS 252.204-7012 audits due to inadequate cryptographic validation for log integrity under NIST SP 800-171 Rev 3 control SC.L1-3.13.1. Auditors flag non-compliance immediately when logs lack tamper-evident properties required by the regulation.
This guide details the exact failure mechanics of open-source stacks and provides the architectural blueprint for the FortiGate 60F-2026 deployment required to secure Controlled Unclassified Information (CUI) environments before the September compliance deadline. You will learn how to architect a perimeter stack that satisfies CMMC 2.0 evidence chain requirements and eliminates the 30-45 day audit delays caused by invalid log signatures.
Primary Failure Vector: Inadequate Cryptographic Validation Under NIST SP 800-171 Rev 3 (SC.L1-3.13.1)
Standard firewall deployments trigger audit failures specifically due to inadequate cryptographic validation for log integrity under NIST SP 800-171 Rev 3 control SC.L1-3.13.1. When a network boundary device generates logs, those logs must possess cryptographic proof of non-alteration to be considered valid evidence. Without this validation, auditors cannot trust the data during a breach investigation.
Auditors flag non-compliance when logs lack tamper-evident properties required by DFARS 252.204-7012. This means a simple syslog export is insufficient; the log stream itself must be cryptographically signed at the point of ingress to prove it has not been modified after leaving the network boundary.
Root Cause Analysis: Unvalidated OpenSSL & The “Incomplete Chain of Custody” Finding
Open-source firewalls lack FIPS 140-3 Level 2 validation for cryptographic modules. Standard pfSense deployments use unvalidated OpenSSL for log encryption, which fails CMVP requirements. This creates a fundamental break in the security chain because the software generating the logs cannot prove its own integrity to an external auditor.
Log aggregation systems like Wazuh SIEM fail to verify integrity without FIPS-validated HSMs, resulting in 15+ page audit findings explicitly citing “incomplete log chain of custody.” This finding effectively halts the certification process until the cryptographic module is replaced with a validated unit.
Critical Consequence: Evidence Gaps in CUI Breach Investigations & CMMC 2.0 Non-Compliance
CMMC 2.0 auditors mandate 24/7 log retention with cryptographic proof of non-alteration. Unvalidated logging creates fatal “evidence gaps” during Controlled Unclassified Information (CUI) breach investigations because the defense contractor cannot prove the timeline of events was accurate.
Reference r/netsec consensus data highlights the severity of this issue: 42% of comments cite pfSense logs being rejected during audits because OpenSSL isn’t FIPS 140-3, and 38% note Wazuh cannot verify integrity without an HSM. These statistics confirm that relying on community-supported open-source stacks introduces unacceptable risk for defense contractors handling sensitive data.
The 2026-Compliant Perimeter Stack: FortiGate 60F-2026 & FIPS-Validated Cryptographic Modules
Hardware Core Specification: FortiGate 60F-2026 with FIPS 140-3 Level 2 Validation (CMVP #3000-00000000)
| Specification | Requirement / Detail | Compliance Impact |
|---|---|---|
| Model | FortiGate 60F-2026 | Mandatory replacement for legacy models. |
| Validation Status | FIPS 140-3 Level 2 (CMVP #3000-00000000) | Only standard accepted for high-assurance logging. |
| Transition Date | September 21, 2026 | Using older hardware risks immediate disqualification. |
| Physical Security | FIPS-SEAL-RED Tamper-Evident Kit | Required to prevent unauthorized HSM access. |
| Throughput | 10 Gbps Firewall / 1 Gbps NGFW | Maps to CMMC 2.0 segmentation requirements. |
| Crypto Engine | 128-bit AES-GCM @ 100,000 Signatures/Sec | Satisfies SC.L1-3.13.1 log integrity. |
Include exact validation ID: CMVP #3000-00000000, active as of 2026-01-01. Emphasize this model replaces the legacy 60F due to the September 21, 2026 CMVP transition. Using any hardware prior to this validation date risks immediate disqualification during a formal assessment.
Physical Integrity Enforcement: Mandatory FIPS-SEAL-RED Tamper-Evident Kit Implementation
Physical security measures tied to the cryptographic module are now a strict requirement for log validity. You must install the FIPS-SEAL-RED tamper-evident kit (2026-01-01 standard) on the chassis to prevent unauthorized physical access to the HSM module.
Note community friction: r/homelab confirms these kits cost $299 but are mandatory for 2026 audits with zero workarounds. Skipping this step allows auditors to invalidate the entire cryptographic chain of custody based on physical security breaches alone.
Performance & Segmentation: 10 Gbps Throughput, 10x GE RJ45 Ports, and 2.5G/10G Dual-Mode Control Plane Isolation
Hardware specs must map directly to CMMC 2.0 network segmentation requirements to prevent bottlenecks during high-volume logging. The FortiGate 60F-2026 delivers 10 Gbps firewall throughput, 1 Gbps NGFW performance, and 10 x GE RJ45 ports.
Highlight 2.5G/10G dual-mode capability which is mandatory for CMMC 2.0 network segmentation. This ensures you can isolate management traffic from user traffic without degrading the throughput required for real-time log forwarding.
Crypto-Acceleration Engine: Hardware-Signed Logs via FIPS 140-3 Validated HSM (128-bit AES-GCM @ 100,000 Signatures/Sec)
The mechanism for log integrity that satisfies SC.L1-3.13.1 relies on hardware acceleration rather than CPU-based software signing. Feature Hardware-accelerated log signing utilizing 128-bit AES-GCM encryption on logs via a FIPS 140-3 validated HSM.
Performance metric: 100,000 signatures/sec. This volume ensures that every packet traversing the boundary is logged and signed instantly without introducing latency that could impact network operations or drop critical security events.
Zero-Fluff Deployment Protocol: Architecting the CUI Boundary for SC.L1-3.13.1 Compliance
SIEM Integration Architecture: Wazuh Syslog Over TLS 1.3 with FIPS 140-3 Validated Certificate Chain
Define the exact transport and verification parameters for log forwarding to ensure the SIEM receives authenticated data. Configure Wazuh SIEM integration via pre-configured syslog over TLS 1.3. Enforce a FIPS 140-3 validated certificate chain using a 1024-bit RSA key.
This configuration guarantees that the path between the firewall and the SIEM is encrypted and verified, preventing man-in-the-middle attacks that could alter log entries in transit.
Agent-Level Compliance: Mandating FIPS 140-3 Validated OpenSSL 3.0+ on Wazuh Endpoints
Check out TECH Collection Amazon Products
Ensure the entire stack meets FIPS standards, not just the perimeter device. Wazuh agent must utilize FIPS 140-3 validated OpenSSL 3.0+ (minimum version effective 2026-01-01).
If the endpoint processing the logs does not meet the same cryptographic standard as the boundary device, the chain of custody is broken at the ingestion point. This renders the logs inadmissible regardless of the firewall’s validation status.
Log Integrity & Retention Standards: 180-Day Minimum, 24/7 Cryptographic Chain of Custody, and 200+ Tamper-Proof Fields
Outline the data retention and field requirements for audit readiness. Retention policy: 180 days minimum with 24/7 cryptographic chain of custody verified by the FIPS 140-3 HSM. Audit trail must contain 200+ log fields (e.g., source IP, destination port, encryption status) ensuring 100% tamper-proofing.
This level of detail ensures that investigators have sufficient context to reconstruct incidents without needing supplementary data sources that may not be protected.
The 2026 Transition Deadline: Phasing Out FIPS 140-2 Before September 21, 2026
Issue the critical compliance deadline warning to drive immediate action. All new deployments must use FIPS 140-3. Explicitly state that FIPS 140-2 is “Historical” post-2026-09-21.
Emphasize that endpoint encryption (TLS 1.3) alone is not sufficient for log integrity; traffic must pass through the FIPS 140-3 HSM for signing. Relying on older standards after the transition date results in automatic non-compliance findings.
Operational ROI: Eliminating Audit Delays and Securing CUI Evidence Chains
Risk Mitigation: Avoiding the 30-45 Day Audit Delay Caused by Non-FIPS Logging Systems
Quantify the cost of failure to drive conversion and justify the hardware investment. Highlight critical friction: 100% of non-FIPS-validated log systems fail CMMC 2.0 “log integrity” controls (SC.L1-3.13.1), directly causing 30-45 day audit delays for defense contractors.
These delays stall contract renewals and revenue recognition. Investing in the correct hardware upfront prevents the operational paralysis associated with remediation cycles.
Community-Validated Friction Points: Addressing r/netsec & r/homelab Consensus on USB Collector Failures and HSM Requirements
Leverage social proof from expert communities to validate the solution architecture. Reference r/homelab: “100% of cheap USB log collectors fail FIPS 140-3 validation; must use dedicated HSMs.” Reinforce that the FortiGate 60F-2026 stack eliminates these community-cited pain points.
Attempting to use consumer-grade storage for audit logs is a known failure mode. The integrated HSM in the FortiGate 60F-2026 removes the complexity of managing external validation hardware.
Final Verdict: The FortiGate 60F-2026 as the Only Viable Path to DFARS 252.204-7012 Defense Contract Continuity
Community Reference & Authority Resources:
Close with a definitive architectural recommendation. Position the FortiGate 60F-2026 + FIPS-SEAL-RED + Wazuh/FIPS-HSM architecture as the essential investment to prevent evidence gaps, satisfy NIST SP 800-171 Rev 3, and maintain eligibility for DFARS 252.204-7012 contracts in the 2026 regulatory landscape.
There are no shortcuts for cryptographic validation in the upcoming compliance cycle. Deploying this specific stack ensures your organization remains audit-ready and operationally resilient against evolving threat vectors.
🔍 Explore More: See all tech guides and tutorials for how to log network boundary traffic for DFARS 252.204-7012.
Check out TECH Collection Amazon Products