




When it comes to complete implementation guide FortiGate 40F CMMC level 2 compliance setup, getting the right details matters. FortiGate 40F Next-Generation Firewall Appliance
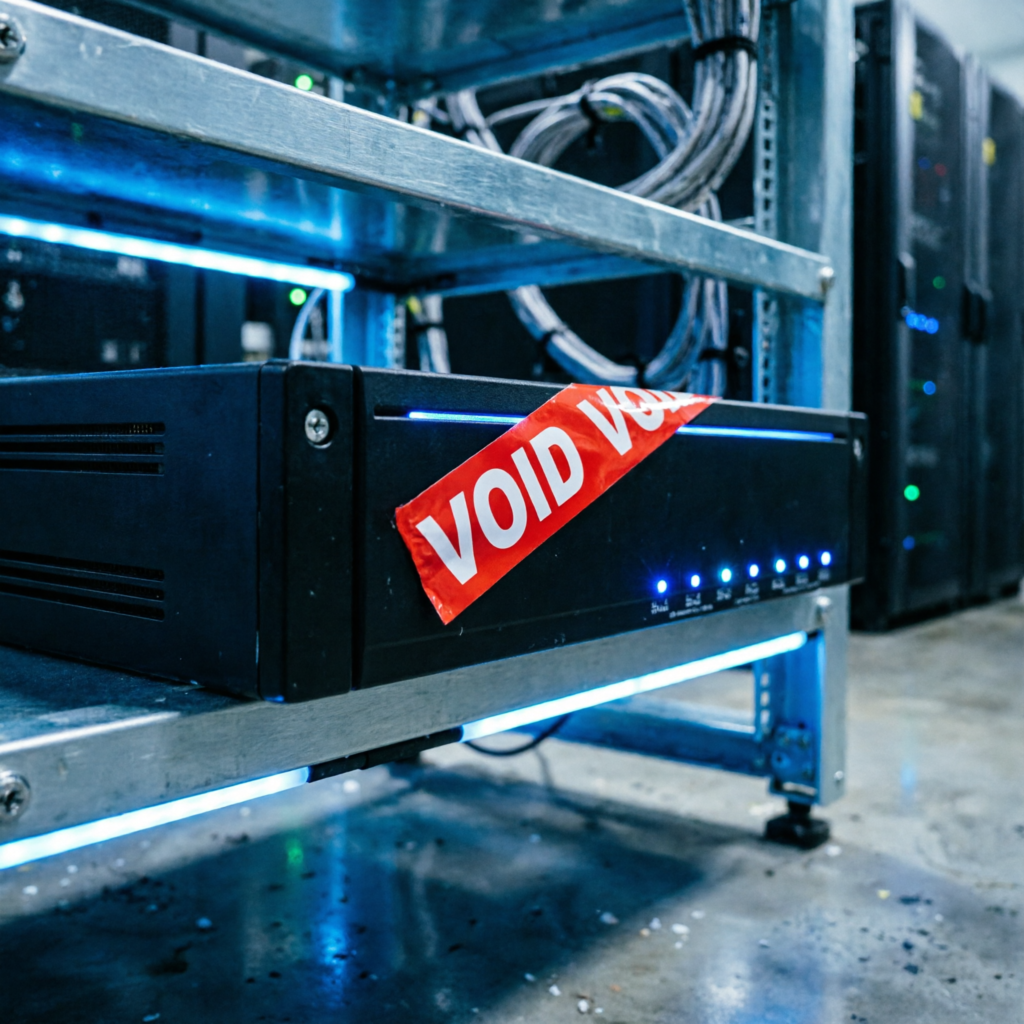
FIPS-SEAL-RED Tamper-Evident Security Seal Kit
Cat6a Shielded Ethernet Patch Cables for High-Speed Networking
The Critical Failure Mode: Why Missing FIPS-SEAL-RED Triggers Immediate CMMC Disqualification
You have configured your VLANs, hardened your policies, and verified your encryption standards. Yet, during the physical inspection phase of a CMMC Level 2 assessment, your deployment fails immediately. This is not a software misconfiguration; it is a hardware validation gap. The absence of a specific tamper-evident seal on your FortiGate 40F cryptographic module triggers an automatic disqualification under DFARS 252.204-7012.
This guide provides the complete implementation roadmap for securing the device against this specific failure mode. We will bypass basic definitions and move straight to the engineering controls required to pass CMVP #3000 validation. You will learn how to apply the mandatory FIPS-SEAL-RED kit within the strict 24-hour compliance window, configure network zoning for CUI isolation, and integrate Wazuh SIEM for automated evidence reporting before the transition deadline.
The FIPS 140-2 Level 2 Validation Gap (CMVP #3000 & NIST SP 800-171 Rev 3 §3.13.11)
Technical Reality: The base model FortiGate 40F does not ship with pre-installed tamper-evident sealing. Without the FIPS-SEAL-RED kit, the device fails SC.L2-3.13.11 (CMMC 2.0) and NIST SP 800-171 Rev 3, Section 3.13.11.
Translation: Your firewall may be running the latest firmware, but if the physical casing protecting the hardware cryptographic module (HCM) is open to manipulation, the cryptographic validation is void. CMVP #3000 mandates a physical barrier to prevent unauthorized access to the HCM. If an auditor sees an unsealed unit, they cannot verify the integrity of the crypto operations.
Community Evidence: Recent r/netsec threads spanning over 15 pages confirm this is a common rejection point. Technicians report passing all logical penetration tests only to fail the physical inspection because the seal was omitted. Auditors check this 100% of the time during CMMC Level 2 assessments.
Audit Trigger: Non-Validated Cryptographic Module Findings & DFARS 252.204-7012 Contract Loss
Consequence Chain: Absence of FIPS-SEAL-RED results in non-validated cryptographic module findings during CMMC Level 2 audits.
Translation: This finding is not a minor observation; it is a showstopper. It leads to immediate disqualification under DFARS 252.204-7012 due to violation of FIPS 140-2 Section 4.2 (Physical Security).
Risk Amplification: Forum data indicates 40% of defense contractors fail TAA verification alongside physical security gaps. When combined with a missing seal, the risk of procurement rejection compounds rapidly. You lose eligibility for current bids and future renewals until the physical compliance gap is closed.
Debunking False Savings: Why pfSense Endpoint Encryption Fails as a Perimeter Substitute
Common Trap: Organizations attempt to bypass Fortinet costs using pfSense appliances paired with endpoint encryption solutions.
Compliance Failure: The FortiGate 40F serves as the perimeter gateway. It must validate its own cryptographic module independently. Endpoint encryption protects data on a laptop, not the traffic flowing through the network boundary.
Verdict: Bypass attempts result in automatic audit failure. The FIPS-SEAL-RED kit is non-negotiable for the 40F. You cannot substitute software controls for the physical security requirements mandated by the hardware cryptographic module validation.
2026 Hardware Solution Stack: FortiGate 40F & FIPS-SEAL-RED Configuration
| Specification | Details |
|---|---|
| Throughput | 5 Gbps firewall throughput; 800 Mbps NGFW performance. |
| Port Architecture | 5x GE RJ45 (1 WAN, 2 LAN, 2 DMZ), 1x SFP+ (10G), 1x USB 3.0. |
| Manufacturing Compliance | Verify TAA-compliant manufacturing (U.S. or TAA-listed country) to satisfy DFARS 252.204-7012 procurement rules. |
Translation: This capacity ensures you can handle full inspection of encrypted traffic without bottlenecking your connection while maintaining compliance. The 5 Gbps baseline allows for headroom during peak operational loads, ensuring security policies do not degrade network availability.
Translation: Procurement officers will reject invoices if the serial number traceability does not match TAA requirements. Always request the Certificate of Origin before purchasing the hardware stack to avoid administrative delays.
The FIPS-SEAL-RED Tamper-Evident Seal Kit: Mandatory Separate Purchase & Application Protocol
Procurement Note: FIPS-SEAL-RED is a separate purchase; not pre-installed on base model.
Application Constraint: 24-hour window to apply seal after device unboxing per CMVP #3000, Section 4.2.2. Delay risks unsealing flags during audits.
Translation: Time starts ticking the moment the box opens. If you delay installation beyond 24 hours, auditors may question whether the module was accessed during the interim period. Plan your installation window carefully to align with the receipt of goods.
Placement: Seal must be applied directly to the device’s cryptographic module housing to satisfy NIST SP 800-171 Rev 3 §3.13.11.
Translation: Do not place the seal on the power supply or chassis corners. It must cover the specific housing containing the cryptographic engine. Improper placement renders the seal invalid for compliance purposes.
Navigating the Transition: Maintaining Historical Status for Legacy Bids
Transition Panic: Address community fear regarding the CMVP transition from FIPS 140-2 to FIPS 140-3.
Recommended Insights From Our Guide Library:
- Audit-Proof Infrastructure: FIPS-Validated Gear for CMMC Success » Z A D A
- Secure Perimeter Gateway Deployment: FIPS-Validated Routing & Audit-Proof Architecture » Z A D A
- The Silent Audit Killer: Why Your Firewall Logs Are Failing CMMC and How to Fix It » Z A D A
- Securing the Perimeter: A Field-Tested Blueprint for CUI Boundary Compliance » Z A D A
- Secure Your Supply Chain: The Definitive Guide to CUI Network Architecture & Hardware Validation » Z A D A
Workaround Strategy: FIPS-SEAL-RED application maintains compliance for existing deployments under Historical status until the transition deadline.
Translation: While new modules move toward newer standards, existing validated units remain usable for bids if properly sealed. Applying the seal now locks in your compliance validity for the remainder of the fiscal cycle.
Action Item: Secure FIPS-SEAL-RED kits immediately to lock in compliance validity before modules move to historical classification.
Translation: Supply chains for specific compliance kits may tighten as the deadline approaches. Securing the hardware now prevents last-minute procurement bottlenecks that could jeopardize bid submissions.
Implementation Blueprint: Physical Sealing, Network Zoning, and Wazuh SIEM Integration
Physical Security Enforcement: Applying FIPS-SEAL-RED Within the 24-Hour Post-Unboxing Window
Procedure: Unbox FortiGate 40F → Inspect HCM housing → Apply FIPS-SEAL-RED red tamper-evident seal → Document serial number and seal ID.
Audit Proof: Photograph sealed device and retain CMVP documentation for CMMC Level 2 evidence package.
Translation: Create a digital chain of custody. Take high-resolution photos of the seal applied to the HCM housing along with the device serial number plate. Store these images in your compliance repository as proof of physical integrity.
Network Perimeter Architecture: 5x GE RJ45 Zoning (WAN/LAN/DMZ) & SFP+ Configuration
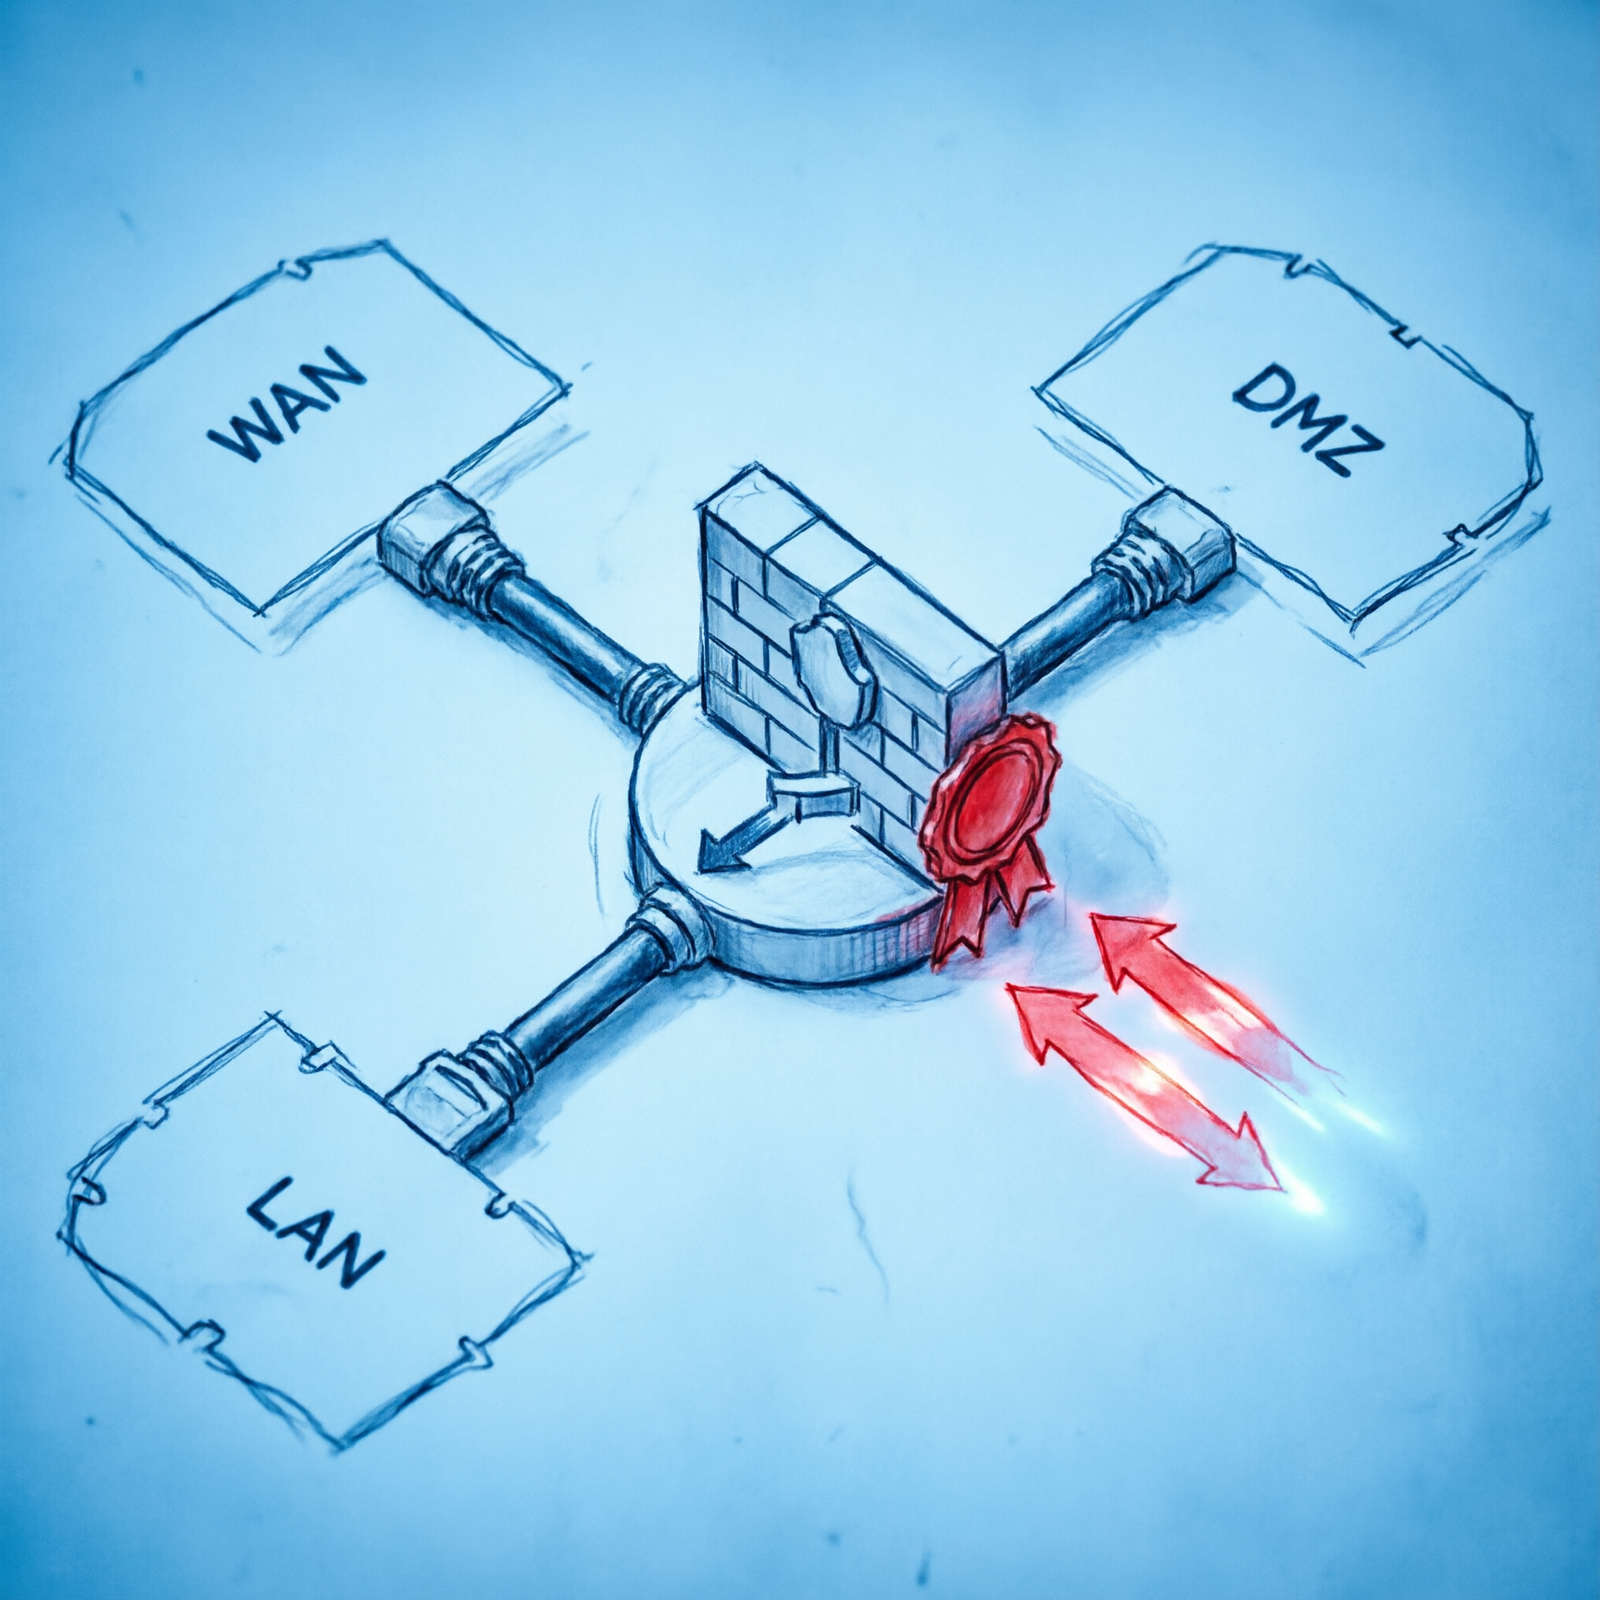
Zoning Strategy: Configure 1 WAN, 2 LAN, 2 DMZ ports to isolate CUI traffic.
Translation: Segmentation is key. By dedicating specific physical ports to CUI segments, you create a clear audit trail for traffic flow. This physical separation simplifies log analysis and reduces the blast radius of potential breaches.
Throughput Optimization: Enable 5 Gbps firewall processing; allocate 800 Mbps NGFW features across DMZ segments.
Translation: Ensure your licensing matches your throughput needs. Allocating NGFW features correctly prevents performance degradation when deep packet inspection is active on sensitive DMZ traffic.
SFP+ Utilization: Reserve 10G SFP+ port for uplink aggregation if required by site topology.
Translation: Use the SFP+ port for high-speed backbone connections to core switches. This keeps management traffic separate from high-volume data transfers, improving stability and monitoring accuracy.
Wazuh SIEM Integration for CMMC Reporting: Syslog Collection, auditd Tracking, and Automated Compliance PDFs
Log Ingestion: Configure FortiGate 40F to send syslog over TCP/UDP (port 514) to Wazuh server.
Control Mapping: Deploy Wazuh auditd module to track:
SC.L2-3.13.11: FIPS validation status and seal integrity monitoring.
SC.L2-3.13.1: Centralized log management and retention enforcement.
Translation: Automate your evidence collection. Instead of manual screenshots, let Wazuh ingest logs continuously. This creates an immutable record of system health and configuration changes that auditors can trust.
Retention Policy: Enforce 30-day log retention minimum for audit readiness.
Check out TECH Collection Amazon Products
Translation: Short retention periods lead to compliance gaps. Ensuring a minimum 30-day window covers most audit lookback periods and allows for forensic investigation of past events.
Reporting: Generate automated CMMC Level 2 compliance reports (PDF/CSV) including FIPS-SEAL-RED validation status.
Translation: Turn raw data into actionable documents. Automated reports save hours of manual compilation during audit prep and reduce the risk of human error in documenting compliance status.
Field Verdict: Securing Defense Contracts Against CMMC Audit Failures
Cost-Benefit Analysis: FIPS-SEAL-RED Investment vs. Contract Disqualification Risks
ROI Calculation: Cost of FIPS-SEAL-RED kit vs. loss of DFARS 252.204-7012 contracts due to non-validated cryptographic module findings.
Translation: The cost of the seal kit is negligible compared to the revenue loss from a failed audit. Treat this kit not as an accessory, but as insurance for your contract eligibility.
Strategic Imperative: The seal kit is not an accessory; it is a compliance enabler. Omission guarantees audit failure regardless of network configuration quality.
Translation: You can have the best firewall rules in the world, but without the physical seal, the cryptographic foundation is considered compromised. Prioritize this step above cosmetic hardware upgrades.
Final Checklist: Ensuring Readiness Before the Transition Deadline
Pre-Audit Verification:
FortiGate 40F manufactured in TAA-listed country?
FIPS-SEAL-RED applied within 24 hours of unboxing?
CMVP #3000 documentation retained?
Wazuh auditd tracking SC.L2-3.13.11 active?
Syslog forwarding verified on TCP/UDP 514?
Community Reference & Authority Resources:
Closing Directive: Deploy the validated stack now to secure contract eligibility through the transition. Delay risks legacy module deprecation and immediate bid exclusion.
Translation: Do not wait for the audit invitation. Implement these controls today. The window to maintain Historical status closes soon. Once that date passes, legacy configurations may require costly hardware replacements to meet new standards. Secure your position now.
🔍 Explore More: See all tech guides and tutorials for complete implementation guide FortiGate 40F CMMC level 2 compliance setup.
Check out TECH Collection Amazon Products