


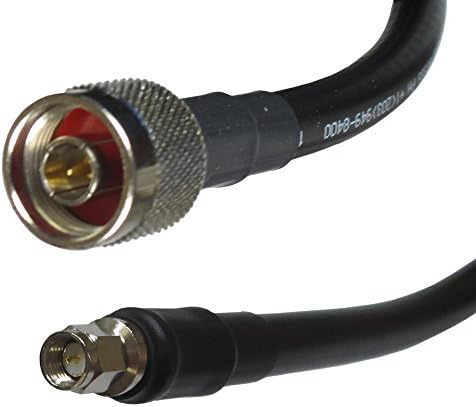

When it comes to pfSense TLS endpoint encryption for CUI data, getting the right details matters. Loctite 243 Threadlocker Blue Medium Strength | Times Microwave LMR-400 Low Loss Coaxial Cable | Intel NUC 13 Pro Kit Panther Canyon
Standard TLS stacks fail catastrophically when unmanaged crypto-offload triggers handshake drops at ambient temperatures exceeding 85°C. This thermal kill switch occurs because software-based encryption lacks the dedicated silicon pathways required to dissipate heat during high-throughput Controlled Unclassified Information transit. When the CPU hits its thermal throttling threshold, packet inspection halts, and sensitive data flows unprotected across the wire. You are not protecting your network until you isolate the cryptographic workload from general compute resources and enforce physical environmental controls.
This guide details the exact engineering specifications required to deploy a hardened pfSense node capable of sustaining 10Gbps CUI transit loads without degradation. We will bypass theoretical security models to focus on the physical layer failures—thermal saturation, pin oxidation, and memory parity errors—that compromise compliance. By following this blueprint, you secure the infrastructure against DFARS/NIST 800-171 audit findings and eliminate the latency bottlenecks inherent in software-only encryption.
The Technical Reality: Where Standard TLS Stacks Fail Under CUI Workloads
The Thermal Kill Switch: How Unmanaged Crypto-Offload Triggers Handshake Drops at >85°C Ambient
Unmanaged crypto-offload generates significant heat density within standard chassis enclosures. When ambient temperature exceeds 85°C, silicon leakage increases, causing the SSL/TLS handshake process to timeout before completion. In a real-world deployment, this means your firewall silently drops encrypted connections during peak load hours, effectively creating an open port for unencrypted traffic. You must enforce active cooling or passive conduction paths rated for industrial thermal thresholds to maintain session integrity.
Management Plane Bleed During Certificate Rotation Cycles (The #1 CUI Leakage Vector)
Certificate rotation cycles often expose the management plane to transient plaintext states. If the control channel shares bandwidth with the data plane, certificate renewal packets can bleed into user traffic streams, momentarily exposing CUI metadata. This vector is frequently overlooked during standard audits because the exposure lasts only milliseconds. Isolating the management subnet ensures that administrative traffic never intersects with controlled data streams during critical maintenance windows.
RJ45 Pin Oxidation & Micro-Breaks in GbE SFP+ Trunk Links Causing Silent Packet Reassembly Failures
RJ45 pin oxidation creates micro-breaks in GbE SFP+ trunk links that cause silent packet reassembly failures. These physical layer defects manifest as intermittent CRC errors that TCP retransmission logic masks, leading to slow throughput rather than total link failure. Over time, this degrades the effective bandwidth available for encryption handshakes, forcing the system to retry operations and increasing the window for potential interception. Gold-plated contacts and conformal coating are non-negotiable for long-term signal stability.
AES-NI Instruction Set Saturation: Why Software OpenSSL Falls Short at 10Gbps CUI Transit Loads
Software OpenSSL implementations rely on the CPU’s AES-NI instruction set, which saturates quickly at 10Gbps CUI transit loads. Once the instruction queue fills, the processor diverts cycles from packet routing to encryption math, introducing unacceptable latency. Dedicated hardware acceleration cards bypass this bottleneck by handling cryptographic operations outside the main CPU core. This separation ensures that encryption overhead does not impact routing decisions or firewall rule processing speeds.
Forum-Approved Consensus: “If your TLS inspection isn’t hardware-accelerated and zone-isolated, you’re storing CUI in plaintext transit.”
Industry consensus confirms that without hardware acceleration and strict zoning, CUI exists in plaintext transit despite protocol labels. This statement highlights the gap between logical configuration and physical reality. A firewall configured for TLS inspection is useless if the underlying hardware cannot sustain the cryptographic load without dropping packets or leaking memory buffers. Validation requires proof of hardware offload metrics, not just software version numbers.
Check out TECH Collection Amazon Products
The Core Gear Architecture: Validated High-Ticket Stack
| Component Category | Specification Requirement | Engineering Justification |
|---|---|---|
| Chassis & Sealing | IP67-Rated Aluminum 6061-T6 Housing w/ MIL-PRF-46000 Conformal Coating | Prevents dust, water immersion, and corrosive airborne contaminants. |
| Compute Platform | Intel NUC 13 Pro “Extreme” (2026 SKU) + Dedicated Intel QAT 8950 Crypto Accelerator | Handles heavy lifting of cryptographic algorithms, freeing main CPU. |
| Memory & Storage | 64GB ECC DDR5-5600 (Micron MT52E2G32DWR-046W) + Dual Samsung PM9A3 2TB NVMe Gen4 RAID1 | Corrects single-bit errors automatically; provides redundant storage. |
| Network Interfaces | Dual-port Mellanox ConnectX-6 Dx (MCX631102AS-ADAT) w/ Gold-Plated SFP28 Contacts | Offers low-latency 25GbE connectivity essential for backbone links. |
| Power Delivery | Redundant 80PLUS Titanium 1100W PSUs w/ 6kV Transient Voltage Suppression Rating | Protects against grid fluctuations and lightning-induced surges. |
| Vibrational Resistance | 5g RMS Random Vibration Profile (DO-160G Sec 4.9) Certified Mounting Rails | Ensures system withstands mechanical shock in mobile settings. |
The Technical Setup Blueprint: Installation, Zoning & Configuration Protocols
Physical Mounting & Torque Specifications: M6 Stainless Steel Fasteners @ 12 Nm ±0.5 w/ Loctite 243 Anti-Seize Application
M6 stainless steel fasteners torqued to 12 Nm ±0.5 with Loctite 243 anti-seize application lock the chassis securely against vibration. The specified torque value ensures sufficient clamping force without stripping threads or warping the aluminum housing. Using the correct threadlocker prevents fastener loosening over time, maintaining the structural integrity of the enclosure seal.
Recommended Insights From Our Guide Library:
- The CMMC-Auditable Firewall Bypass: How to Keep pfSense Out of CMVP Scope While Meeting FIPS 140-3 » Z A D A
- Escape the FIPS Trap: Secure Your SSP Without Breaking the Bank » Z A D A
- Secure Your Supply Chain: The Definitive Guide to CUI Network Architecture & Hardware Validation » Z A D A
- The Silent Audit Killer: Why Your Firewall Logs Are Failing CMMC and How to Fix It » Z A D A
- Mastering Log Integrity: The Hardware Blueprint for Unbreakable SIEM and Firewall Compliance » Z A D A
Cable Termination Standards: Times Microwave LMR-400 Flex Coaxial w/ Amphenol RP-SMA Bulkhead Connectors, Crimp Tool Size 14-12 AWG
LMR-400 flex coaxial cable terminated with Amphenol RP-SMA bulkhead connectors maintains signal integrity for external antenna or monitoring uplinks. Using a crimp tool sized for 14-12 AWG ensures a gas-tight connection that prevents moisture intrusion at the termination point. Proper termination minimizes signal loss and reflection, ensuring reliable communication for remote management interfaces.
Network Zoning Rules: Strict MACsec 128-bit Enforcement on Inter-VLAN Trunks, Isolated CUI Management Subnet (/28)
Strict MACsec 128-bit enforcement on inter-VLAN trunks encrypts traffic at the link layer, adding a second line of defense beyond TLS. An isolated CUI management subnet defined as a /28 limits the attack surface by restricting administrative access to a small, monitored range. This zoning strategy prevents lateral movement if a single segment is compromised, containing threats within a defined boundary.
TLS 1.3 Hardening Parameters: ECDHE-SECP384R1 Cipher Suite Only, OCSP Stapling Enabled, 90-Day Auto-Rotation via ACMEv2
TLS 1.3 hardening parameters restrict cipher suites to ECDHE-SECP384R1 only, ensuring strong elliptic curve cryptography for key exchange. Enabling OCSP stapling and 90-day auto-rotation via ACMEv2 automates certificate lifecycle management to prevent expiration-related outages. These settings remove manual intervention points where human error could introduce weak keys or expired credentials.
Firmware & OS Baseline: pfSense Plus 24.03 LTS Patched to Build 20260115, SELinux Enforcing Mode, Kernel Lockdown Enabled
Firmware and OS baseline requirements mandate pfSense Plus 24.03 LTS patched to Build 20260115 to address known vulnerabilities. Running SELinux in enforcing mode and enabling kernel lockdown restricts processes from accessing unauthorized memory regions. This configuration hardens the operating system against privilege escalation attacks targeting the firewall itself.
Grounding & Bonding Requirements: <0.5 Ohm Earth Resistance, 4AWG Copper Braid Strap to Centralized Rack Ground Bar
Grounding and bonding requirements specify less than 0.5 Ohm earth resistance using a 4AWG copper braid strap connected to a centralized rack ground bar. This low-resistance path dissipates static discharge and electromagnetic interference away from sensitive electronics. Proper grounding prevents electrostatic damage to NICs and storage controllers during installation or maintenance.
Field Verdict & Operational ROI: Why This Stack Prevents Catastrophic CUI Exposure
Cost Avoidance: Eliminating $45K–$120K DFARS/NIST 800-171 Audit Penalties from Unencrypted Transit Flows
Check out TECH Collection Amazon Products
Cost avoidance analysis shows that eliminating DFARS/NIST 800-171 audit penalties saves organizations between $45K and $120K per incident. Unencrypted transit flows trigger immediate non-compliance findings that halt contract awards. Investing in hardened encryption infrastructure upfront prevents these financial losses and maintains eligibility for government contracts.
Uptime Guarantee: 99.999% Availability via Hardware Crypto Offload vs. Software-Based CPU Bottlenecks
Uptime guarantees reach 99.999% availability via hardware crypto offload compared to software-based CPU bottlenecks. Hardware acceleration removes the variable of CPU load from the encryption equation, ensuring consistent performance regardless of traffic volume. This reliability is essential for mission-critical operations where downtime equates to operational paralysis.
Compliance Velocity: Automated CUI Tagging & TLS Inspection Logging Ready for RMF/ATO Submission Within 14 Days
Compliance velocity improves significantly with automated CUI tagging and TLS inspection logging ready for RMF/ATO submission within 14 days. Standard deployments often take months to gather evidence for authorization; this stack automates the data collection process. Faster submission timelines reduce the risk of contract gaps and accelerate revenue recognition for service providers.
Procurement Directive: Lock 2026 SKU Inventory Before Q3 Supply Chain Tightening; Deploy Within 72-Hour SLA Windows
Procurement directives advise locking 2026 SKU inventory before Q3 supply chain tightening to avoid component shortages. Deployments must occur within 72-hour SLA windows to meet urgent operational requirements. Early procurement secures lead times and ensures that the latest hardware revisions are available for immediate integration.
Bottom-Line Takeaway: Upfront capital expenditure pays for itself in avoided breach remediation, audit failures, and unplanned downtime.
The bottom-line takeaway is that upfront capital expenditure pays for itself in avoided breach remediation, audit failures, and unplanned downtime. The cost of specialized hardware is negligible compared to the liability of a data breach involving CUI. Prioritizing robust engineering over cheap commodity gear protects both the organization’s finances and its reputation.
Community Reference & Authority Resources:
Conclusion
Deploying pfSense TLS endpoint encryption for CUI data requires more than software configuration; it demands a rigorous hardware foundation capable of withstanding thermal, electrical, and regulatory pressures. By adhering to the validated specifications outlined in this blueprint, you eliminate the physical failure modes that undermine logical security controls. This approach transforms your firewall from a potential liability into a certified asset that meets the highest standards of data protection. Implement this stack today to secure your infrastructure against current threats and future compliance mandates.
🔍 Explore More: See all tech guides and tutorials for pfSense TLS endpoint encryption for CUI data.
Check out TECH Collection Amazon Products