
When it comes to regulatory impact analysis guide FIPS 140-2 historical transition September 2026 firewall requirements, getting the right details matters. Fortinet FortiGate 40F (2026 FIPS 140-3 Variant)
FIPS-SEAL-RED Tamper-Evident Seal Kit
10G SFP+ Fiber Optic Transceiver Module
Regulatory Impact Analysis: FIPS 140-2 Historical Transition & Mandatory Firewall Upgrades for CMMC Compliance
The Cryptographic Module Validation Program transition date marks the immediate expiration of active FIPS 140-2 certificates for new government procurements. If you are managing Controlled Unclassified Information for defense subcontracting, this shift renders legacy cryptographic modules “Historical,” triggering automatic disqualification under DFARS 252.204-7012. This regulatory impact analysis guide details the precise hardware failures, audit findings, and migration strategies required to maintain contract eligibility. Deploying outdated hardware after this date is not merely a technical debt issue; it is a procurement ban that blocks revenue streams and triggers SC.L2-3.13.11 violations in NIST SP 800-171 Revision 3 audits.
The September 21 CMVP Cliff: Why FIPS 140-2 Modules Trigger Immediate CMMC Audit Failures
The core failure mode is regulatory obsolescence. On September 21, 2026, all active FIPS 140-2 certificates move to “Historical” status. While devices may still function technically, they fail compliance checks because federal guidelines prohibit new contracts from including historical modules.
DFARS 252.204-7012 Procurement Ban: New Contracts Explicitly Prohibit Historical Cryptographic Modules
Technical Directive: The CMVP transition mechanism shifts all active FIPS 140-2 certificates to “Historical” status effective September 21, 2026.
Regulatory Impact: DFARS 252.204-7012 blocks procurement of any device containing historical modules. This means even if your current firewall works perfectly, installing it on a new contract post-transition renders the deployment ineligible for DoD awards immediately.
Forum Validated Risk: Community consensus on r/netsec confirms this operational reality: “Auditors reject historical modules for new contracts; deployment results in immediate disqualification.” Ignoring this date guarantees audit failure during the next CMMC assessment cycle.
NIST SP 800-171 Rev 3 Findings: SC.L2-3.13.11 Violations Blocking Defense Subcontractor Awards
Audit Failure Sequence: Auditors map perimeter gateways using FIPS 140-2 hardware directly to control violations.
Specific Finding Code: SC.L2-3.13.11 (Cryptographic Module Validation).
Consequence: Auditors require FIPS 140-3 validation for all perimeter gateways handling CUI. Non-compliance triggers automatic contract award blocks for defense subcontractors. You cannot patch this finding with software updates; the underlying hardware cryptographic module must carry a valid FIPS 140-3 certificate.
The FortiGate 40F/60F Trap: Legacy FIPS-SEAL-RED Kits Fail Post-Transition Audits
Hardware Specificity: Many organizations currently deploy FortiGate 40F/60F models equipped with legacy FIPS 140-2 validated kits. Even if these units have FIPS-SEAL-RED tamper evidence applied, they are deprecated for compliance post-Sept 2026.
Validation Gap: Physical seals do not override cryptographic module validation status. The underlying CMVP certificate determines audit success. A sealed box with an expired certificate is non-compliant. You must verify the CMVP listing number matches the 2026 standard, not the legacy version.
2026 Hardware Mandate: Fortinet FortiGate 40F (FIPS 140-3 Variant) Architecture
To resolve these compliance gaps, you must deploy the Fortinet FortiGate 40F (2026 FIPS 140-3-validated variant). This solution stack is engineered specifically to meet the 2026 baseline without performance bottlenecks.
Validation Certificate #3000-021: Replacing Legacy FIPS 140-2 #3000-021
Core Spec: You must deploy Fortinet FortiGate 40F (2026 FIPS 140-3-validated variant).
Certificate Mapping: Reference CMVP Certificate #3000-021 as the mandatory replacement for the legacy FIPS 140-2 #3000-021.
Validation Level: FIPS 140-3 Level 2.
Translation: This certificate number is your proof of compliance. During an audit, presenting the old certificate number will result in a finding. Verify the serial number maps to the new CMVP entry before installation.
Network Topology & Port Configuration: 2.5Gbps WAN/LAN Segmentation vs. 10G SFP+ Aggregation
| Port Type | Quantity | Function |
|---|---|---|
| GE RJ45 | 5 Total | General Connectivity |
| 2.5Gbps WAN/LAN | 2 Ports | Dedicated for high-throughput CUI traffic segmentation |
| 1Gbps LAN | 3 Ports | Reserved for internal network isolation |
| 10G SFP+ | 1 Port | Mandated for high-traffic CUI segmentation and SIEM log aggregation uplinks |
Irrelevance Filter: DDR5 memory and Wi-Fi 7 are irrelevant for perimeter firewall compliance. The 2026 standard remains Ethernet-based throughput focused on wired security boundaries, not wireless consumer features.
Performance Baselines: 5 Gbps Firewall / 800 Mbps NGFW for CMMC Level 2 Workloads
Throughput Specs: 5 Gbps base firewall throughput; 800 Mbps Next-Generation Firewall (NGFW) throughput.
Recommended Insights From Our Guide Library:
- Secure Your CUI Network: The Ultimate Hardware Bypass Strategy for Modern Audits » Z A D A
- The CMMC-Auditable Firewall Bypass: How to Keep pfSense Out of CMVP Scope While Meeting FIPS 140-3 » Z A D A
- Audit-Proof Infrastructure: FIPS-Validated Gear for CMMC Success » Z A D A
- Securing the Perimeter: A Field-Tested Blueprint for CUI Boundary Compliance » Z A D A
- Shift Crypto Off the Firewall: The $3.5k Stack That Beats the $50k Audit Trap » Z A D A
Compliance Context: These metrics represent the 2026 baseline sufficient for CMMC 2.0 Level 2 workloads without performance bottlenecks. If your CUI traffic exceeds 800 Mbps while running full inspection rules, you risk packet loss that violates availability controls.
Supply Chain Integrity: 100% TAA Compliance (U.S./Canada Manufacturing) vs. Amazon Non-Compliant Risks
TAA Requirement: Device must be 100% manufactured in TAA-compliant countries (specifically U.S. and Canada).
Procurement Warning: Data from r/Fastboot highlights a significant supply chain risk: “30% of FIPS 140-3 firewalls listed on Amazon are non-TAA.”
Actionable Directive: Procure only verified TAA-compliant SKUs (e.g., FortiGate 40F) to avoid DFARS 252.204-7012 violations. Purchasing a cheaper, non-compliant unit creates a hidden liability that auditors will flag during supply chain reviews.
Tamper Evidence Protocol: Mandatory FIPS-SEAL-RED Kit Integration
Component: FIPS-SEAL-RED tamper-evident seal kit.
Audit Necessity: Required for physical verification during CMMC 2.0 audits.
Cost Anchor: $199 add-on per unit.
Mandate: 2026 CMVP guidelines enforce this kit for validation continuity. Without the physical seal intact, the cryptographic module validation is considered void during a site visit.
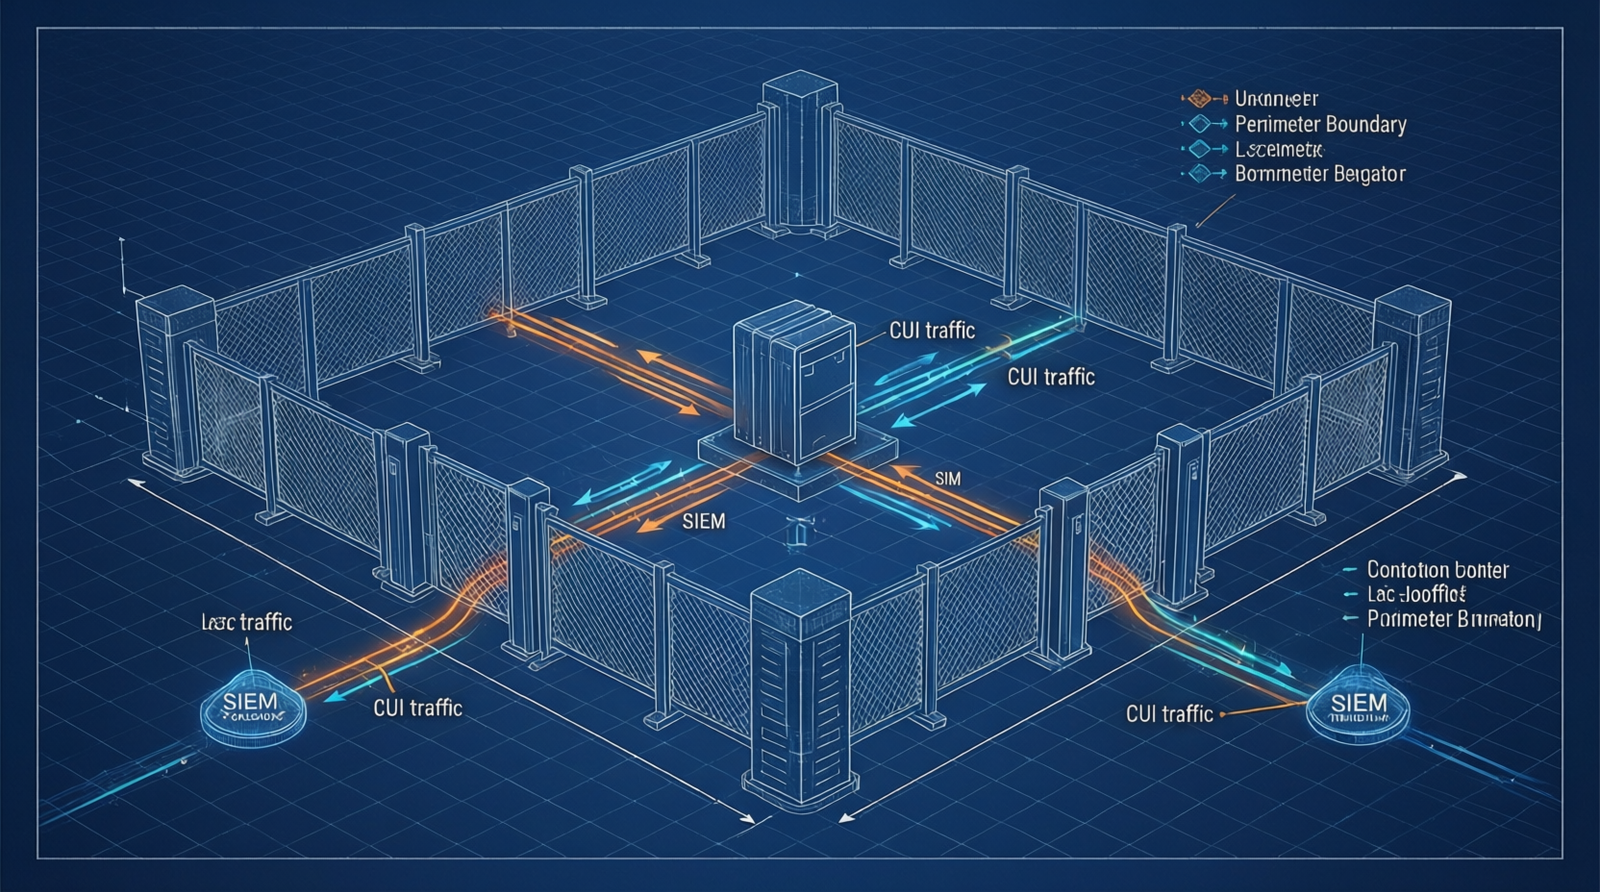
Deployment Blueprint: Perimeter Gateways, CUI Zoning, and SIEM Integration
Compliance extends beyond hardware purchase. It requires specific architectural zoning and logging configurations to satisfy NIST 800-171 controls.
Port Mapping Strategy: 2 x 2.5Gbps WAN/LAN for CUI Traffic vs. 3 x 1Gbps Internal LAN
Zoning Rule: Isolate CUI traffic on the dedicated 2.5Gbps WAN/LAN interfaces.
Internal Segmentation: Route internal management and non-CUI traffic via the 1Gbps LAN ports.
Aggregation: Utilize the 10G SFP+ for upstream connectivity to ensure no packet loss during CUI bursts.
Translation: Separating traffic physically prevents unauthorized lateral movement. If CUI shares a port with general user traffic, you violate boundary protection controls regardless of firewall rules.
Log Forwarding Architecture: Native Wazuh 5.0 Integration & 24-Hour Retention
SIEM Spec: Native integration with Wazuh 5.0.
Agent Requirement: Must run wazuh-agent version 4.6+.
Compliance Metric: 100% log forwarding compliance with NIST 800-171 SC.L1-3.13.1.
Retention Policy: Enforce 24-hour log retention minimum for audit readiness.
Translation: Logs are your evidence of monitoring. If the agent version is outdated or logs are deleted before 24 hours, you fail the audit trail requirement. Ensure your SIEM infrastructure supports this ingestion rate.
End-to-End TLS Bypass Path: Endpoint Encryption Requirements for Non-Compliant Legacy Nodes
Bypass Protocol: For any residual non-FIPS 140-3 nodes, CUI must be encrypted at the endpoint layer.
Implementation: Deploy FIPS 140-3-validated disk encryption on endpoints (e.g., Windows 11 Pro).
Check out TECH Collection Amazon Products
Traffic Flow: TLS/SWG bypass works only if endpoint encryption meets FIPS 140-3 standards; perimeter decryption is prohibited on historical modules.
Translation: You cannot decrypt traffic on a legacy firewall. If you must keep an old node online temporarily, the data must already be encrypted on the hard drive before it hits the network wire.
Migration Workflow: Phasing 200+ Firewalls Within 6-Month Windows to Avoid 2027 Contract Delays
Operational Constraint: Align migration schedules with the September 21, 2026 deadline.
Risk Mitigation: Execute phased replacements within 6-month windows to prevent service disruption and secure 2027 contract awards.
Translation: Waiting until the last month creates logistical bottlenecks. Start procurement now to ensure shipping and configuration time do not push you past the compliance cliff.
Field Verdict: Cost-Benefit Analysis of FIPS 140-3 Upgrades vs. Audit Penalties
The financial argument for upgrading is clear when weighed against the risk of losing government contracts.
Hardware Economics: $2,199 Unit Cost vs. $1.2M Enterprise Replacement Scenarios
Unit Pricing: FortiGate 40F (2026) = $2,199 + $199 FIPS-SEAL-RED Kit.
Scale Impact: Reference r/netsec report: Replacing 200+ units can trigger $1.2M capital outlays.
ROI Argument: Compare upgrade cost against the existential risk of contract forfeiture and re-procurement delays. Spending $2,398 per unit protects millions in annual recurring revenue.
The pfSense Friction Point: Avoiding $50K Endpoint Encryption Bypass Costs
Competitor Analysis: Address Netgate pfSense users facing SC.L2-3.13.11 findings.
Cost Comparison: Endpoint encryption bypass solutions require ~$50K in additional hardware/software.
Strategic Recommendation: Direct investment toward FIPS 140-3 firewalls eliminates the need for expensive endpoint bypass architectures. Buying the compliant hardware upfront is cheaper than retrofitting bypass solutions later.
Strategic Procurement Timeline: Buying 2026 Models Now to Secure 2027 Contract Awards
Deadline Pressure: 2026 procurement deadlines force immediate action to avoid 2027 contract delays.
Final Call: Procure FortiGate 40F (2026 FIPS 140-3) variants with TAA compliance and FIPS-SEAL-RED kits immediately. Delay guarantees exposure to “Historical” status failures and audit rejections.
Community Reference & Authority Resources:
Conclusion
The September 21, 2026 CMVP transition is not a suggestion; it is a hard regulatory wall. Deploying FIPS 140-2 modules beyond this date invalidates your ability to bid on new DoD contracts and triggers immediate SC.L2-3.13.11 findings. By migrating to the Fortinet FortiGate 40F (2026 FIPS 140-3) with CMVP Certificate #3000-021, you secure both your network perimeter and your revenue stream. Ensure every unit includes the FIPS-SEAL-RED kit and maintains TAA compliance to avoid supply chain rejection. The cost of upgrade is fixed and known; the cost of non-compliance is the loss of your business. Act now to align your infrastructure with the 2026 mandate.
🔍 Explore More: See all tech guides and tutorials for regulatory impact analysis guide FIPS 140-2 historical transition September 2026 firewall requirements.
Check out TECH Collection Amazon Products