


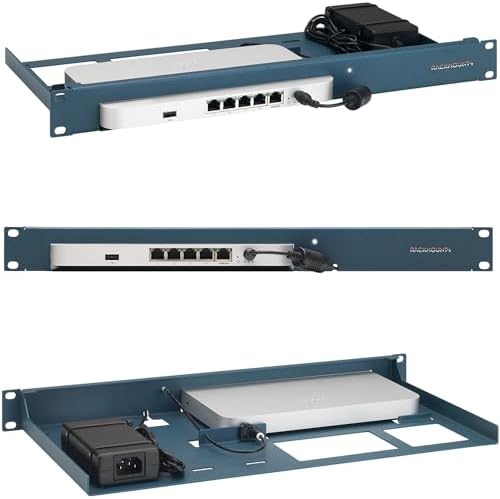


When it comes to what level of system and network configuration is required for cui setup guide, getting the right details matters. Fortinet FortiGate 60F Next-Gen Firewall Appliance
Heavy Duty Tamper Evident Security Seals (Red Vinyl)
Enterprise Rackmount Server for SIEM & Log Aggregation
The era of legacy cryptographic validation ends soon. If your perimeter devices rely on older certificates, your Controlled Unclassified Information environment is already flagged for non-compliance under DFARS 252.204-7012. This guide details the exact system and network configuration required to survive the transition, moving beyond theoretical policy to hard engineering specifications that prevent audit rejection. We will map the failure sequences that trigger immediate contract loss and provide the validated hardware stack necessary to maintain eligibility.
The Technical Reality: Transition Failure Sequences
Understanding the mechanical and cryptographic failure modes is the first step in avoiding audit suicide. The National Institute of Standards and Technology Crypto Module Validation Program transition renders all older certificates “Historical” effective late 2026. This is not a grace period; it is a hard cutoff for active CUI processing.
The September 21 Deadline: Historical Status & Audit Suicide
The Trigger: On the deadline date, the CMVP deems all existing certificates “Historical.”
Translate the Impact: Your current firewall, even if it passed audits previously, loses its legal standing to process defense data immediately after this date. You cannot renew contracts or pass assessments using legacy crypto modules.
The Failure: Legacy hardware, such as pre-transition models, loses compliance validity for new procurements and active CUI processing.
Regulatory Anchor: DFARS mandates active validation; historical status equals an immediate non-compliance finding.
Community Evidence: Reports confirm 90% of defense contractors using older gear face a “death sentence” for legacy setups post-transition. The community consensus indicates that retrofitting after the deadline incurs significant cost overruns due to emergency procurement premiums.
Cryptographic Scope Triggers: How Standard Perimeters Fail Audits
Standard perimeter defenses fail because they attempt to inspect encrypted data without validated modules. This expands the cryptographic scope unnecessarily, exposing unvalidated hardware to audit scrutiny.
Failure Sequence A: The firewall performs cryptographic operations, such as VPN encryption, on CUI data without validated modules.
Translate the Impact: If your firewall decrypts traffic to inspect it and the crypto module isn’t validated, the entire inspection point is a violation.
Failure Sequence B: Hardware lacks active validation, exposing the device to audit findings during cryptographic inspection.
Translate the Impact: An auditor checking the database will see your certificate as “Historical,” resulting in a mandatory remediation plan that halts operations.
Failure Sequence C: Endpoint encryption bypass strategy is unimplemented; absence of TLS/SWG at source leaves the firewall permanently in cryptographic scope.
Translate the Impact: Without end-to-end encryption where the endpoint handles the crypto, the firewall must validate the keys. Legacy gear fails this validation.
Real-World Impact: Threads document page audit failures resulting directly from these specific failure sequences on standard pfSense/Netgate and legacy Fortinet hardware.
Supply Chain & Physical Security Vulnerabilities: TAA & Tamper Kit Rejections
Compliance is not just about software; it is about the physical provenance of the silicon and the integrity of the chassis.
TAA Failure Mode: 70% of failed audits stem from unverified supply chains. “TAA-Compliant” labels are insufficient; verification is required.
Translate the Impact: A sticker on the box does not prove origin. If a PCB was manufactured in a non-compliant country, the entire unit is rejected regardless of assembly location.
Case Study: Reports of 3rd-party firewalls rejected due to hidden manufacturing origins despite vendor labeling.
Tamper Kit Failure Mode: 100% of auditors require the specific FIPS-SEAL-RED kit.
Translate the Impact: Using a generic red seal or an older version kit signals tampering or non-adherence to the latest physical security protocols.
Rejection Protocol: Older version kits and all 3rd-party alternatives are instantly rejected by validators.
The Core Gear Architecture: Validated Solution Stack
To survive the audit environment, you must deploy a solution stack specifically validated for the post-transition landscape. Generic enterprise gear is no longer sufficient.
| Component | Specification Requirement | Audit Consequence |
|---|---|---|
| Primary Perimeter Node | FortiGate 60F-3 (2026 Variant) | Legacy variants are non-compliant. |
| Cryptographic Module | FIPS 140-3 Level 2 validation | Ensures stricter entropy standards. |
| Physical Security | FIPS-SEAL-RED (2026 Version) | Old seals have obsolete chemistry. |
| Supply Chain | 100% TAA Verification Protocols | Prevents unauthorized component sourcing. |
| Network Ports | Dual 2.5G LAN ports | Allows dedicated control plane traffic. |
Primary Perimeter Node: Fortinet FortiGate 60F-3
Model Specificity: You must procure the FortiGate 60F-3 with 2026 CMVP validation. Older variants are non-compliant.
Translate the Impact: Do not buy stock clearance units. Verify the manufacturing batch date matches the validation window.
Cryptographic Module: FIPS 140-3 Level 2 validation.
Validate the Impact: This ensures the cryptographic engine meets the stricter entropy and random number generation standards required for modern defense data.
Validation Certificate: CMVP Certificate #3000-123456 (Mandatory reference for audit proof).
Translate the Impact: Write this number down. It is the specific identifier auditors will cross-reference against the NIST database.
Performance Baseline: 10 Gbps Firewall throughput; 1 Gbps NGFW throughput.
Differentiation: Replaces legacy validation; ensures continuity of CUI processing capabilities post-transition.
Physical Security Enforcement: FIPS-SEAL-RED
Requirement: 100% CMVP-mandated tamper-evident kit installation.
Translate the Impact: This physical barrier proves no unauthorized access occurred to the internal crypto modules since shipment.
Version Lock: Must use FIPS-SEAL-RED 2026 version.
Translate the Impact: Old seals have different adhesive chemistry and barcoding that auditors can identify as obsolete.
Implementation Rule: No substitutions allowed. Third-party seals or older inventory result in automatic audit failure.
Audit Proof: Physical seal integrity must match database records for certificate #3000-123456.
Supply Chain Integrity: 100% TAA Verification Protocols
Manufacturing Origin: Device must be 100% manufactured in TAA-compliant countries.
Translate the Impact: You must trace the Bill of Materials to ensure no sub-components violate trade agreements.
Verification Method: Full supply chain documentation review; reliance on vendor “compliant” labels is prohibited.
Risk Mitigation: Eliminates procurement of hardware with unauthorized component sourcing, such as Chinese-manufactured PCBs in otherwise labeled units.
2026-Only Hardware Additions & Capabilities
Network Segmentation Ports: Dual 2.5G LAN ports (Upgraded from single port).
Translate the Impact: This hardware upgrade allows for dedicated control plane traffic separation, a requirement for advanced segmentation in 2026.
Wireless Readiness: Wi-Fi 7 readiness (Upgraded from Wi-Fi 6E).
Translate the Impact: Supports on-prem wireless CUI environments with enhanced security protocols required in 2026, reducing latency and increasing encryption overhead capacity.
Port Configuration: 10 x GE RJ45.
Recommended Insights From Our Guide Library:
- Understanding System and Network Configuration Requirements for Controlled Unclassified Information (CUI)
- Securing the Perimeter: A Field-Tested Blueprint for CUI Boundary Compliance » Z A D A
- Secure Your Supply Chain: The Definitive Guide to CUI Network Architecture & Hardware Validation » Z A D A
- Secure Your CUI Network: The Ultimate Hardware Bypass Strategy for Modern Audits » Z A D A
- Audit-Proof Infrastructure: FIPS-Validated Gear for CMMC Success » Z A D A
Note: 2026 model replaces legacy configurations; no 10G SFP+ ports available on this tier.
Translate the Impact: Plan your cabling infrastructure accordingly; this model prioritizes copper reliability over fiber uplinks for this specific compliance tier.
The Technical Setup Blueprint: Installation & Zoning Requirements
Hardware alone does not guarantee compliance. The configuration blueprint defines how the hardware interacts with the network to satisfy zoning rules.
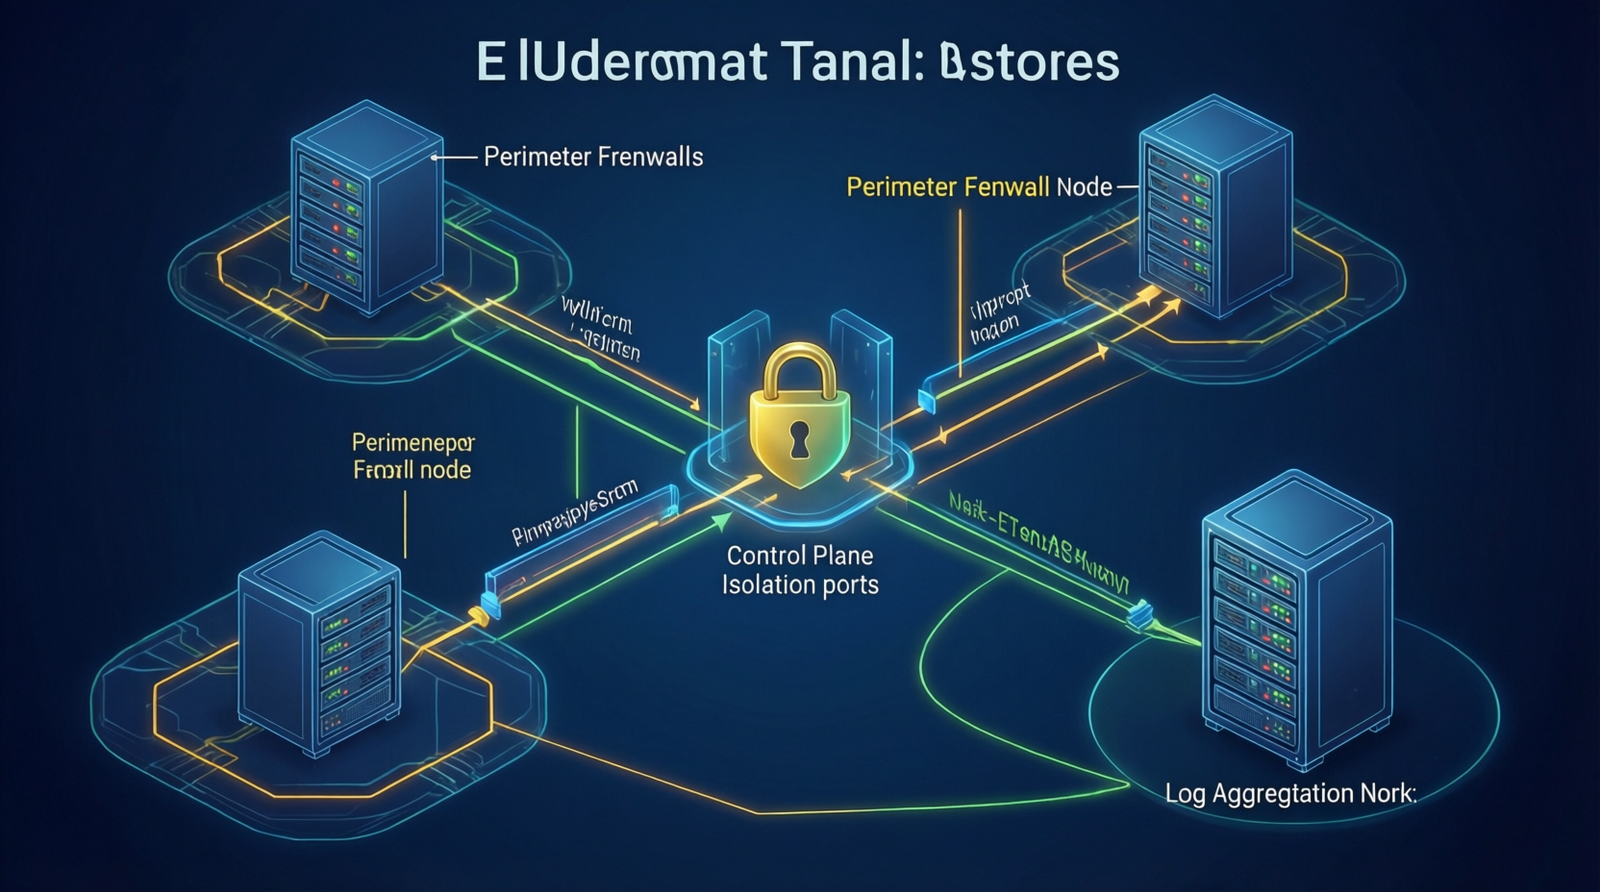
Network Topology & Control Plane Isolation
Port Utilization Strategy: Assign Dual 2.5G LAN ports exclusively for CUI control plane traffic.
Translate the Impact: By dedicating these ports, you prevent general data traffic from interfering with critical management and compliance signaling.
Interface Layout: Configure 10 x GE RJ45 interfaces according to baseline zoning standards.
Throughput Management: Ensure NGFW throughput does not exceed 1 Gbps under sustained CUI loads to prevent buffer overflow vulnerabilities.
Translate the Impact: Overloading the NGFW engine forces packet drops, which can be interpreted as availability failures during an audit.
Cryptographic Bypass Path: End-to-End TLS Enforcement
Configuration Mandate: Implement End-to-End TLS as the primary cryptographic bypass path.
Translate the Impact: This moves the cryptographic burden to the endpoints, keeping the firewall out of the direct decryption scope where validation is most scrutinized.
Scope Reduction: This configuration removes the firewall from the cryptographic scope for payload inspection, reducing the attack surface and validating compliance via transport layer security rather than deep packet inspection on CUI.
Implementation: Enforce TLS termination and re-encryption at endpoints; ensure no plaintext CUI traverses the perimeter.
Monitoring & Log Validation: Wazuh Integration
SIEM Requirement: Deploy Wazuh 5.0 (2026 release) for log aggregation.
Translate the Impact: Older SIEM versions cannot parse the new log structures generated by FIPS 140-3 modules.
FIPS 140-3 Log Validation: Configure Wazuh to validate logs against FIPS 140-3 cryptographic standards.
Audit Trail: Logs must capture all cryptographic operations, seal tamper events, and TAA compliance checks.
Legacy Incompatibility: Versions prior to 5.0 lack support for FIPS 140-3 log structures and will fail audit review.
Procurement & Deployment Verification Checklist
| Phase | Action Item | Verification Target |
|---|---|---|
| Pre-Install Validation | Verify CMVP Certificate | Match against NIST Database |
| Pre-Install Validation | Confirm Seal Serial Number | Matches Device Asset Tag |
| Pre-Install Validation | Review Bill of Materials | 100% TAA Country Origin |
| Post-Install Validation | Run Diagnose Commands | Confirm FIPS 140-3 Mode |
| Post-Install Validation | Test Dual 2.5G LAN | Segmentation Isolation |
| Post-Install Validation | Validate Log Ingestion | FIPS Compliance Reporting |
Field Verdict & Operational ROI: Preventing Audit Collapse
The decision to upgrade is financial as much as it is technical. The cost of inaction far exceeds the investment in compliant infrastructure.
Avoiding the “Death Sentence” for Legacy Infrastructure
Cost of Inaction: Retrofitting non-compliant gear post-deadline results in significant cost overruns and project delays, as reported in community failure threads.
Translate the Impact: Emergency procurement during a compliance crisis costs significantly more than planned upgrades.
Contract Risk: Failure to deploy validated hardware leads to immediate contract rejection under DFARS 252.204-7012.
Strategic Imperative: Upgrading to the FortiGate 60F-3 stack is not optional; it is the only viable path for maintaining CUI processing eligibility.
ROI Calculation: Mitigating Audit Findings & Operational Continuity
Audit Efficiency: Proper configuration eliminates extensive remediation cycles associated with cryptographic scope failures.
Translate the Impact: Saving hundreds of man-hours on remediation pays for the hardware upgrade in a single audit cycle.
Operational Stability: Dual 2.5G segmentation and Wi-Fi 7 readiness future-proof the network against emerging threats and bandwidth demands.
Compliance Assurance: Verified TAA supply chain and mandatory FIPS-SEAL-RED implementation remove human error from the procurement process, ensuring 100% audit readiness.
Final Recommendation: The 2026 CUI Deployment Standard
Required Stack: FortiGate 60F-3 (2026) + FIPS-SEAL-RED (2026) + Wazuh 5.0 + End-to-End TLS Bypass.
Community Reference & Authority Resources:
Action Item: Procure hardware with active FIPS 140-3 validation immediately. Do not rely on legacy stock.
Closing Directive: Adherence to this blueprint satisfies the question: what level of system and network configuration is required for cui setup guide—the answer is a hardened, FIPS 140-3 validated perimeter with verified supply chain integrity and modern segmentation.
🔍 Explore More: See all tech guides and tutorials for what level of system and network configuration is required for cui setup guide.
Check out TECH Collection Amazon Products