
When it comes to fips-seal-red application guidelines for fortinet hardware firewalls, getting the right details matters. FNIRSI LCR-ST1 Smart Tweezers
Andonstar AD246S-M Microscope
GEEKOM A9 Max Mini PC
FIPS-SEAL-RED Application Guidelines for Fortinet Hardware Firewalls: The 2026 CMMC Compliance & Hardware Blueprint
The Technical Reality: Physical Cryptographic Boundary Compromise & Audit Failure
The Chassis Access Vulnerability: Volatile Memory Extraction and Bus-Level Intercepts
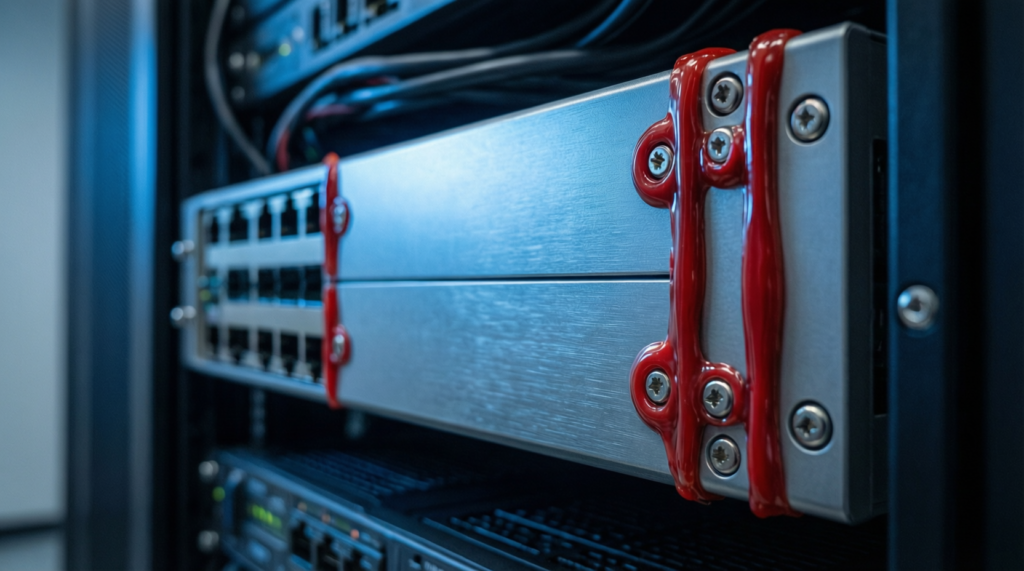
When a FortiGate appliance operates in FIPS mode, the cryptographic module processes Controlled Unclassified Information (CUI) data flows internally. If the physical chassis is accessed without authorization, an attacker could extract volatile memory keys, intercept bus-level data, or flash malicious firmware. The absence of the FIPS-SEAL-RED tamper-evident seal kit on the chassis screws and access panels constitutes a direct violation of physical security controls.
Software-level cryptographic validation is useless without strict physical boundary protection for CUI. Without the seal, the cryptographic boundary is considered compromised regardless of configuration settings.
The CMMC 2.0 Level 2 Trap: Software FIPS CLI Mode vs. Physical FIPS-SEAL-RED Reality
Network engineers frequently report enabling FIPS mode via the FortiGate CLI, assuming this satisfies the cryptographic requirements. This assumption leads to catastrophic failure during a Certified Assessor (CCAA) physical inspection protocol for the perimeter gateway. During a CMMC assessment, the auditor physically inspects the perimeter gateway. If the tamper-evident epoxy or seals are missing, broken, or improperly applied, the auditor will issue a formal finding for SC.L2-3.13.11 (FIPS-validated cryptography).
This failure halts the compliance certification process, preventing the defense contractor from bidding on prime contracts, regardless of the fact that the firewall’s software is fully FIPS-validated and operational.
The Procurement Friction: Irreversible Epoxy, Standalone Kit Bans, and the Over-Provisioning Mandate
Fortinet direct sales channels often refuse to sell the FIPS-SEAL-RED kits as standalone accessories. This forces organizations to purchase entirely new, pre-sealed hardware units or navigate complex special-order processes that delay compliance timelines by months. Furthermore, system administrators express frustration over the irreversible nature of the seals. Once the FIPS-SEAL-RED epoxy is applied, any hardware modification, including routine SSD replacements or RAM expansions, breaks the seal and instantly voids the FIPS validation.
This forces organizations to over-provision hardware specifications at the time of initial purchase, as post-deployment physical scaling is impossible without returning the unit to the manufacturer for a costly and time-consuming re-certification process.
The Core Gear Architecture: 2026 FIPS 140-3 Perimeter & Diagnostic Stack
Cybersecurity & Network Perimeter Architecture: FortiGate 40F/60F, Netgate 1100, and Wazuh
The definitive hardware solution to resolve this physical compliance failure is the deployment of Fortinet FortiGate 40F or 60F appliances paired with the mandatory FIPS-SEAL-RED tamper-evident seal kit. The following table details the performance specifications and certification status of the recommended perimeter gateways.
| Model | Ports | Firewall Throughput | NGFW Performance | Certification Status |
|---|---|---|---|---|
| FortiGate 40F | 5 x GE RJ45 | 5 Gbps | 800 Mbps | FIPS 140-2 Level 2 (Historical Sep 2026) |
| FortiGate 60F | 10 x GE RJ45 | 10 Gbps | 1 Gbps | FIPS 140-2 Level 2 (Historical Sep 2026) |
For environments requiring a bypass, the Netgate 1100 serves as a Cryptographic Bypass with 3x 1 Gbps Switched Ports and a Dual-Core ARM64 Cortex-A53 processor. This is used to bypass FIPS requirements if CUI is encrypted at the endpoint via TLS/SWG. To maintain visibility, SIEM Integration via Wazuh aggregates security event logs for SC.L1-3.13.1 continuous monitoring and correlates raw network traffic with endpoint file integrity.
Micro-Electronics & PCB Diagnostic Architecture: FNIRSI LCR-ST1, Andonstar AD246S-M, and 40 AWG Trace Repair
To maintain the integrity of the supporting infrastructure, precise diagnostic tools are required. The FNIRSI LCR-ST1 Smart Tweezers offer selectable test frequencies of 100 Hz, 1 kHz, and 10 kHz. They feature dual test voltages of 0.3V to prevent parallel component interference and 0.6V. The unit weighs 41g, allowing for handheld precision during bench testing. The Andonstar AD246S-M Microscope features a 7-inch LCD, 3 interchangeable lenses (A, D, L), and 2160P video output. Its 30cm high bracket provides vertical clearance for hot-air rework, and it supports dual-screen HDMI for collaborative inspection.
For physical repairs on the support nodes, PCB Trace Repair Materials include 40 AWG micro-thin copper jumper wire for bridging severed traces on multi-layer populated PCBs under high-magnification stereomicroscopes. These tools ensure that the non-compliant support hardware (like the SIEM server) remains physically intact to validate the compliant perimeter.
DevOps Homelab & Compute Cluster Architecture: GEEKOM A9 Max/A8/A6 and Proxmox VE/OpenZFS Dynamics
The compute layer supporting the compliance stack requires robust resources. The GEEKOM A9 Max Mini PC features an AMD Ryzen AI 9 HX 370 processor with 12 Cores/24 Threads. It supports up to 128 GB DDR5 SODIMM, includes Dual 2.5G RJ45 LAN ports, and has 2x M.2 PCIe Gen4 x4 NVMe slots supporting up to 8 TB storage. It delivers 55 NPU TOPS for local inference tasks. The following table compares the compute specifications across the recommended GEEKOM lineup.
| Model | CPU | RAM Support | LAN Configuration | Storage Slots |
|---|---|---|---|---|
| GEEKOM A9 Max | Ryzen AI 9 HX 370 | Up to 128 GB DDR5 | Dual 2.5G RJ45 | 2x M.2 PCIe Gen4 x4 |
| GEEKOM A8 | Ryzen 9 8945HS | 64 GB DDR5 | Single 2.5G LAN | 1x M.2 PCIe Gen4x4 |
| GEEKOM A6 | Ryzen 7 6800H | 64 GB DDR5 | Single 2.5G LAN | Standard M.2 |
These machines run Proxmox VE & OpenZFS Dynamics where KVM/LXC resource allocation requires generous multi-core processing. OpenZFS Adaptive Replacement Cache (ARC) requires baseline DDR5 memory to prevent I/O bottlenecks. Dual LAN enables control plane API segmentation, isolating management traffic from data plane flows.
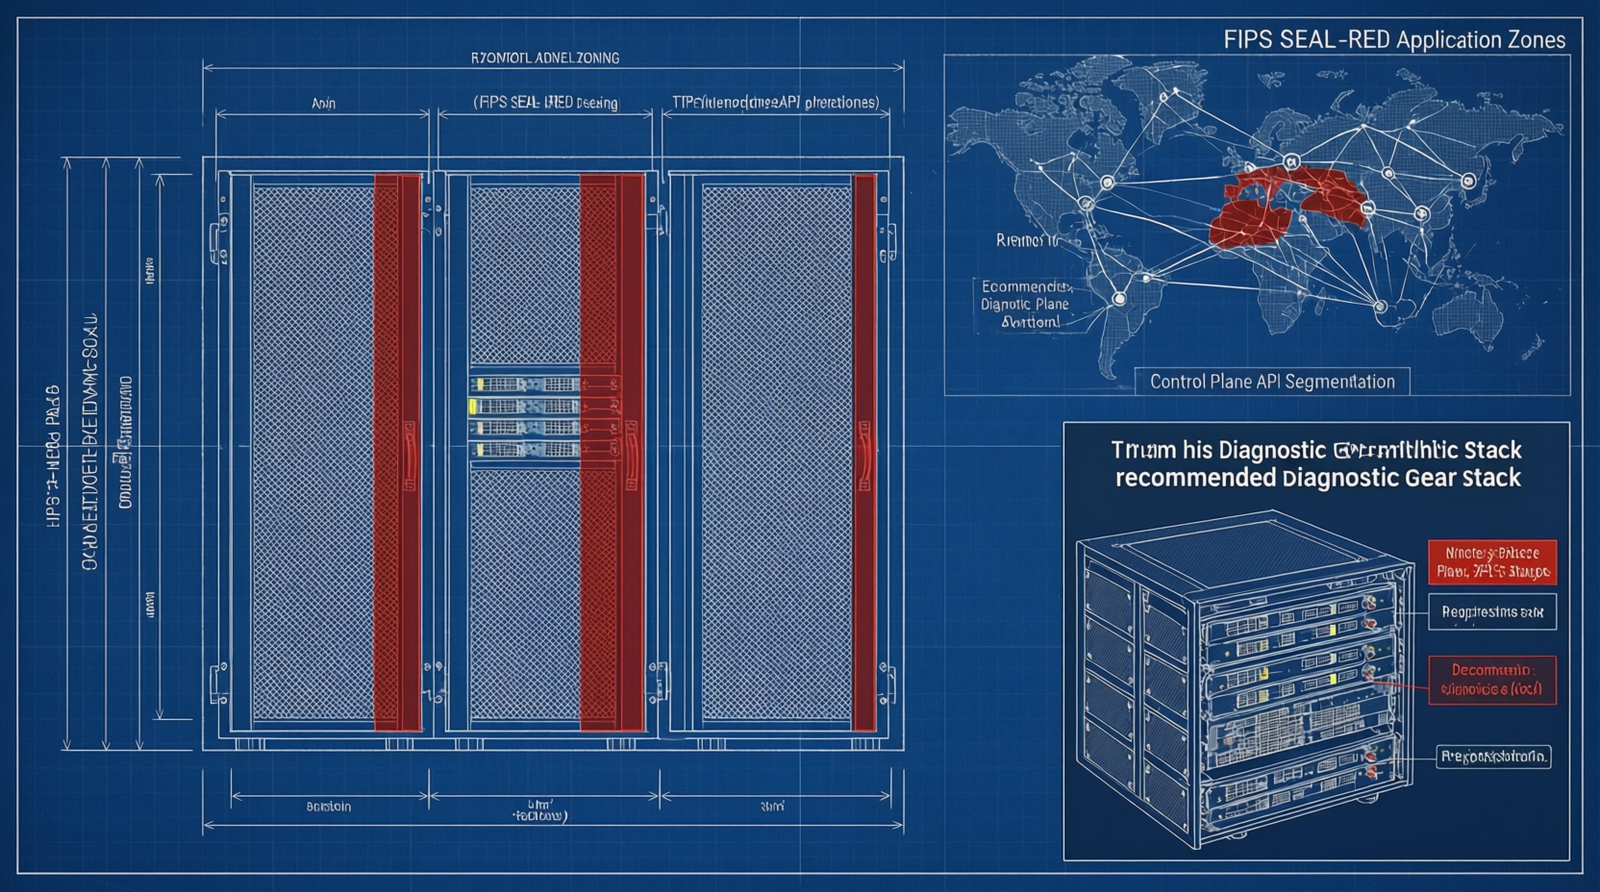
The Technical Setup Blueprint: FIPS-SEAL-RED Application & Infrastructure Zoning
Pre-Rack Provisioning & The Irreversible Seal Mandate
Hardware must be fully provisioned prior to final deployment and sealing. You must install all RAM, configure storage, and set port configurations before applying the seal. This rule exists because breaking the seal voids the validation. On September 21, 2026, the CMVP will move all remaining active FIPS 140-2 certificates to the Historical list. Federal procurement guidelines dictate that historical modules must not be included in new procurements.
Therefore, FIPS 140-3 Level 2 is the absolute baseline for upcoming Department of Defense contract bids. Planning your hardware capacity now avoids the inability to scale later without losing compliance status.
FIPS-SEAL-RED Epoxy and Tamper-Evident Label Application Protocol
Apply the specialized tamper-evident labels and epoxy resins over chassis screws and panel seams immediately upon racking. The FIPS-SEAL-RED kit consists of specialized tamper-evident labels and epoxy resins designed to be applied over the chassis screws and panel seams immediately upon racking. This action satisfies FIPS 140-3 Level 2 physical security requirements for the FortiGate hardware. The physical compliance requirement mandates that the seal covers all potential entry points to the cryptographic module.
Any attempt to remove the seal leaves visible evidence of tampering, which triggers an immediate audit finding.
Network Zoning and Control Plane API Segmentation
Map out the integration of the perimeter gateways with the DevOps compute cluster to ensure logical separation. Detail the use of Dual 2.5G RJ45 LAN configurations to enable strict control plane API segmentation. This ensures management traffic is isolated from data plane CUI flows. By segmenting the control plane, you reduce the attack surface exposed to the internet-facing data interfaces. This architecture supports the Wazuh SIEM aggregation by providing a dedicated channel for log ingestion that does not compete with production traffic bandwidth.
Field Verdict & Operational ROI: Securing Prime Defense Contracts
Neutralizing the CCAA Physical Inspection Failure Point
Applying the FIPS-SEAL-RED kit is not just a hardware accessory, but the literal key to passing the physical boundary inspection. This applies under NIST SP 800-171, CMMC 2.0 Level 2, and DFARS 252.204-7012. The operational ROI lies in avoiding the formal finding for SC.L2-3.13.11. Without this step, the compliance certification process halts. This failure prevents the defense contractor from bidding on prime contracts.
The cost of the seal kit is negligible compared to the revenue loss from a failed audit.
The 2026 FIPS 140-3 Procurement Imperative and Long-Term Compliance ROI
Community Reference & Authority Resources:
Frame the recommended gear stack as an essential investment. The stack includes FortiGate 40F/60F plus pre-applied FIPS-SEAL-RED plus over-provisioned specs. This combination secures the organization against the September 21, 2026 transition. Avoid the catastrophic cost of failed audits, delayed compliance timelines, and the inability to bid on prime federal contracts due to historical FIPS 140-2 module procurement violations. Investing in the correct hardware and sealing protocol now ensures long-term eligibility for government work.
The financial reality dictates that compliance is a prerequisite for revenue, not an optional overhead.
🔍 Explore More: See all tech guides and tutorials for fips-seal-red application guidelines for fortinet hardware firewalls.
Check out TECH Collection Amazon Products