

When it comes to Proxmox VE network segmentation tutorial with dual 2.5G LAN, getting the right details matters. Recommended Products:
GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, 128GB DDR5)
FNIRSI LCR-ST1 Smart LCR Tweezers (0.3V/0.6V Test Voltage)
Andonstar AD246S-M Digital Microscope (2160P Video Output)
Eradicating the Single-NIC Trap: Dual 2.5G LAN Architecture for CMMC Compliance and Zero-Downtime Virtualization
In production and advanced homelab environments, the absence of physical and logical network segmentation on virtualization hosts creates a cascading infrastructure failure mode characterized by resource contention, security vulnerabilities, and compliance violations.
When a Proxmox VE host relies on a single network interface or a flat, unsegmented virtual bridge architecture, management traffic, high-throughput storage replication, and untrusted tenant traffic share the same broadcast domain, resulting in severe broadcast storms, hypervisor API timeouts, and immediate audit non-compliance under DFARS 252.204-7012.
The Technical Reality: Infrastructure Collapse and the “Single-NIC Trap”
The “Single NIC Trap” and Management Plane Starvation
System administrators frequently document the “single NIC trap,” where users attempt to segment traffic using VLANs on a single physical port (`vmbr0` with VLAN-aware enabled). While logically segmented, this setup fails to provide true physical isolation, causing massive CPU interrupt overhead and failing to prevent storage replication traffic from starving the management plane.
A recurring complaint involves the Proxmox Web GUI becoming entirely unresponsive during heavy Ceph or OpenZFS replication events, as management packets are queued behind massive storage payloads on the single physical link, requiring physical separation of the control plane from the data plane to resolve queue depth limits.
Broadcast Storms and I/O Saturation
The cascading failure mode occurs when untrusted tenant traffic, management packets, and high-throughput storage replication share a flat broadcast domain. This results in hypervisor API timeouts, VM lockups, and severely degraded OpenZFS ARC performance.
In a saturated environment, the hypervisor kernel spends excessive cycles processing interrupt requests rather than executing guest instructions, and this degradation compounds exponentially as packet collision rates increase, allowing a rogue container to flood the switch buffer and effectively DoS your own management interface.
The Compliance Death Spiral
Flat network topologies directly violate NIST SP 800-171 and CMMC 2.0 boundary protection requirements, introducing lateral movement vulnerabilities that trigger immediate audit non-compliance under DFARS 252.204-7012 when CUI workloads share domains with untrusted tenants.
Auditors do not accept logical VLAN separation on a shared physical uplink as sufficient boundary protection for CMMC Level 2; they require demonstrable isolation between general IT environments and those handling Controlled Unclassified Information, meaning storage replication traffic traversing the same physical path as public-facing web servers constitutes a fundamental design flaw inviting regulatory penalties.
The 1Gbps Physical Bottleneck
Legacy 1Gbps interfaces physically prevent the throughput required to saturate modern DDR5 memory speeds and high-density NVMe storage replication, creating an artificial ceiling on cluster performance.
Modern PCIe Gen 5×4 NVMe drives can sustain sequential read/write speeds exceeding 10 GB/s, while a 1Gbps network link caps at roughly 125 MB/s, causing the storage stack to back up, fill RAM buffers, and force the system to page to disk, which stalls the entire virtualization host and renders high-speed memory and storage investments useless.
The Core Gear Architecture: 2026 High-Density Mini PC Cluster Stack
Compute Node Engineering
Deploying the 2026 hardware standard requires the GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, 128GB DDR5), engineered to support strict physical network segmentation.
This platform features the AMD Ryzen AI 9 HX 370 processor with Zen 5 architecture, 12 cores, 24 threads, and an XDNA 2 neural processing unit delivering 55 NPU TOPS for local AI workloads, while supporting up to 128 GB of dual-channel DDR5-5600 SODIMM memory to allocate massive pools to the OpenZFS ARC and multiple virtual machines simultaneously.
Storage is handled by dual M.2 PCIe Gen 5×4 NVMe slots, delivering the sequential read/write throughput required to prevent I/O bottlenecks during storage replication, allowing you to run the hypervisor, firewall, and SIEM locally without external dependencies.
Network PHY & Out-of-Band Specifications
Utilizing dual 2.5G RJ45 LAN ports driven by Intel i226-V PHY controllers is mandatory for this architecture. These controllers support 802.1Q VLAN tagging and Link Aggregation Control Protocol (LACP), ensuring robust link management.
Integrated with Wi-Fi 7 (IEEE 802.11be), the system simulates traditional IPMI/iDRAC out-of-band management capabilities, resolving the lack of dedicated management cards found in compact form factors and maintaining connectivity even if the wired management VLAN is compromised.
Cryptographic Compliance Bypass (FIPS 140-3)
To address the impending September 21, 2026, CMVP transition moving all legacy FIPS 140-2 certificates to Historical status, the hardware solution integrates FIPS 140-3 validated endpoint encryption modules.
This allows the physical node to encrypt CUI at the endpoint level before it traverses the virtualized network, successfully bypassing the requirement for a FIPS-validated perimeter firewall while maintaining strict CMMC Level 2 compliance and ensuring data remains encrypted and unreadable to unauthorized actors even if the network perimeter is breached.
Check out TECH Collection Amazon Products
Perimeter Hardware & Physical Security
Deploying the Fortinet FortiGate 60F (10 x GE RJ45, 10 Gbps throughput) operating at FIPS 140-2 Level 2 is essential for legacy compliance environments. This device mandates the FIPS-SEAL-RED tamper kit to ensure hardware integrity.
While the endpoint encryption handles the data, the perimeter firewall enforces the network boundaries, and the 10 Gbps throughput ensures the firewall does not become a choke point for the 2.5G internal nodes, while the tamper kit provides physical assurance that cryptographic keys have not been compromised through hardware intrusion.
Micro-Electronics & PCB Diagnostic Arsenal
Equipping the hardware maintenance tier with FNIRSI LCR-ST1 Smart LCR Tweezers (0.3V/0.6V Test Voltage) is vital for precise component testing. These tools offer 100 Hz, 1 kHz, 10 kHz test frequencies and 0.3V / 0.6V dual test voltage for in-circuit SMD measurement.
This low-voltage capability prevents false parallel circuit readings and protects sensitive logic during bench testing, while the Andonstar AD246S-M Digital Microscope (2160P Video Output) provides 30cm high bracket clearance, 7-inch LCD, dual-screen HDMI output, and 2160P video clarity necessary for repairing severed traces on multi-layer PCBs surrounding the 2.5G LAN magnetics and PHY chips.
The Technical Setup Blueprint: Proxmox VE Dual 2.5G LAN Segmentation
Physical to Virtual Bridge Mapping & Zoning
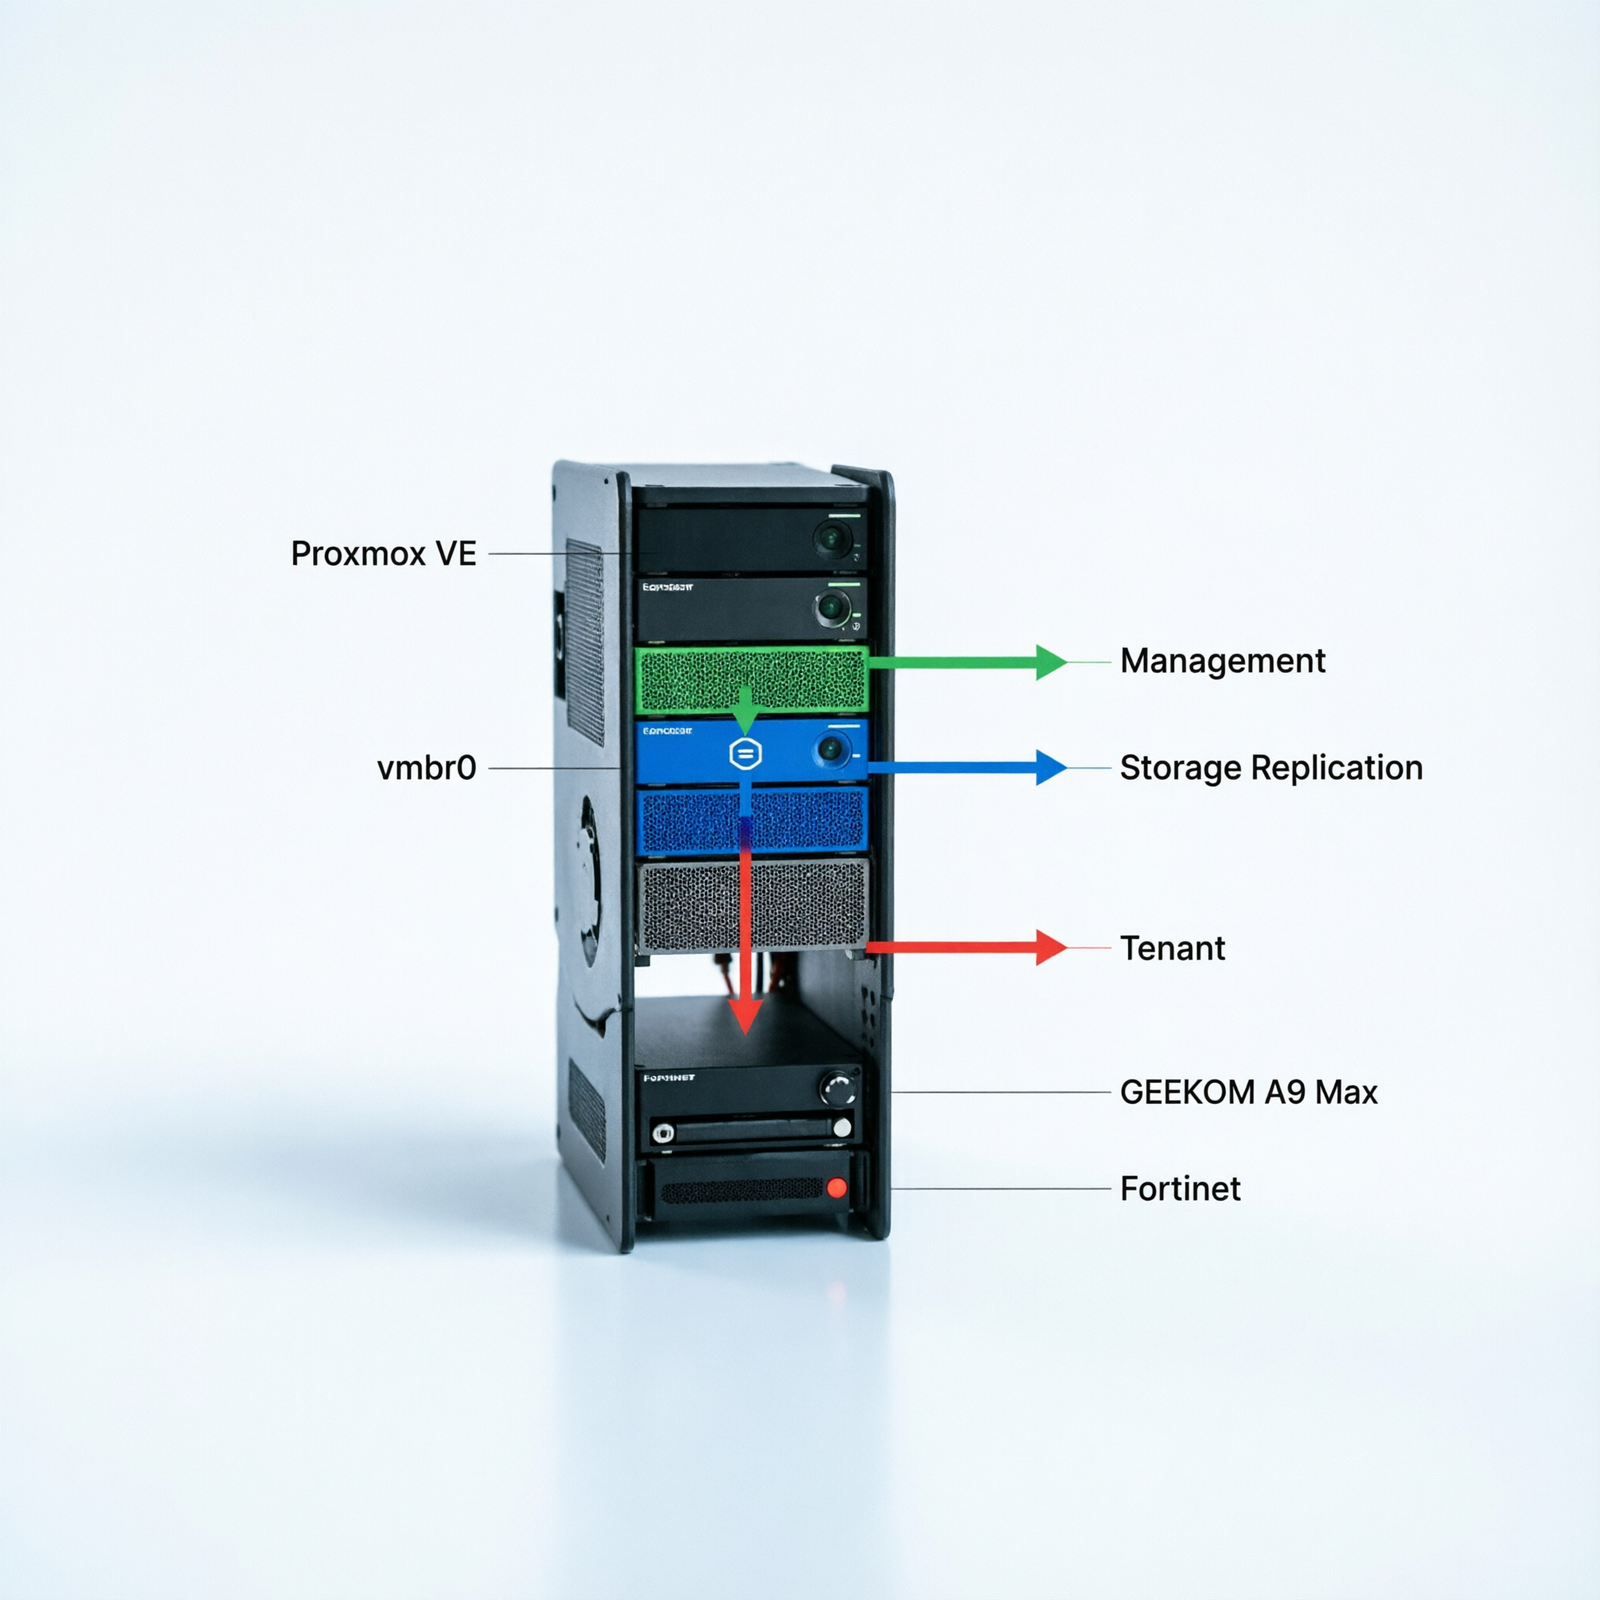
Configuring strict physical isolation begins with mapping `vmbr0` (Port 1) for Management/GUI and `vmbr1` (Port 2) for Storage/Replication/Ceph. Port 1 connects to your trusted management switch, while Port 2 connects directly to storage peers or a dedicated storage switch.
| Virtual Bridge | Physical Port | Subnet/Config | Function |
|---|---|---|---|
| vmbr0 | Port 1 | 192.168.1.x (Tagged) | Management/GUI |
| vmbr1 | Port 2 | 10.0.0.x (Untagged) | Storage/Replication/Ceph |
This physical separation ensures that storage traffic never contends with management traffic on the wire, and if the storage network floods, the management interface remains responsive because it resides on a completely different physical cable and switch port.
Memory & Storage Allocation Rules
Partitioning the 128 GB DDR5-5600 pool requires allocating exactly 64 GB DDR5 to the OpenZFS ARC and 64 GB DDR5 to VM workloads. This split maximizes cache efficiency without starving the guest operating systems.
| Resource | Configuration | Purpose |
|---|---|---|
| DDR5 Memory | 64 GB OpenZFS ARC / 64 GB VM Workloads | Maximize cache efficiency without starving guests |
| NVMe Boot | RAID 1 Mirror | Hypervisor high availability |
| NVMe Storage | RAID 0 Stripe | Maximum throughput for active workloads |
Configuring the dual NVMe drives as a RAID 1 mirror for the hypervisor boot ensures high availability for the OS itself, while a RAID 0 stripe for VM storage maximizes throughput for the active workload, balancing redundancy for the control plane with performance for the data plane.
Virtualized Firewall & SIEM Deployment
Deploying the Netgate pfSense Plus VM on `vmbr0` maps 3 x 1 Gbps virtual switched ports to the physical 2.5G interfaces, creating a robust software-defined perimeter.
The Wazuh manager VM is deployed on `vmbr1`, with agents on the Proxmox host and all VMs forwarding logs exclusively via the dedicated storage VLAN, ensuring that security telemetry does not traverse the public or management networks and preventing log flooding from impacting user-facing services.
Simulating IPMI via Dedicated Management VLANs
Dedicating Port 1 (`vmbr0`) exclusively to a management VLAN guarantees hypervisor accessibility for emergency remediation. This setup ensures that the management plane survives even if the primary tenant network experiences a catastrophic broadcast storm.
Since mini PCs often lack dedicated out-of-band management ports, this virtual IPMI simulation is critical, allowing you to reboot, reconfigure, or recover the host remotely without physical access, which is non-negotiable for remote deployments where physical intervention is costly or impossible.
Field Verdict & Operational ROI: Securing the 2026 Virtualization Perimeter
Eradicating Downtime and Resource Contention
Physical 2.5G isolation definitively solves the “single NIC trap,” preventing multi-hour GUI lockouts and eliminating storage-induced hypervisor API timeouts.
By separating the traffic flows, you unlock full OpenZFS ARC performance because the cache is no longer competing with management packets for bandwidth, resulting in a stable, predictable environment where performance scales linearly with hardware additions and mean time to recovery is significantly reduced.
Audit-Ready Architecture & Cost Avoidance
Achieving immediate, verifiable CMMC Level 2 and NIST SP 800-171 compliance avoids the massive capital expenditure of upgrading perimeter firewalls. Leveraging FIPS 140-3 endpoint encryption navigates the 2026 CMVP transition efficiently.
Instead of replacing entire network segments, you secure the endpoints and enforce boundaries logically and physically where it counts, reducing the total cost of ownership while increasing security posture and demonstrating to auditors that you understand the nuance of modern compliance requirements beyond simple checkbox exercises.
The Mandatory 2026 Hardware Baseline
Transitioning from power-hungry enterprise rack servers to the GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, 128GB DDR5) dual 2.5G LAN mini PC cluster is the only viable path to supporting DDR5/NVMe throughput while maintaining strict physical network segmentation.
The density and efficiency of this hardware allow for localized clustering without the noise and heat of legacy racks, representing the future of edge computing and secure virtualization, and adopting this baseline now positions your infrastructure ahead of the curve for the increased demands of AI workloads and stricter data sovereignty laws.
Conclusion
Community Reference & Authority Resources:
The shift from flat, single-NIC architectures to physically segmented dual 2.5G LAN environments is not merely an upgrade; it is a necessity for survival in the modern threat landscape.
By implementing the GEEKOM A9 Max Mini PC (AMD Ryzen AI 9 HX 370, 128GB DDR5) cluster with strict `vmbr0` and `vmbr1` zoning, you eliminate the “Single-NIC Trap” that causes management plane starvation and compliance failures, gaining immediate immunity against broadcast storms, storage saturation, and lateral movement attacks while securing your perimeter with tools like the FNIRSI LCR-ST1 Smart LCR Tweezers (0.3V/0.6V Test Voltage) and Andonstar AD246S-M Digital Microscope (2160P Video Output) for hardware integrity.
🔍 Explore More: See all tech guides and tutorials for Proxmox VE network segmentation tutorial with dual 2.5G LAN.
Check out TECH Collection Amazon Products