
When it comes to step by step guide pfSense CUI boundary protection setup tutorial, getting the right details matters. Netgate 1100 Firewall Appliance
GEEKOM A9 Mini PC
FNIRSI LCR-ST1 Smart LCR Tweezers
Step by Step Guide pfSense CUI Boundary Protection Setup Tutorial: The 2026 FIPS-Compliant Architecture Blueprint
The Technical Reality / The Failure Point: Why Standard pfSense Triggers Immediate DFARS Audit Failure
Standard pfSense deployments in Controlled Unclassified Information (CUI) environments fail compliance immediately upon inspection. This is not a configuration error; it is an architectural violation of cryptographic mandates.
When auditors examine external boundary protection devices under NIST SP 800-171 and CMMC 2.0, they verify the presence of validated cryptographic modules. The absence of these modules results in immediate disqualification regardless of firewall rule complexity.
The SC.L2-3.13.11 Cryptographic Gap
The control SC.L2-3.13.11 mandates that external boundary protection devices performing cryptographic operations on CUI must utilize FIPS 140-2 or FIPS 140-3 validated modules. Standard Netgate pfSense community hardware lacks active Cryptographic Module Validation Program (CMVP) certification.
When a pfSense appliance terminates virtual private networks or inspects encrypted CUI traffic without this validation, it triggers an immediate audit failure under DFARS 252.204-7012. You cannot patch software to fix a hardware certification gap. If the silicon does not hold the CMVP certificate, the boundary protection device is non-compliant regardless of firewall rule accuracy.
The September 21, 2026 CMVP Transition
The regulatory landscape shifts decisively on September 21, 2026. On this date, the National Institute of Standards and Technology (NIST) relegates all remaining FIPS 140-2 certificates to Historical status.
This transition renders legacy compliant hardware obsolete for new federal procurements. Any system relying on FIPS 140-2 validated components after this date faces immediate disqualification in contract bidding. Organizations must deploy FIPS 140-3 validated hardware now to avoid infrastructure obsolescence before the fiscal year ends.
SC.L1-3.13.1 Continuous Monitoring Failure
Relying solely on local pfSense syslog daemons fails the SC.L1-3.13.1 continuous monitoring requirement. Decentralized logs lack the tamper-evident centralization required for audit-ready Security Information and Event Management (SIEM) correlation.
If log files reside locally on the firewall disk, an attacker with root access can alter them to hide intrusion evidence. To pass audit, you must forward telemetry to a separate, hardened SIEM host where logs are immutable and correlated in real-time. Local storage is insufficient for federal-grade defense.
The Core Gear Architecture: 2026 Hardware Solutions for CUI Perimeter Defense
To resolve the cryptographic compliance failure, the architecture must either deploy a turnkey FIPS-validated commercial gateway or implement an endpoint-level encryption bypass utilizing a TAA-compliant Netgate appliance.
Turnkey Perimeter Gateway Standard
For organizations requiring a plug-and-play perimeter gateway that satisfies auditors out-of-the-box in the 2026 landscape, the Fortinet FortiGate 60F is the mandatory hardware standard. It comes equipped with FIPS 140-3 validated cryptographic modules embedded in the ASIC.
Check out TECH Collection Amazon Products
The FortiGate 60F provides 10 GE RJ45 ports supporting 10 Gbps aggregate firewall throughput. It leverages dedicated ASIC hardware acceleration for Next-Generation Firewall inspection. This ensures that deep packet inspection does not degrade network performance while maintaining cryptographic integrity.
The Endpoint Encryption Bypass Stack
For budget-conscious IT administrators utilizing the endpoint encryption bypass strategy—where CUI is encrypted via FIPS-validated Transport Layer Security at the endpoint before traversing the network—the Netgate 1100 running pfSense Plus serves as the optimal routing and access control node.
The Netgate 1100 features a Dual-Core ARM64 Cortex-A53 processor and 3 x 1 Gbps Switched Ports.
While TAA Compliant, it lacks active FIPS validation on the box itself. Therefore, it requires the endpoint encryption bypass strategy to remain compliant. This offloads the cryptographic burden to the client device rather than the network perimeter.
High-Density SIEM Compute Node
To satisfy centralized log management, a high-performance DevOps node is required to host the Wazuh SIEM platform. The GEEKOM A9 Max serves as the hypervisor host for this function.
The GEEKOM A9 Max utilizes the AMD Ryzen AI 9 HX 370 processor and 128 GB of dual-channel DDR5 SODIMM memory. It features Dual 2.5G RJ45 LAN interfaces.
These physical ports enable strict network segmentation between the control plane API and node-to-node cluster communications, ensuring management traffic never mixes with audit data streams.
Forum-Validated Tradeoffs
Technical communities highlight severe friction points when configuring pfSense for CUI environments. Engineers document fragmented threads detailing CMMC audit failures caused by auditors rejecting pfSense for boundary protection due to the missing FIPS validation certificate.
A major consensus pain point involves the technical complexity of the endpoint encryption bypass workaround. Sysadmins report that configuring Secure Web Gateways and enforcing local application encryption across heterogeneous endpoints is significantly more labor-intensive than deploying a pre-validated commercial firewall. Practitioners also heavily criticize the acoustic and thermal footprint of enterprise-grade FIPS firewalls, driving a strong preference for silent, compact Netgate appliances paired with robust endpoint encryption, despite the initial configuration overhead.
The Technical Setup Blueprint: Zoning, Telemetry, and Physical Diagnostics
The exact technical specifications for the CUI boundary protection setup span multiple architectural domains. Precision here determines whether the system passes or fails a physical security inspection.
Network Perimeter Zoning & 802.1Q Tagging
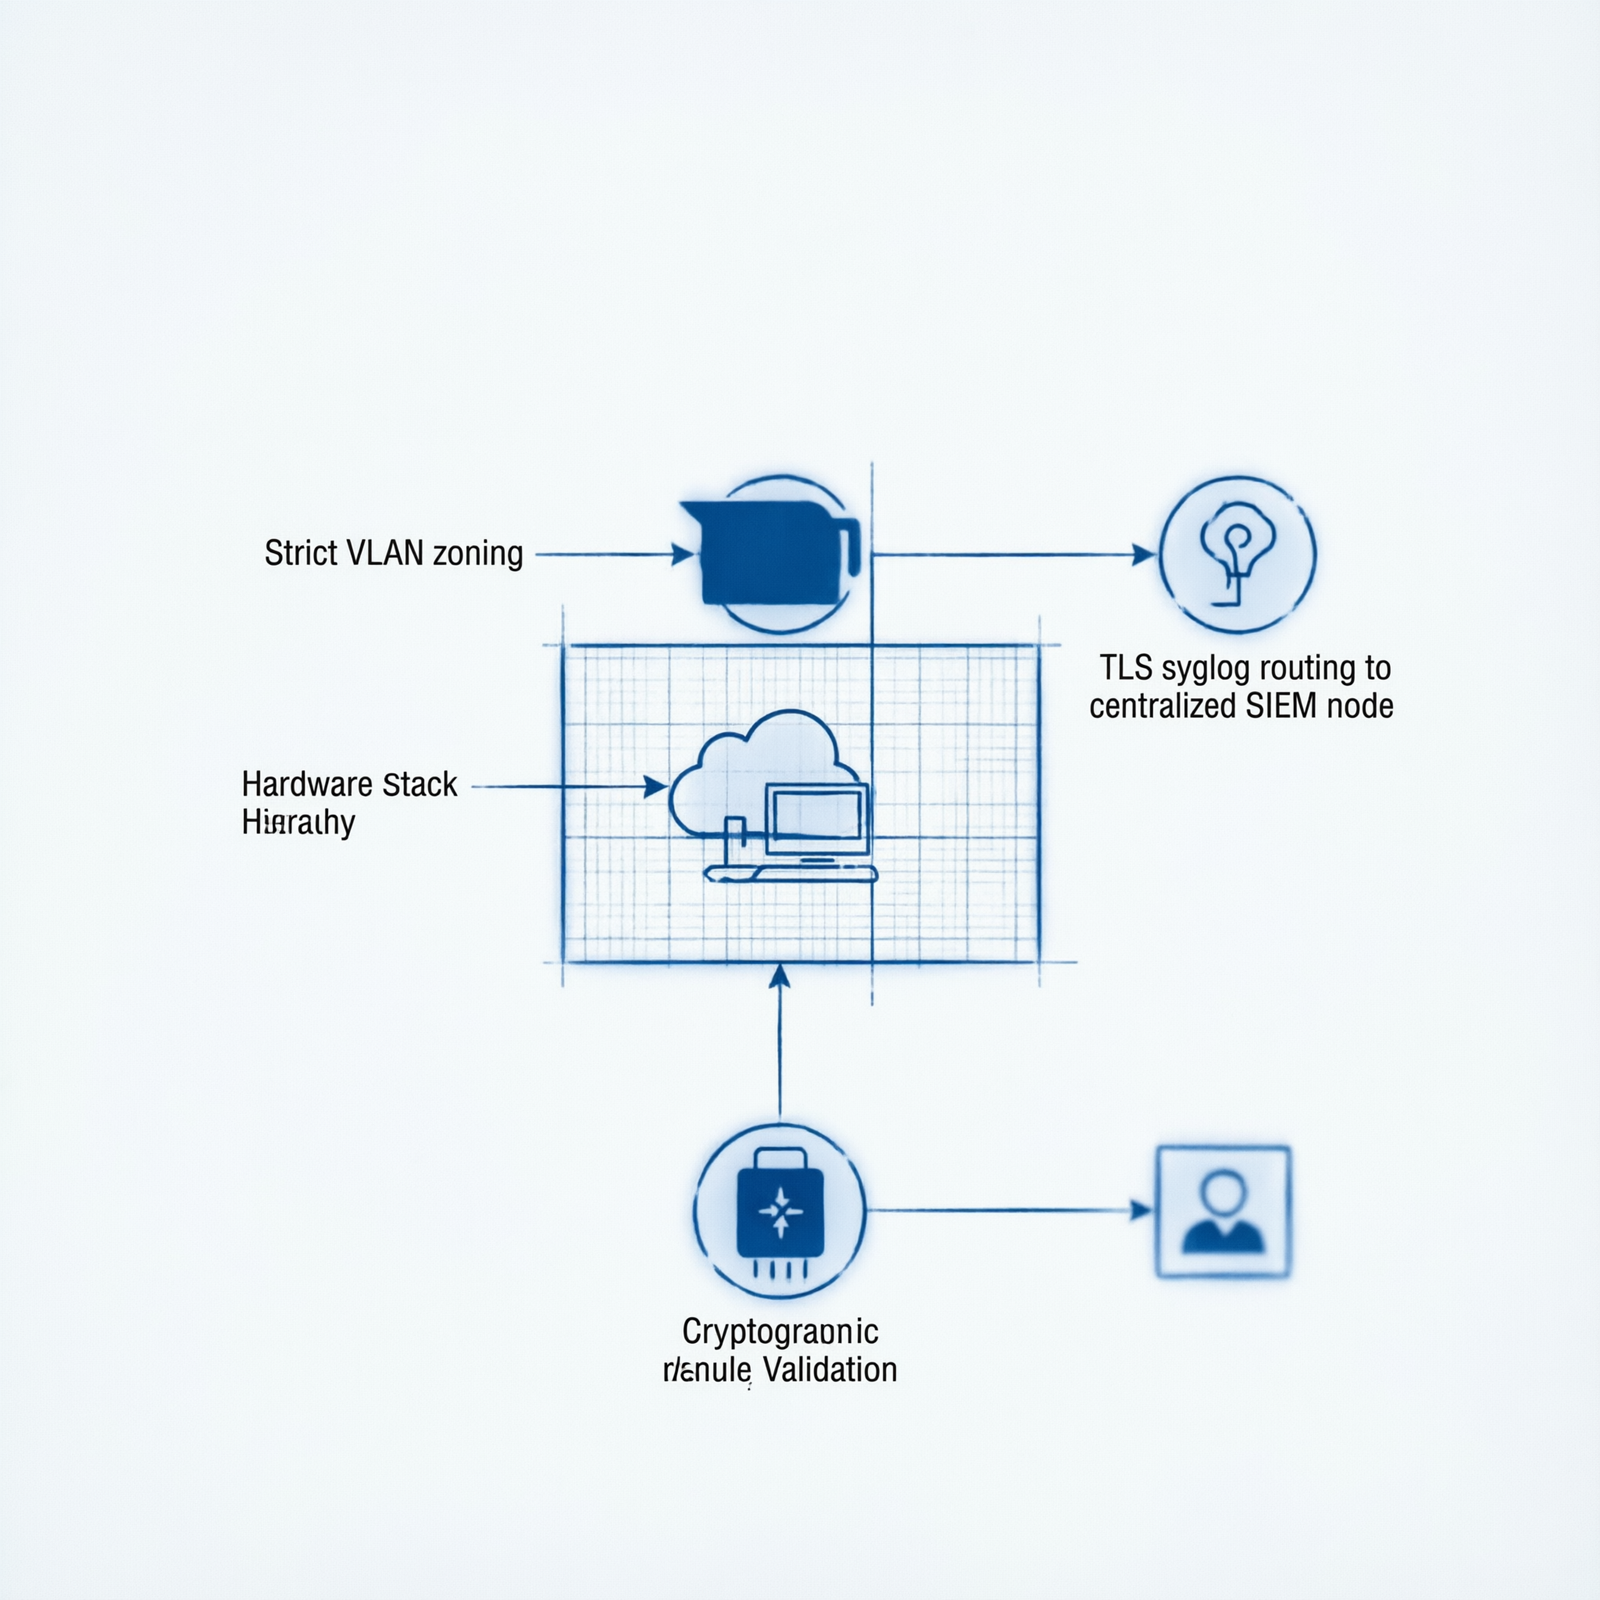
Within the Cybersecurity and Network Perimeter Architecture, the Netgate 1100 utilizes three 1 Gbps switched ports to separate the management plane, the CUI transit VLAN, and the external WAN interface via 802.1Q tagging.
You must configure the switch ports to strictly isolate the management plane from the CUI transit VLAN. This prevents lateral movement if the external WAN interface is compromised. Traffic isolation ensures that administrative access cannot traverse the same logical path as sensitive data payloads.
Secure Telemetry Routing & Packet Preservation
Recommended Insights From Our Guide Library:
- The CMMC-Auditable Firewall Bypass: How to Keep pfSense Out of CMVP Scope While Meeting FIPS 140-3 » Z A D A
- The Silent Audit Killer: Why Your Firewall Logs Are Failing CMMC and How to Fix It » Z A D A
- Mastering Log Integrity: The Hardware Blueprint for Unbreakable SIEM and Firewall Compliance » Z A D A
Syslog forwarding to the Wazuh manager must be configured over Transport Layer Security on port 1514 to ensure log integrity in transit. Community diagnostics reveal that integrating pfSense with open-source SIEM platforms like Wazuh often results in dropped syslog packets during high-throughput events.
Configuring TLS on port 1514 eliminates the dropped syslog packets common in high-throughput open-source SIEM integrations. It also encrypts the log stream, preventing attackers from injecting false events or stripping critical alerts during transmission.
Micro-Electronics & PCB Diagnostic Maintenance
Physical hardware maintenance requires precision tools to verify circuit integrity without damaging sensitive components.
In-Circuit Measurement
Utilizing FNIRSI LCR-ST1 Smart LCR Tweezers allows for in-circuit measurement using selectable test frequencies of 100 Hz, 1 kHz, and 10 kHz. The dual test voltage modes of 0.3V and 0.6V prevent forward-biasing adjacent semiconductor junctions during diagnostic probing.
This protects the motherboard from accidental damage while verifying component health.
Visual Trace Verification
Deploying the Andonstar AD246S-M Digital Microscope provides a 30cm high bracket working clearance for hot-air rework. It features a 7-inch LCD with dual-screen HDMI output for zero-latency trace verification using 40 AWG micro-thin jumper wire.
This level of visual clarity is essential for identifying cold solder joints or short circuits on multi-layer printed circuit boards.
DevOps Homelab Compute Cluster Configuration
The DevOps Homelab and Compute Cluster Architecture dictates that the Wazuh SIEM and OpenZFS storage backend require a high-density compute node.
Physical Segmentation
Leveraging the GEEKOM A9 Max dual 2.5G RJ45 LAN ports enables strict physical network segmentation between the control plane API and node-to-node cluster communications. This separation ensures that heavy logging traffic does not saturate the management interface.
Storage Latency Prevention
The OpenZFS Adaptive Replacement Cache memory allocation is mathematically defined to prevent storage latency during high-volume audit log writes. You must calculate the target cache size based on total physical memory to avoid swapping.
ARC_target = (RAM_total – RAM_OS_reserved) / 2
Check out TECH Collection Amazon Products
Where RAM_total represents the 128 GB physical DDR5 capacity, and RAM_OS_reserved denotes the baseline memory allocated to the Proxmox VE host and critical Linux Containers. Ignoring this calculation causes write bottlenecks that delay audit log ingestion.
Field Verdict & Operational ROI: Securing the 2026 Federal Procurement Mandate
The decision to invest in specific hardware stacks is not merely about functionality; it is about financial risk mitigation.
Mitigating the Endpoint Bypass Overhead
Calculating the long-term operational ROI of deploying pre-validated commercial firewalls versus the recurring labor costs of maintaining complex endpoint encryption bypasses on the Netgate 1100 reveals a stark reality.
While the Netgate 1100 has a lower upfront cost, the labor hours required to enforce encryption policies across every endpoint add up quickly. Deploying the Fortinet FortiGate 60F reduces ongoing administrative overhead. The higher capital expenditure pays for itself in reduced man-hours spent troubleshooting endpoint compliance issues.
Audit-Ready Centralization
Demonstrating how dedicated logging VLANs and Wazuh File Integrity Monitoring (FIM) definitively close the SC.L1-3.13.1 continuous monitoring gap transforms decentralized vulnerabilities into tamper-evident compliance assets.
By centralizing logs on the GEEKOM A9 Max, you create a single source of truth that auditors can verify instantly. This removes the ambiguity of distributed logging systems where evidence could be lost or altered.
Final Hardware Investment Mandate
Framing the exact 2026 gear stack not as an optional upgrade, but as a mandatory capital expenditure is necessary to prevent catastrophic DFARS 252.204-7012 audit failures and contract terminations.
Waiting until the September 21, 2026 deadline creates a supply chain bottleneck and price surge. Securing FIPS 140-3 validated hardware now ensures your organization remains eligible for federal contracts without interruption. This is not just IT procurement; it is business continuity planning.
Conclusion
Community Reference & Authority Resources:
The path to CUI boundary protection compliance requires abandoning legacy assumptions about open-source firewalls. Standard pfSense configurations trigger immediate audit failures due to cryptographic gaps that software updates cannot fix. By deploying FIPS 140-3 validated gateways like the FortiGate 60F or implementing rigorous endpoint bypass strategies with the Netgate 1100, you align with the 2026 regulatory mandate.
Centralizing telemetry on a high-density compute node like the GEEKOM A9 Max ensures your audit logs remain tamper-evident and performant. Precision maintenance tools like the FNIRSI LCR-ST1 Smart LCR Tweezers and Andonstar AD246S-M guarantee the physical integrity of your hardware infrastructure. Implementing this blueprint secures your deployment against both cyber threats and regulatory termination.
🔍 Explore More: See all tech guides and tutorials for step by step guide pfSense CUI boundary protection setup tutorial.
Check out TECH Collection Amazon Products