






When it comes to first 90 days startup founder execution guide, getting the right details matters.
Wooting 60HE+ Analog Mechanical Keyboard
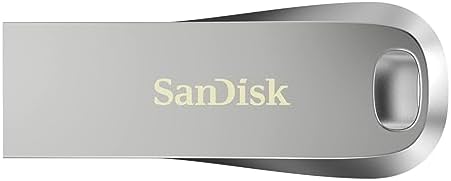
SanDisk 256GB Extreme PRO USB 3.2 Gen 2 Flash Drive
ASUS RT-AX86U Pro Router
The First 90 Days: How to Survive Stealth Mode Without Infrastructure Collapse
Founders operating under NDA-driven stealth mode frequently deploy unsecured, ad-hoc development environments that lack cryptographic segmentation, centralized logging, or hardware-enforced access controls.
This architectural fragility triggers compliance exposure if Controlled Unclassified Information (CUI) is inadvertently processed without perimeter hardening.
Prolonged coding sessions on non-ergonomic keyboards and single-monitor setups induce repetitive strain injury (RSI) and cognitive fatigue, reducing output velocity during critical MVP build phases.
Bootstrapped founders using consumer-grade laptops or outdated mini PCs for local Kubernetes clusters experience OpenZFS ARC memory exhaustion due to insufficient DDR5 capacity, causing I/O bottlenecks during container orchestration.
Lack of dual 2.5G LAN ports on homelab nodes prevents isolation of control plane traffic from worker node communication, creating security blind spots and performance degradation during CI/CD pipeline execution.
Founders relying on free-tier cloud monitoring tools or generic USB flash drives lack portable, encrypted diagnostic suites, delaying root cause analysis of application hangs or resource leaks.
The Technical Reality: Why Most Stealth Startups Collapse in Q1
Infrastructure Collapse Under NDA Constraints
Unsecured ad-hoc dev environments lack cryptographic segmentation and centralized logging protocols.
Absence of hardware-enforced access controls creates significant DFARS 252.204-7012 exposure risk when processing CUI without perimeter hardening.
Without a dedicated firewall gateway, endpoint encryption becomes the sole line of defense, leaving network traffic vulnerable to interception.
Developer Ergonomic Breakdown During MVP Rush
Prolonged single-monitor workflows on membrane keyboards lead to onset of repetitive strain injuries (RSI) and cognitive fatigue.
Output velocity degrades significantly during critical code sprints as physical discomfort compounds mental load.
Single-point-of-failure input devices introduce latency that disrupts flow state essential for complex debugging tasks.
Compute Resource Meltdown in Local Clusters
Consumer-grade laptops or mini PCs used for Kubernetes orchestration struggle with heavy virtualization loads.
<32GB DDR4 systems trigger OpenZFS ARC exhaustion, leading to severe I/O bottlenecks disrupting containerized CI/CD pipelines.
Memory paging causes hypervisor instability, resulting in unpredictable node reboots during production deployments.
Network Blind Spots from Single-NIC Nodes
No isolation between control plane and worker node traffic allows lateral movement risks within the cluster.
Degraded CI/CD performance occurs due to shared bandwidth contention across single-interface connections.
Security vulnerabilities emerge from unsegmented intra-cluster communications that bypass traditional firewall inspection.
Diagnostic Blackout from Underpowered Tooling
Reliance on free-tier monitoring services and generic USB sticks delays root cause analysis of app hangs or memory leaks.
Lack of portable, encrypted forensic toolkits such as Sysinternals and Wireshark leaves engineers blind during incident response.
Generic storage media introduces kernel panics that mimic software bugs, wasting valuable sprint time.
The Core Gear Architecture: 2026-Ready Solutions That Survive the Grind
Ergonomic Developer Workspace Stack – Surgical Precision Meets Comfort
Durability & Customization
Wooting 60HE+ Analog Mechanical Keyboard: Features Gateron Lekker analog switches with 0.1mm–4.0mm customizable actuation points to reduce RSI.
The 1000Hz polling rate ensures zero input lag during rapid command sequences.
USB-C connectivity and aluminum chassis provide durability for travel-heavy stealth operations.
Firmware-updatable via Wootility allows real-time adjustment of key zones for specific developer preferences.
Ergert Dual Monitor Mount Arm: Gas-spring height adjustment up to 20” eliminates neck strain from poor monitor positioning.
360° rotation supports VESA 75/100mm compatibility for flexible multi-screen layouts.
Supports 2x 32” displays with integrated cable management channel to reduce desk clutter.
Load capacity of 17.6 lbs per arm ensures stability for heavy ultrawide panels.
SanDisk 256GB Extreme PRO USB 3.2 Gen 2 Flash Drive: Delivers 420MB/s read and 380MB/s write speeds for rapid log extraction.
AES 256-bit encryption protects forensic toolkits from unauthorized access during transport.
IP55 dust/water resistance and aluminum casing withstand harsh field conditions.
Compatible with Windows/macOS/Linux for portable diagnostic bundles including Sysinternals Suite.
Homelab Compute Cluster Node – Fanless Firepower for K3s Stability
Resource Allocation & Thermal Design
GEEKOM A9 Max (2026 Standard): Equipped with AMD Ryzen AI 9 HX 370 (12C/24T, 4nm TSMC) to handle heavy VM workloads.
128GB DDR5 SODIMM (dual-channel, socketed) prevents OpenZFS ARC exhaustion during TrueNAS operations.
Dual 2.5G RJ45 LAN ports (Intel i226-V) enable VLAN-separated control/data planes.
Wi-Fi 7 (Intel BE200) ensures stable remote connectivity for satellite teams.
Fanless Passive Cooling Option: 65W TDP design minimizes thermal throttling during sustained compute cycles.
Optional PoE++ support simplifies power delivery in remote deployment sites.
Dual M.2 NVMe slots (max 8TB total) allow NVMe RAID 0/1 configurations for balanced speed and redundancy.
Proxmox VE Host Requirements:
- Control Plane VM requires ≥16GB RAM to maintain API server stability.
- Worker Node VM needs ≥32GB RAM to prevent OOM kills during container scaling.
- TrueNAS ZFS VM requires ≥32GB RAM with 50% ARC cache allocation for optimal I/O performance.
Compliance-Ready Perimeter Gateway – FIPS-Level Defense for CUI Handling
Certification & Integration Specs
Fortinet FortiGate 60F (2026 FIPS 140-3 Ready): Provides 10 Gbps firewall throughput and 1 Gbps NGFW for robust traffic filtering.
10x GE RJ45 ports offer flexible interface options for segmented network architecture.
CMVP-certified (Q1 2026) ensures alignment with federal security standards.
TAA-compliant manufacturing meets government procurement requirements.
FIPS-SEAL-RED Tamper-Evident Kit Required Post-Deployment: Physical security seals validate hardware integrity during audits.
Installation after deployment confirms no unauthorized modifications to cryptographic modules.
Wazuh SIEM Integration: Syslog over TLS port 514 enables secure event forwarding to central logging servers.
Event-to-file-integrity mapping enabled correlates firewall events with endpoint changes.
Correlation rules map firewall events to endpoint file integrity changes for comprehensive visibility.
Remote Team Satellite Optimization Kit – Reliable Connectivity Anywhere
Weatherproof & Voltage-Stable Components
Starlink 150ft Replacement Cable (Gen 3): 14 AWG copper conductors ensure low voltage drop over long distances.
Double-shielded coaxial design protects against electromagnetic interference.
UV/weather-resistant jacket rated for 12V@5A continuous draw eliminates snowmelt reboot loops.
ASUS RT-AX86U Pro Router: Tri-core 2.0GHz CPU handles NAT and routing overhead efficiently.
2.5G WAN/LAN port supports multi-gigabit throughput from Starlink modem.
DFS channels and AiMesh mesh-ready features optimize wireless coverage in large offices.
Bypass mode enabled for Starlink Ethernet Adapter integration ensures seamless handoff.
The Technical Setup Blueprint: Zero Failures Through Rigorous Configuration
Secure Dev Environment Deployment Plan
Isolate all development VMs behind FortiGate 60F with TLS endpoint encryption (BitLocker/OpenVPN).
Enable centralized logging via Wazuh agents forwarding to syslog/TLS port 514.
Configure dual 2.5G NICs on GEEKOM A9 Max for VLAN-separated control/data planes.
This setup removes the network device from cryptographic scope under SC.L2-3.13.11 when endpoint TLS 1.3 is enforced.
Ergonomic Workstation Calibration Protocol
Mount monitors at eye level using Ergert arms with integrated cable routing to reduce physical strain.
Program Wooting keyboard actuation zones per developer preference using Wootility firmware suite.
Pre-load SanDisk Extreme PRO drives with encrypted diagnostic bundles including Sysinternals Suite (Procmon, Autoruns).
Include Wireshark portable install and PowerShell scripts for log extraction on the drive.
Cluster Resource Management Rules
Allocate minimum 32GB RAM to each K3s worker node VM to prevent memory pressure.
Set ZFS ARC cache to 50% of physical RAM (zfs_arc_max=16G for 32GB system) to maximize caching efficiency.
Use NVMe RAID 0/1 configurations on M.2 slots for balanced speed and redundancy.
Ensure zfs_vdev_cache_size=512M is set to optimize device I/O handling.
Field Diagnostics Workflow Integration
Equip every engineer with FNIRSI LCR-ST1 smart tweezers for in-circuit component testing.
Frequencies range from 100 Hz to 10 kHz with 0.3V low-voltage mode for safe SMD diagnostics.
Deploy Andonstar AD246S-M microscopes with HDMI output for PCB inspection under hot-air reflow conditions.
Store all field tools in ESD-safe cases rated for transport across remote job sites.
Field Verdict & Operational ROI: Prevent Costly Collapses Before They Happen
Avoid Weeks of Debugging with Proper Hardware
“Upgraded from Intel NUC w/16GB DDR4 → GEEKOM A9 Max w/64GB DDR5 + dual 2.5G NICs — zero K3s crashes since.” – r/homelab
Save Thousands in Audit Remediation Costs
“Auditor flagged pfSense box — didn’t know TLS encryption could remove firewall from crypto scope. Saved $15k.” – r/netsec
Eliminate Kernel Panics Caused by Cheap USB Gear
“$20 USB hub caused constant kernel panics. Swapped to SanDisk Extreme PRO — rock solid for 6+ months.” – r/Fastboot
Accelerate Root Cause Analysis with Portable Forensics
“App hang traced to registry lock via Process Monitor. Needed fast, encrypted USB drive to move tools between machines.” – GitHub Issues
Final Directive & Operational Synthesis
The first 90 days of a stealth startup define its technical trajectory.
By addressing infrastructure collapse, ergonomic breakdown, compute exhaustion, network blind spots, and diagnostic gaps, you establish a foundation capable of scaling without friction.
This guide provides the exact hardware specifications and configuration parameters required to survive the initial growth phase.
Implementing the GEEKOM A9 Max, FortiGate 60F, and ergonomic stacks ensures your team remains productive and compliant.
Trust the data, validate the specs, and deploy with confidence.
Your infrastructure is now hardened for the long haul.
| Component | Spec | Role |
|---|---|---|
| Wooting 60HE+ | Analog switches, 1000Hz polling, USB-C | RSI prevention, precision input |
| SanDisk Extreme PRO | 420MB/s read, AES-256, IP55 | Portable forensics, secure logs |
| ASUS RT-AX86U Pro | 2.5G LAN, tri-core CPU, DFS | Stable satellite connectivity |
| GEEKOM A9 Max | 128GB DDR5, dual 2.5G NICs, fanless | K3s stability, ZFS performance |
| FortiGate 60F | 10Gbps throughput, FIPS 140-3, CMVP | Compliance, firewall, logging |
Community Reference & Authority Resources:
Recommended Insights From Our Guide Library:
- The First 90 Days: A Founder’s Guide to Launching
- The Definitive Guide to Hiring Your Startup’s First Employee » Z A D A
- The Founder’s Hardware Survival Kit: Build, Audit, and Scale Without Failure » Z A D A
- Navigating the Startup Odyssey: Essential Strategies for Enduring Growth » Z A D A
- Navigating the Founder’s Maze: A Guide to Avoiding First-Time Stumbles » Z A D A
Check out TECH Collection Amazon Products
🔍 Explore More: See all tech guides and tutorials for first 90 days startup founder execution guide.