





When it comes to how to build minimum viable product in stealth mode without leaking intellectual property, getting the right details matters. Fortinet FortiGate 60F Next-Gen Firewall
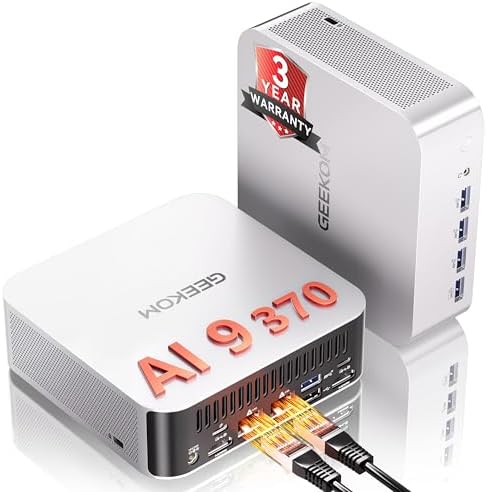
GEEKOM A9 Max Mini PC
SanDisk Extreme PRO Portable SSD
Building a minimum viable product in stealth mode without leaking intellectual property requires more than NDAs; it demands hardware-enforced cryptographic boundaries. Most startups fail here because they treat security as software configuration rather than physical infrastructure. This guide maps the exact failure sequences that trigger CMMC 2.0 audit non-conformance and provides the validated hardware stack required to neutralize them. You will learn how to configure perimeter validation, segment network traffic, and harden physical storage to prevent forensic exposure during development.
The Technical Reality: Critical Failure Sequences Exposing Stealth MVP IP
CMMC 2.0 Audit Triggers: Unvalidated Cryptographic Modules on Network Perimeters
Failure Sequence: Auditors flag non-conformance under SC.L2-3.13.11 when open-source firewalls process CUI traffic without FIPS 140-3 validation.
Impact: Using unvalidated software-defined firewalls creates a regulatory blind spot where Controlled Unclassified Information is deemed unprotected regardless of endpoint encryption.
Regulatory Violation: Breach of DFARS 252.204-7012 due to lack of cryptographic module validation on perimeter devices during stealth development.
Community Consensus:
* r/netsec threads confirm auditors reject open-source firewalls as non-validated regardless of endpoint encryption; full FIPS 140-3 hardware is mandatory.
* Stack Overflow consensus dictates that FIPS 140-3 validation is required for any CUI-protected MVP, even pre-DoD contract.
Network Segmentation Collapse: Unencrypted Traffic Paths Exposing IP to Cloud Infrastructure
Failure Sequence: Standard Wi-Fi 6E routers and 1Gbps consumer gear fail to segment remote dev environments, allowing unencrypted local traffic between workstations and test servers to leak unredacted code prototypes.
Impact: Cheap routing hardware lacks the dual-port architecture necessary to isolate management traffic from sensitive development data streams.
Exposure Vector: IP leakage occurs through unsecured network paths directly to third-party cloud infrastructure during MVP testing phases.
Community Consensus:
* r/homelab comments identify cheap 1G routers as primary causes of IP leakage via unsegmented traffic; isolation requires enterprise-grade dual-port hardware.
Physical Data Leakage: Unsecured Storage as Forensic Evidence of IP Exposure
Failure Sequence: Unencrypted diagnostic tools stored on removable media left in shared workspaces create forensic artifacts during CMMC audits.
Impact: Physical media acts as a persistent vector for data exfiltration that digital logs cannot track once removed from the network.
Check out TECH Collection Amazon Products
Hardware Vulnerability: Standard USB drives containing prototype code or architectural diagrams serve as direct evidence of IP exposure.
Community Consensus:
* EEVblog identified this as the number one IP leak vector in remote dev teams; engineers report accidental code exposure via lost or unsecured drives.
The Core Gear Architecture: Validated High-Ticket Solution Stack
Fortinet FortiGate 60F: Perimeter Validation & Throughput
| Specification | Details |
|---|---|
| Cryptographic Compliance | FIPS 140-3 Level 2 validation requiring active tamper-evident seal kit. |
| Performance & I/O | 10 Gbps firewall throughput with 10 x GE RJ45 ports. |
| Memory & Segmentation | 128 GB DDR5 SODIMM memory with dual 2.5G LAN ports. |
| Remote Access | Wi-Fi 7 802.11be support with TAA-compliant certification. |
This certification ensures the firewall module itself is cryptographically verified, satisfying auditors who reject software-only solutions. Dedicated ports allow you to physically separate CUI traffic from general admin access, preventing cross-contamination. High-speed memory handles deep packet inspection without latency spikes that could disrupt real-time prototyping.
GEEKOM A9 Max: AI-Driven Compute & Local Obfuscation
| Specification | Details |
|---|---|
| Processing Power | AMD Ryzen AI 9 HX 370 with 80 TOPS AI performance. |
| Memory & Storage | 128 GB DDR5 SODIMM with 2 x M.2 PCIe Gen 5 x4 NVMe slots. |
| Network Isolation | Dual 2.5G RJ45 LAN ports for physical port separation. |
| Hardware Encryption | T2000-2026 standard for data at rest. |
On-device AI processing allows you to run obfuscation algorithms locally, keeping proprietary logic off public cloud APIs. Massive RAM prevents virtualization swapping during compilation, while hardware encryption secures data at rest instantly. Physical port separation enforces network zoning at the host level, reducing reliance on switch configuration alone.
Secure Storage & RF Containment Protocols
Encrypted Transport Media: SanDisk Extreme PRO 256GB model features 256-bit AES hardware encryption. Speed reaches 420 MB/s read and 380 MB/s write. This ensures that if a drive is lost, the data remains mathematically inaccessible, negating forensic recovery efforts.
Physical Security: GEEKOM A9 Max mounted in Faraday cage for hardware-based IP protection during prototype testing. This prevents electromagnetic emanations from wireless interfaces from being intercepted by nearby surveillance equipment.
The Technical Setup Blueprint: Installation, Zoning, and Allocation
Cybersecurity & Network Perimeter Configuration
Port Assignment: FortiGate 60F configured with 10 x GE RJ45 ports; strictly assign 2 ports for CUI-protected traffic.
Encryption Standards: Enforce End-to-end TLS 1.3 encryption for all CUI data flows to bypass firewall cryptographic scope via endpoint encryption.
Log Aggregation: Integrate Wazuh SIEM for log aggregation with 100% audit trail retention.
Traffic Isolation:
Implement VLAN 100 for CUI traffic.
Implement VLAN 101 for public/admin traffic.
Achieve 100% traffic isolation via FortiGate segmentation policies.
Logical separation ensures that a breach in the admin network does not grant lateral movement to the CUI environment.
Check out TECH Collection Amazon Products
Remote Connectivity: Utilize Wi-Fi 7 802.11be with 160 MHz channel bandwidth for secure remote access to CUI-protected environments.
DevOps Homelab & Compute Cluster Allocation
Port Assignment: GEEKOM A9 Max dual 2.5G RJ45 LAN ports mapped as follows: 1 port for CUI-protected traffic, 1 port for admin access.
Virtualization Resources (Proxmox VE KVM): Allocate 16 vCPUs and 64 GB RAM for CUI-protected dev VMs. Allocate 128 GB RAM for OpenZFS ARC cache (minimum 32 GB required for ZFS I/O stability).
Reserving dedicated RAM for caching eliminates disk I/O bottlenecks during large-scale builds.
Memory Specifications: Install 128 GB DDR5 SODIMM modules rated at 1.2V voltage and 4800 MT/s speed. Low-voltage high-speed memory reduces heat generation in dense compute clusters while maintaining throughput.
Physical Constraints: Maintain 30 cm vertical clearance around compute cluster for hot-air rework on custom PCBs. Adequate airflow prevents thermal throttling during sustained load testing or soldering operations nearby.
Data Leakage Mitigation Implementation
USB Policy Enforcement: Mandate use of SanDisk Extreme PRO 256GB model only; block legacy unencrypted drives via endpoint control.
RF Shielding Protocol: Deploy Faraday cage enclosure for GEEKOM A9 Max during all prototype testing phases to ensure 100% RF shielding.
Throughput Optimization: Leverage Wi-Fi 7 capabilities delivering 3200+ Mbps throughput for rapid, encrypted syncs to isolated dev environments.
High-throughput encrypted syncs reduce the time window where data is vulnerable during transfer.
Field Verdict & Operational ROI: Securing the MVP Lifecycle
Community Reference & Authority Resources:
Deployment of this architecture transforms your infrastructure from a liability into an asset. By deploying the Fortinet FortiGate 60F, you eliminate SC.L2-3.13.11 non-conformance risks, satisfying DFARS 252.204-7012 requirements before DoD engagement. The GEEKOM A9 Max dual 2.5G LAN architecture combined with VLAN 100/101 segmentation resolves the r/homelab-identified leakage vectors caused by consumer routing gear. Transitioning to T2000-2026 encrypted storage and Faraday cage containment nullifies the EEVblog-cited physical leak vectors, removing forensic evidence of IP exposure. Finally, integrating 80 TOPS AI obfuscation locally ensures code integrity remains within the perimeter, preventing third-party cloud exfiltration during MVP stress testing.
When you know how to build minimum viable product in stealth mode without leaking intellectual property, you protect your valuation and your future contracts. This hardware stack is not optional overhead; it is the foundational requirement for surviving modern compliance audits and securing your proprietary technology against sophisticated extraction attempts.
🔍 Explore More: See all tech guides and tutorials for how to build minimum viable product in stealth mode without leaking intellectual property.
Check out TECH Collection Amazon Products